
SIEM + SOAR
Unified SOC command center
- Kafka ingest → detect → correlate → decide inside Core.
- MITRE ATT&CK coverage and 24h detection timeline on one board.
- Built for global SOC teams and MSSP tenants.
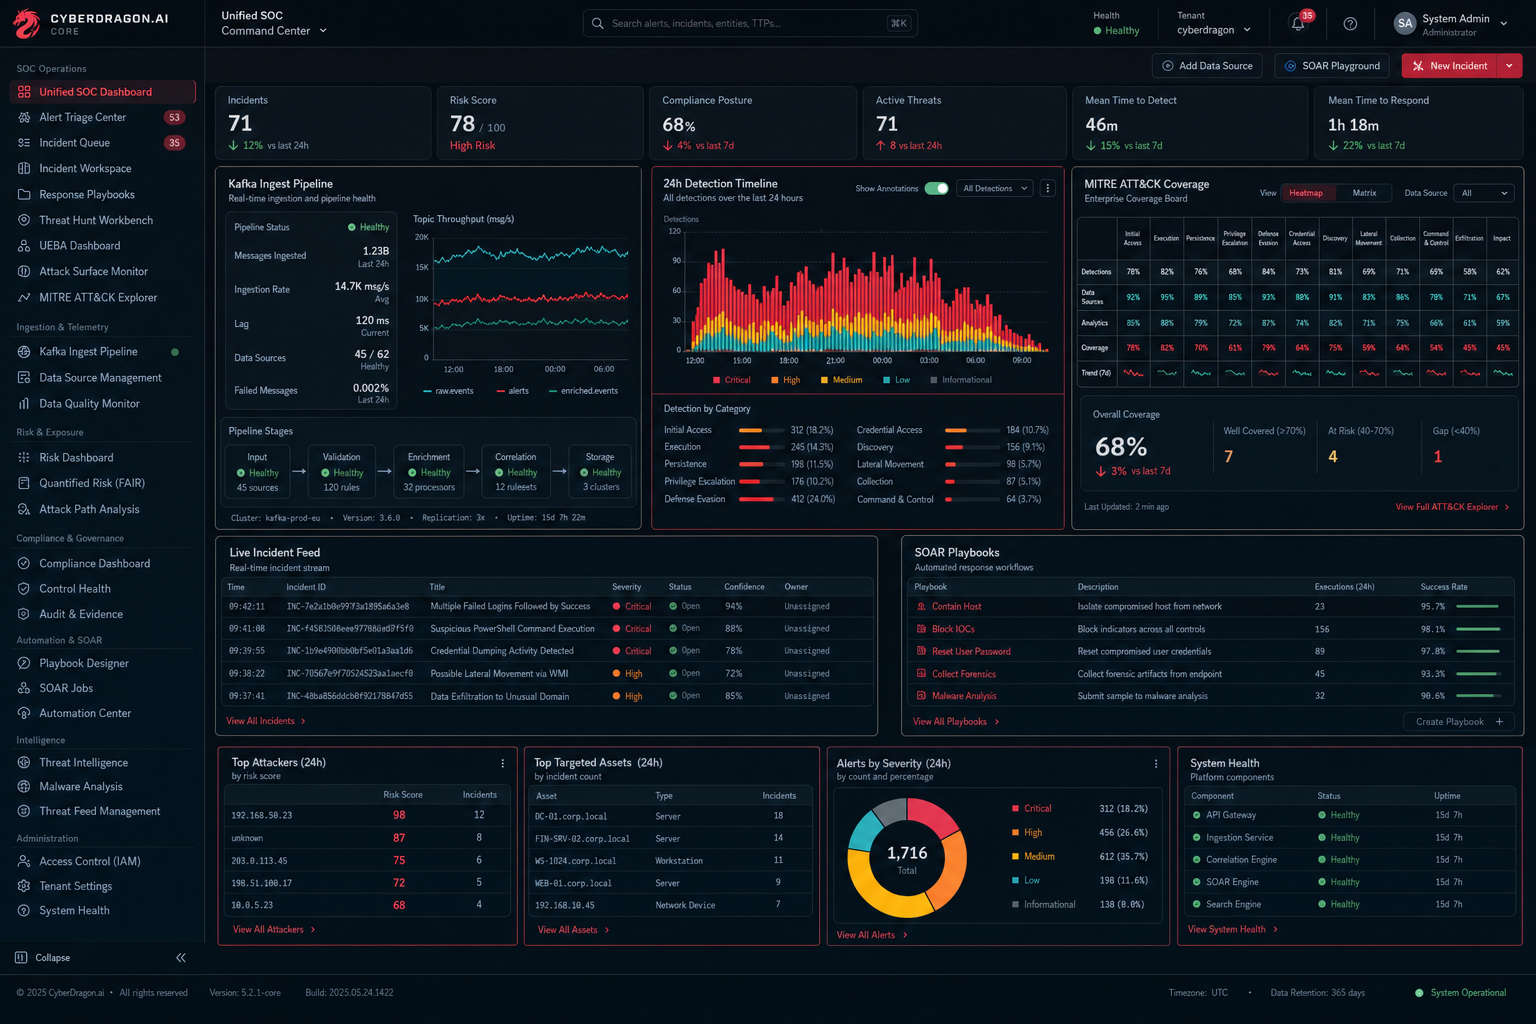
~62 microservices behind a single reverse proxy. Identity, ingest, threat intel fusion, kill-chain detection, risk, compliance, Temporal-orchestrated response, and a tamper-evident evidence vault. Layout and theme are distinct from Edge.
Core never pushes control into Purdue process networks. Edge is passive-first.
OT-affecting automation requires both. Policy can deny even after analyst approval.
Hybrid ML-DSA-65 + Ed25519 JWTs. No third-party IdP dependency for core sessions.
Hash-chained, Ed25519-signed vault with ZIP export for auditors and regulators.
SIEM + SOAR
ML-DSA-65 + Ed25519 hybrid JWTs; MFA; API keys; Vault-backed signing keys.
Cascading W15 (15 min) / W60 (1 hr) / W24 (24 hr) correlation windows.
Explicit signaling when enterprise compromise precedes OT-side anomalies.
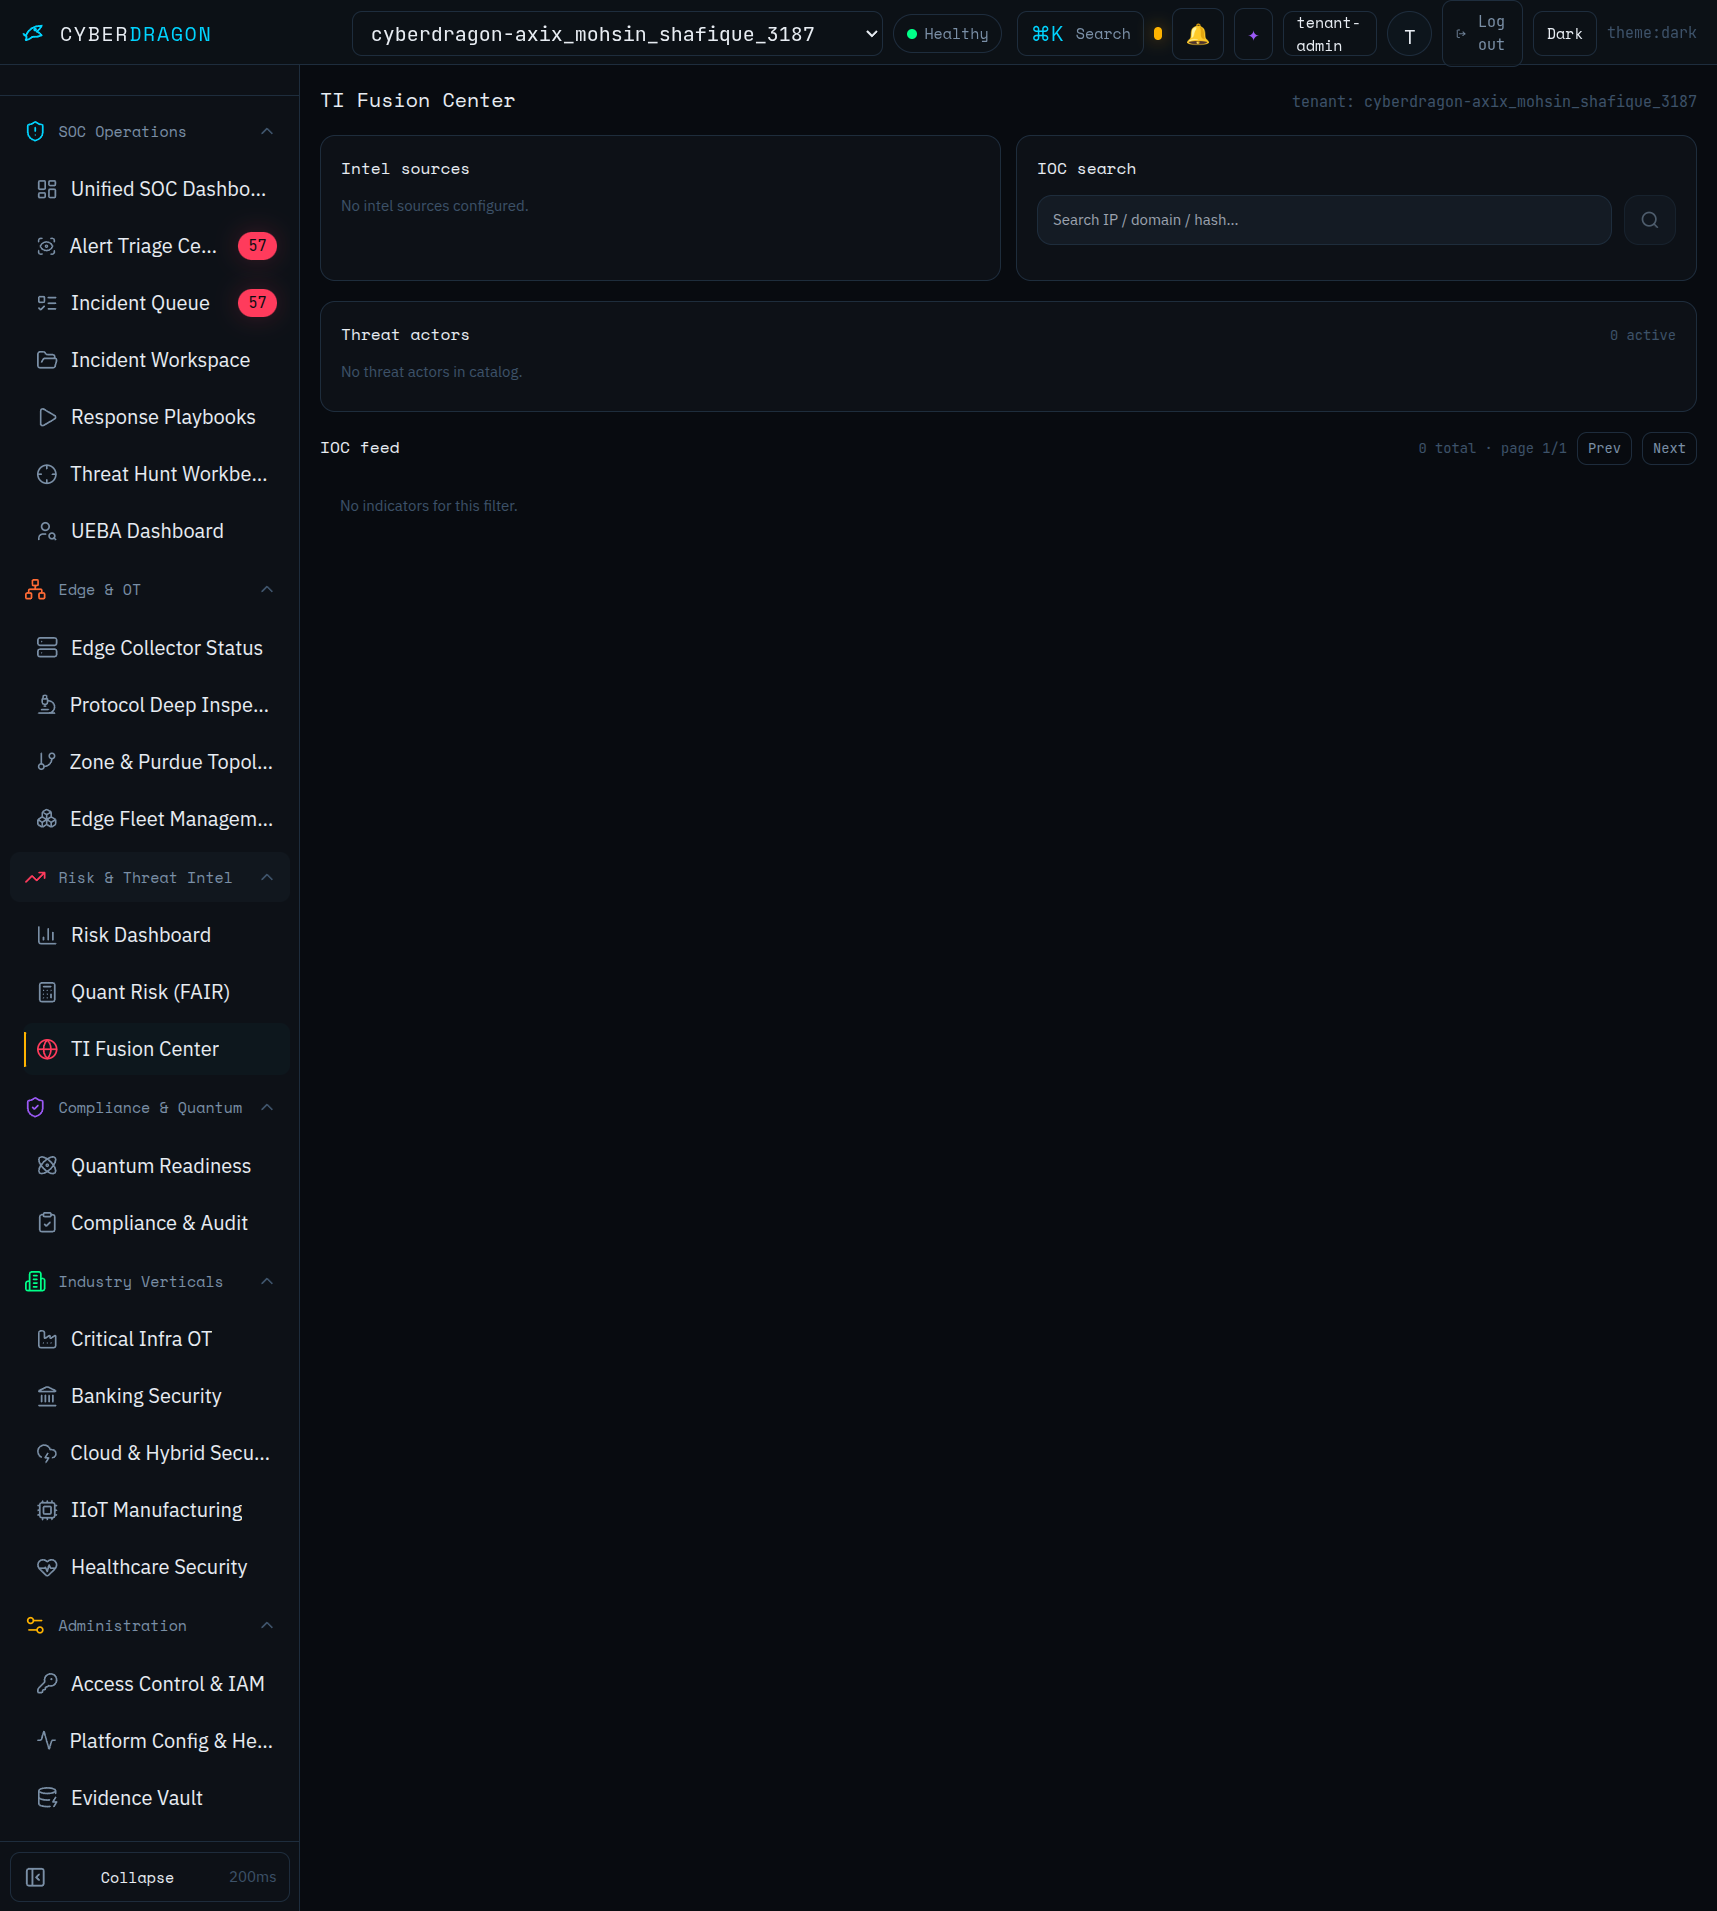
OTX, Abuse.ch, ThreatFox, MITRE TAXII, GreyNoise — in-flight enrichment.
Mirrored NVD/CVE/CPE, CISA ICS-KEV, and OSV for local, offline-safe query.
Asset risk plus FAIR-style scenario scoring, 0–100.
Events mapped to controls automatically — roughly 7 controls per network event.
IEC 62443-3-3, NERC CIP, NIST CSF 2.0, ISO 27001:2022, SOC 2.
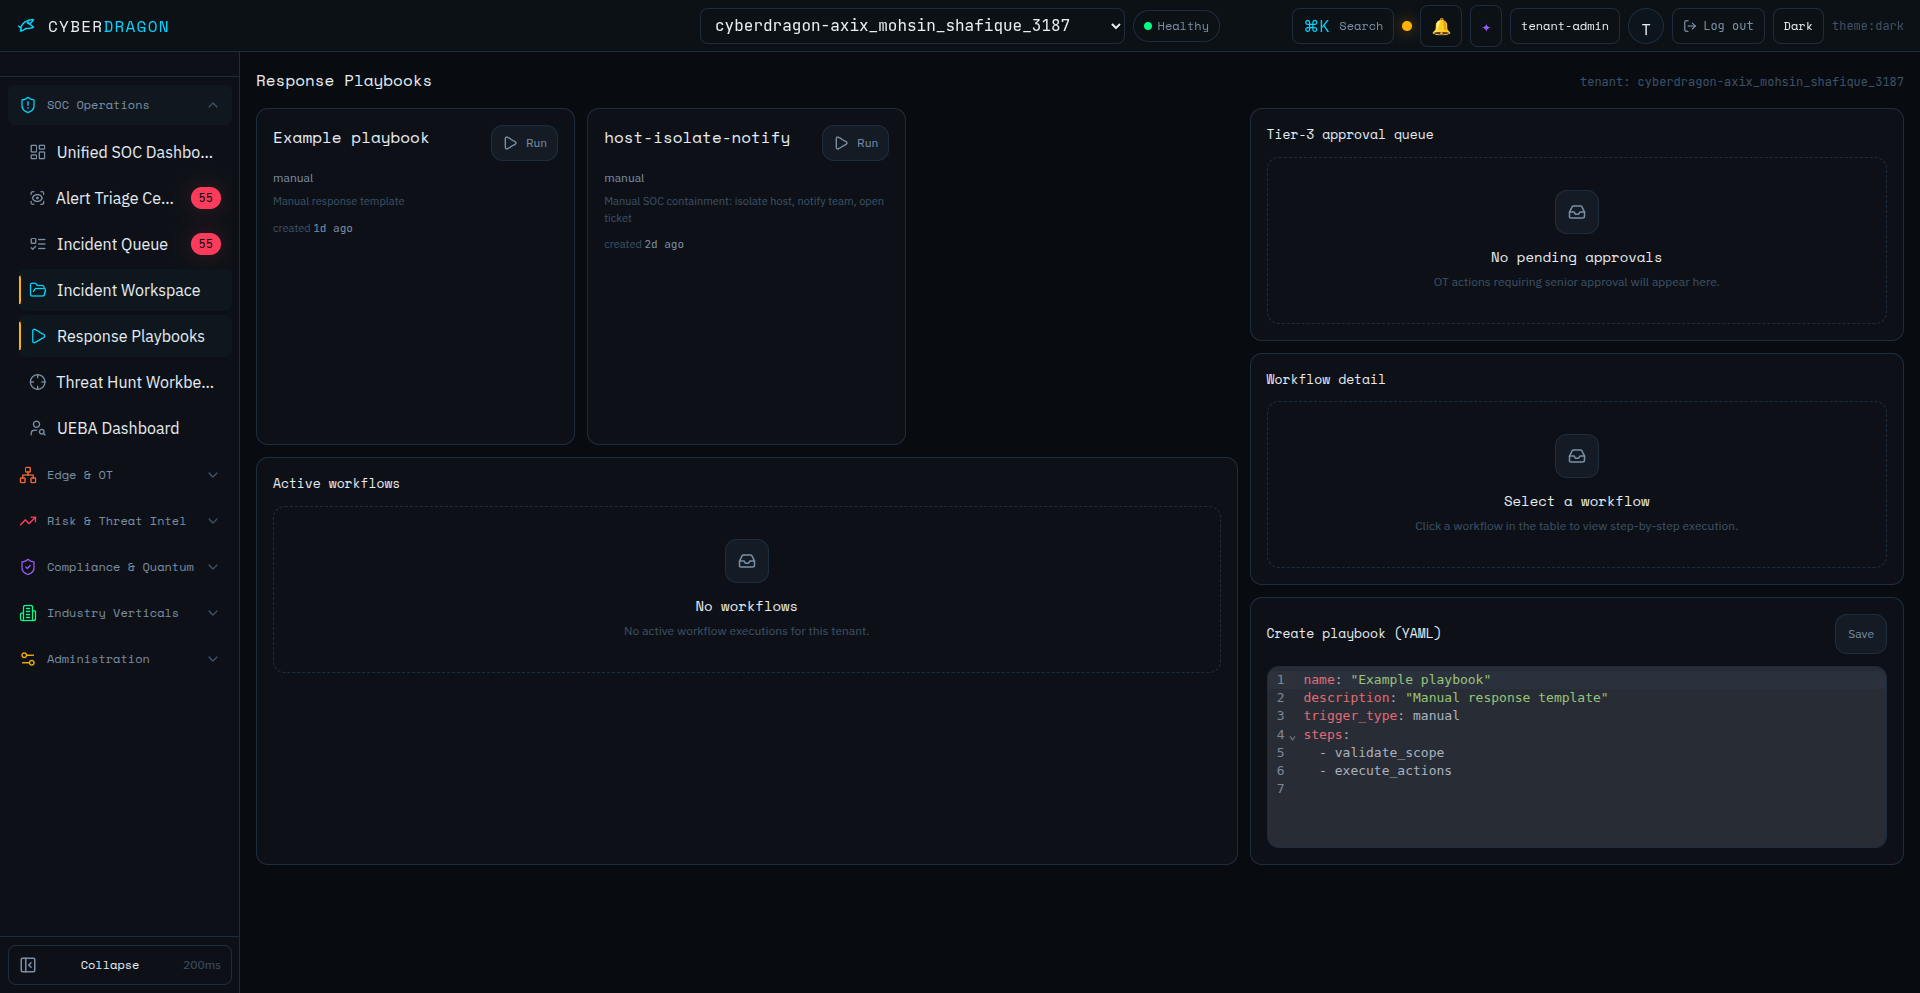
Temporal-orchestrated playbooks with human approval workflows.
OPA policy can deny actions even after human approval on OT-affecting classes.
Hash-chained, Ed25519-signed, tamper-evident audit trail with ZIP export.
Neo4j-backed cyber-physical knowledge graph.
Board PDFs, CISO monthly digests, auditor packets.
Detection packs and partner integration catalog.
Cross-tenant operations, client onboarding, portfolio views.
Response
| Component | Role in the control plane |
|---|---|
| Apache Kafka | Event backbone for ingest, normalization, enrichment, and detection topics. |
| PostgreSQL + RLS | Primary store with row-level security enforcing structural tenant isolation. |
| Neo4j | Cyber-physical knowledge graph powering attack-path and blast-radius queries. |
| Temporal | Durable orchestration for response playbooks and human approval workflows. |
| Open Policy Agent | Platform ABAC plus the OT guardrails that can deny an approved action. |
| HashiCorp Vault | Custody of Ed25519 and ML-DSA-65 signing material. |
| nginx + TLS 1.3 | Single-hostname reverse proxy in front of roughly 62 microservices. |
Threat intel
Edge mirrors traffic from a SPAN port or hardware TAP at the industrial DMZ and parses OT protocols locally.
Events land in a SQLite WAL store-and-forward queue (~5,000 events) so a link outage never loses telemetry.
HMAC-SHA256 signed batches, optionally mTLS, are shipped to Core over the ingest network only.
Threat-intel fusion adds OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise context in flight.
Cascading W15 / W60 / W24 windows assemble events into kill chains and flag Enterprise→OT pivots explicitly.
Risk scoring, compliance auto-mapping, and Temporal playbooks with human approval and OPA guardrails.
Detections, approvals, and denials are hash-chained and Ed25519-signed into the evidence vault.
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.