
Hunt
Threat Hunt Workbench
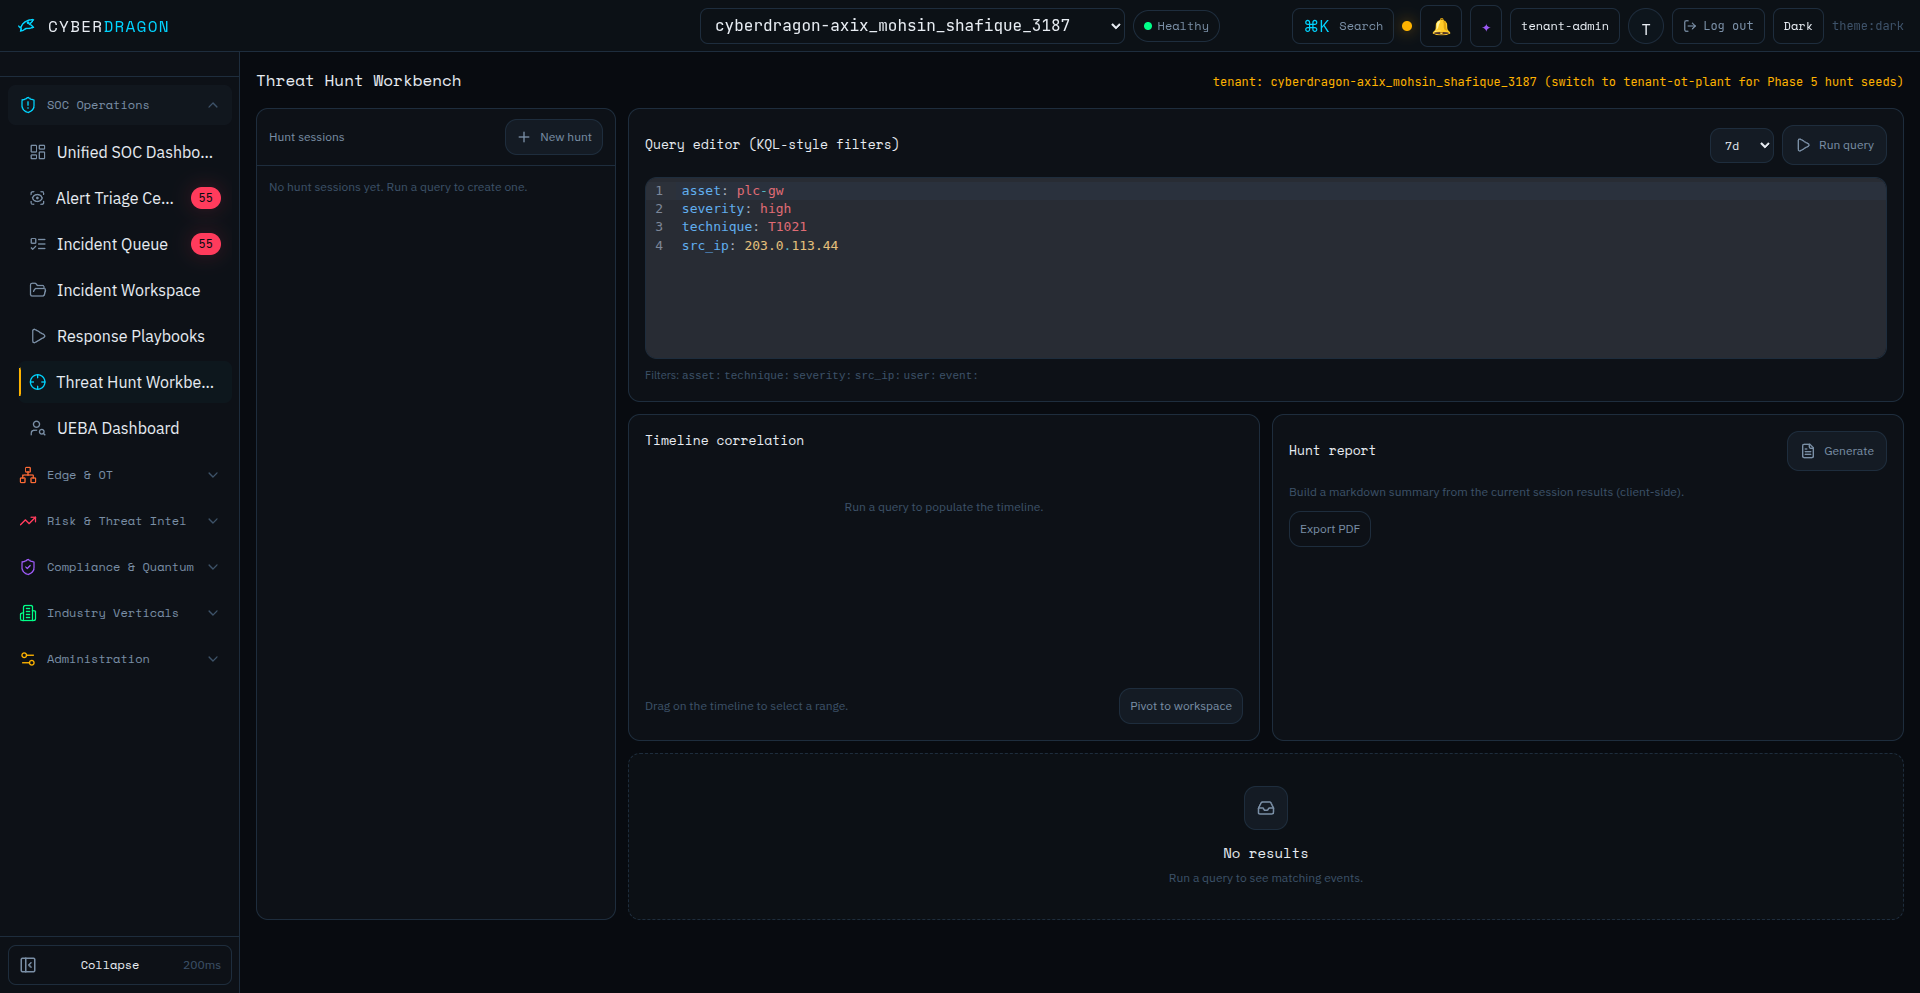
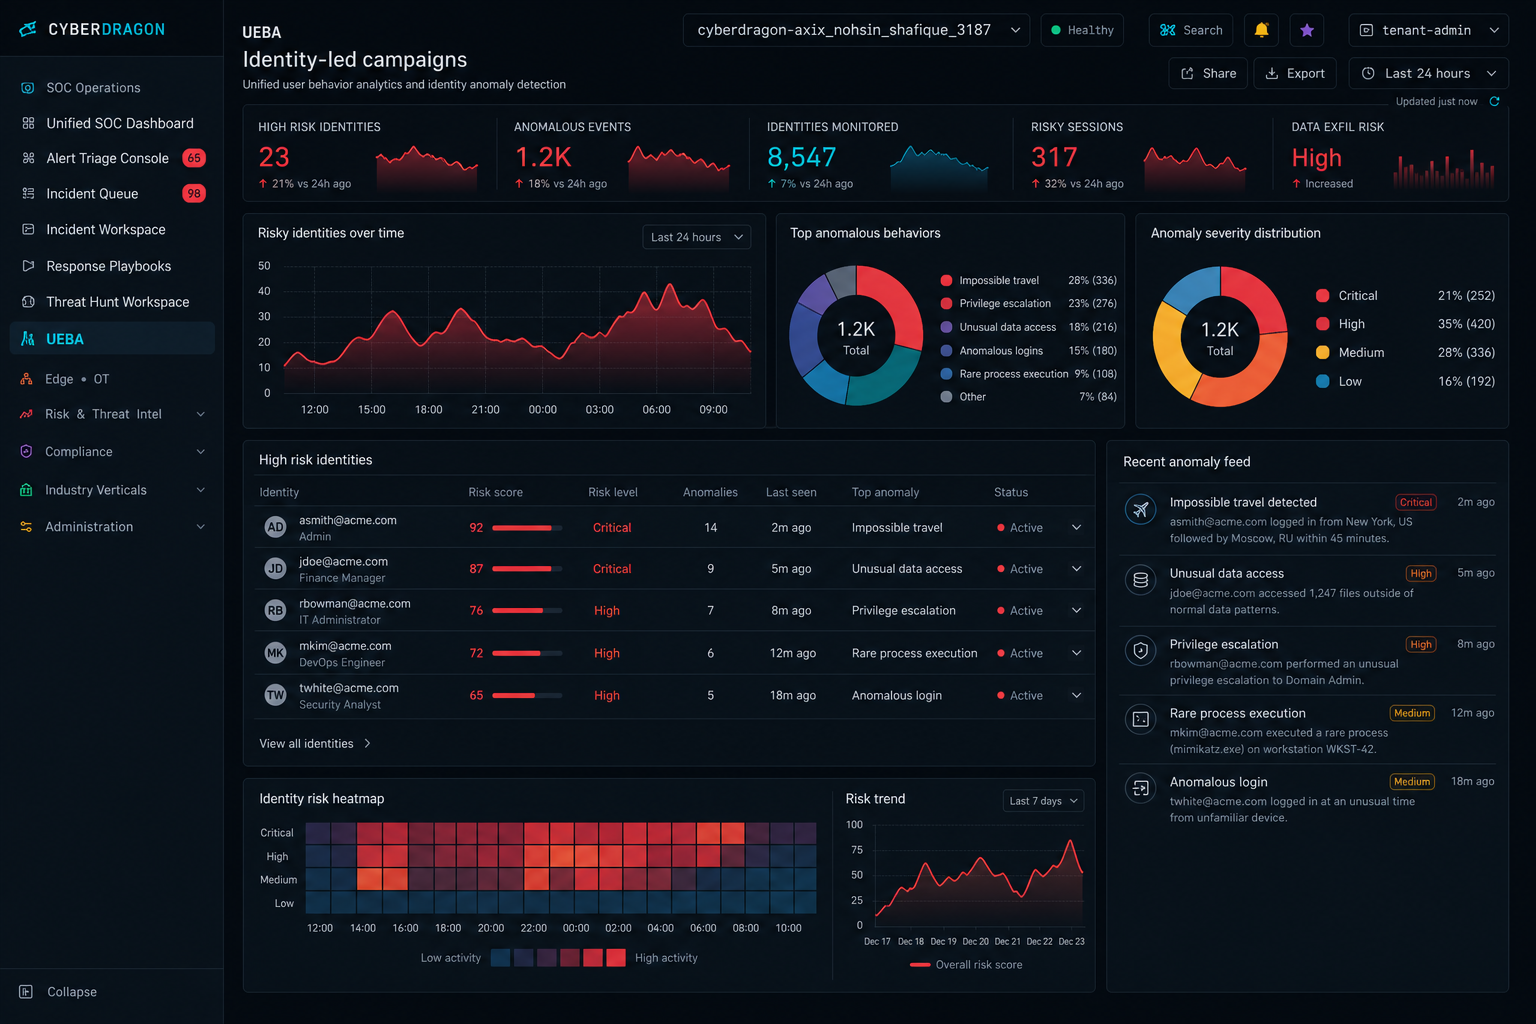
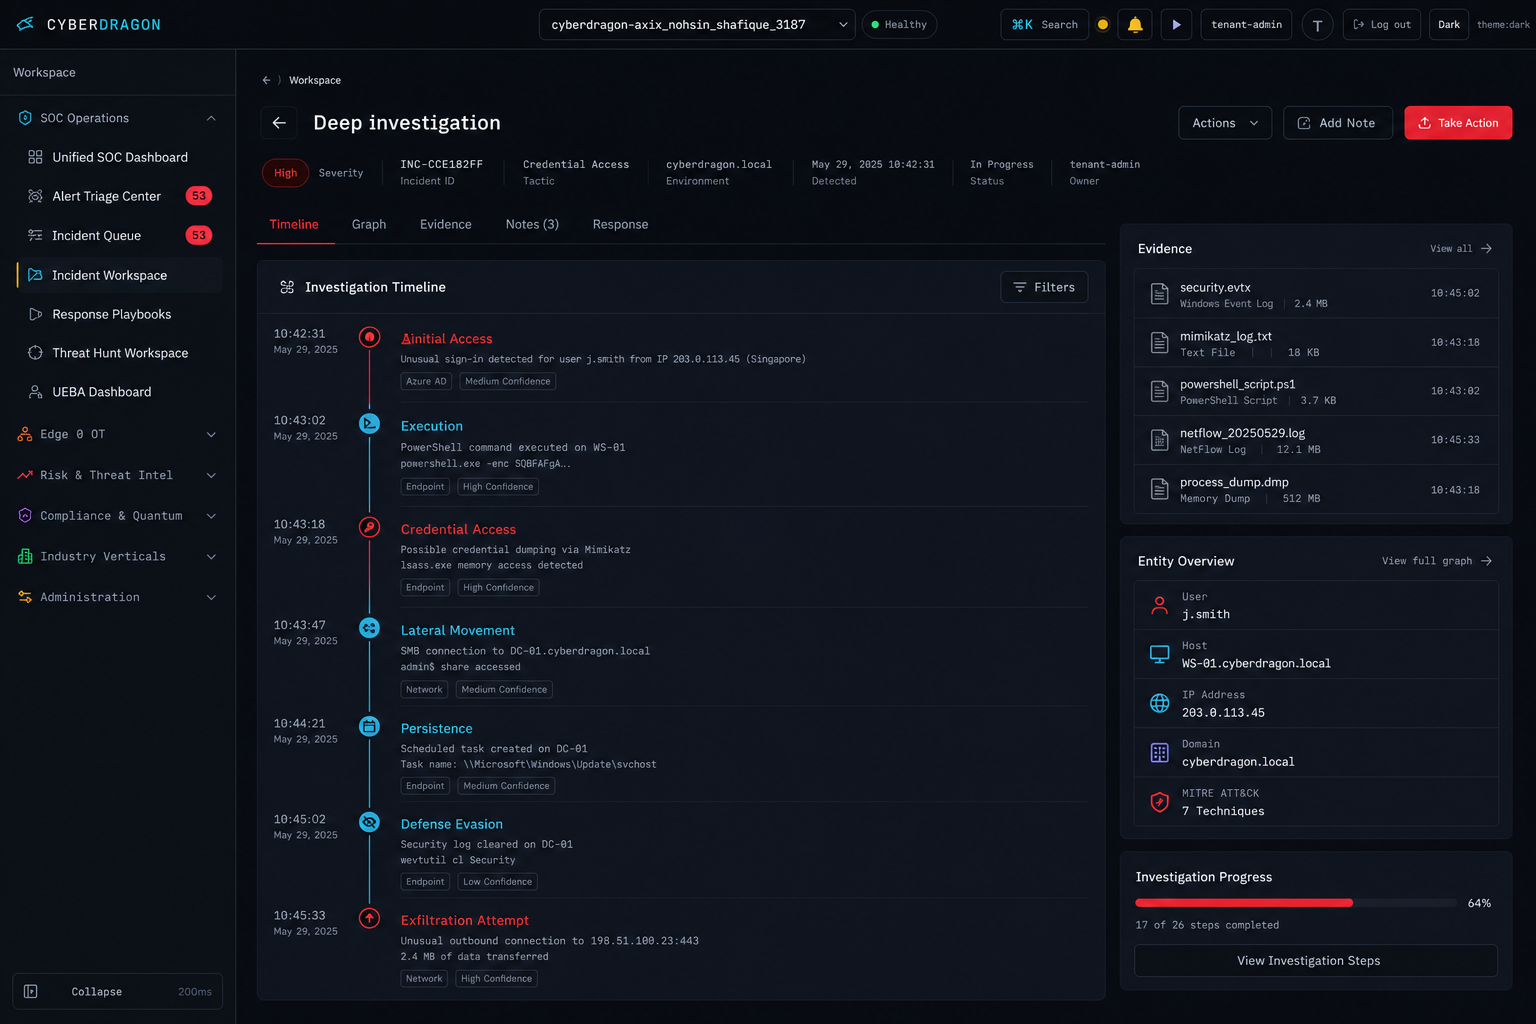
- Proactive hunts on the same corpus as the SOC.
- Senior analysts lead; L1 stays in triage.
- Disclose demo vs live backend honestly in a PoV.
Each use case pairs a detection path with the modules that carry it — from passive capture at the plant to the signed evidence packet.
Correlate a compromised corporate identity to an anomalous Modbus write in one timeline.
Kill-chain detection, Edge, attack-path graph
Passive capture flags a write to a protected register outside a maintenance window.
Edge, OT safety guardrails, evidence vault
TI fusion matches C2 infrastructure before encryption starts on the enterprise side.
TI fusion, W24 window, SOAR
Third-party maintenance sessions tracked against approved windows and asset classes.
Identity, OPA policy, incident queue
Auto-mapped controls exported as a signed auditor packet at quarter close.
Compliance auto-mapper, evidence vault, reporting
Agentless asset identification finds unsupported firmware without touching the device.
Edge, VSI, risk engine
New industrial tenant provisioned with RLS isolation and framework packs in days.
MSSP portal, tenant admin
Crypto inventory and hybrid PQC session tokens evidence crypto agility today.
Sovereign identity, quantum readiness
Hunt
UEBA
Every use case on this page rides the same seven-stage pipeline. Nothing on the path opens a write channel into the process network.
Edge mirrors traffic from a SPAN port or hardware TAP at the industrial DMZ and parses OT protocols locally.
Events land in a SQLite WAL store-and-forward queue (~5,000 events) so a link outage never loses telemetry.
HMAC-SHA256 signed batches, optionally mTLS, are shipped to Core over the ingest network only.
Threat-intel fusion adds OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise context in flight.
Cascading W15 / W60 / W24 windows assemble events into kill chains and flag Enterprise→OT pivots explicitly.
Risk scoring, compliance auto-mapping, and Temporal playbooks with human approval and OPA guardrails.
Detections, approvals, and denials are hash-chained and Ed25519-signed into the evidence vault.
Workspace
| Role | Primary concern | What they get |
|---|---|---|
| CISO | Board-level risk narrative, quantified exposure, and audit readiness | Executive reporting, FAIR scenario scoring, and signed evidence packets. |
| SOC Manager | Alert quality, MTTD, and analyst throughput | Kill-chain correlation instead of raw alerts, plus playbooks with approval gates. |
| OT / Plant Engineer | Nothing may disturb the process | Passive SPAN capture, no agents on PLCs, no command plane into L0–L2. |
| Compliance Lead | Control coverage and evidence on demand | Auto-mapped IEC 62443, NERC CIP, NIST CSF, ISO 27001, and SOC 2 controls. |
| MSSP Operator | Margin, isolation, and onboarding speed | PostgreSQL RLS tenancy, cross-tenant portfolio views, and white-label options. |
| Auditor | Can this record be trusted? | Tamper-evident hash chain with Ed25519 signatures and reproducible verification. |
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.