CyberDragon Core is live and indigenous SIEM/SOAR with Edge protocol capture. Start a 7-day free trial on your own traffic →
Platform · SIEM + SOAR

An indigenous SIEM and SOAR and not adapters bolted onto a generic one.

Kafka-powered control plane with Temporal playbooks, approval workflows, and OT Safety Gate denials after human approve.

SOAR / Response

SOAR / Response

Temporal-orchestrated playbooks with human approval workflows.

Explore Now →
Explore Now →
Explore Now →

SIEM + SOAR

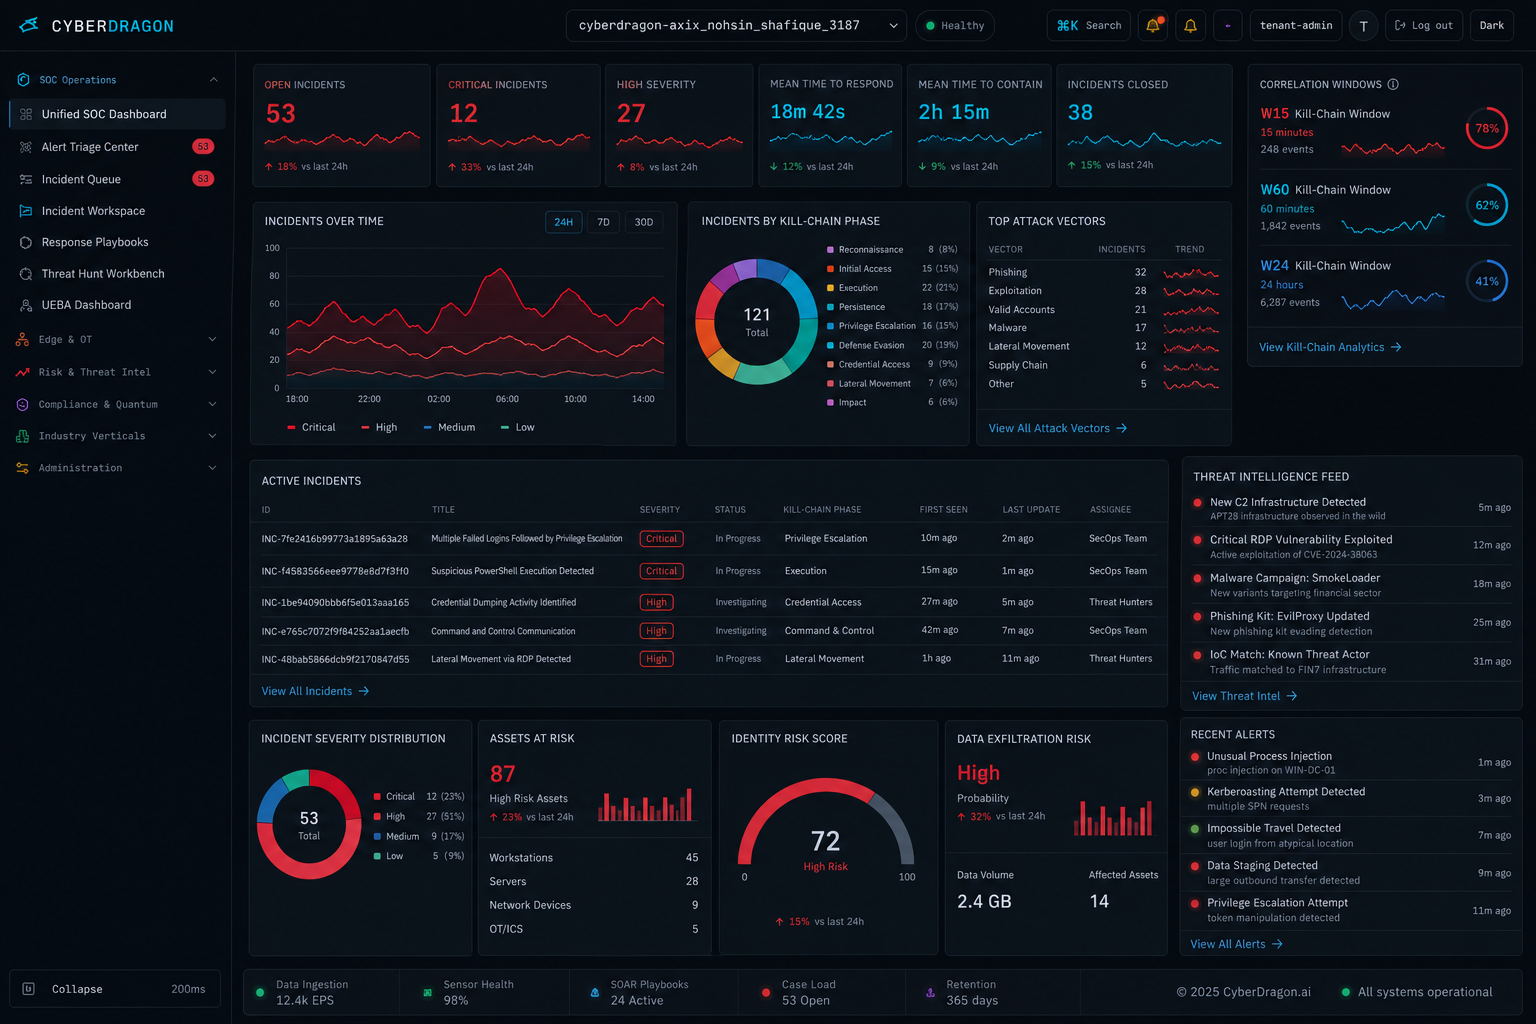
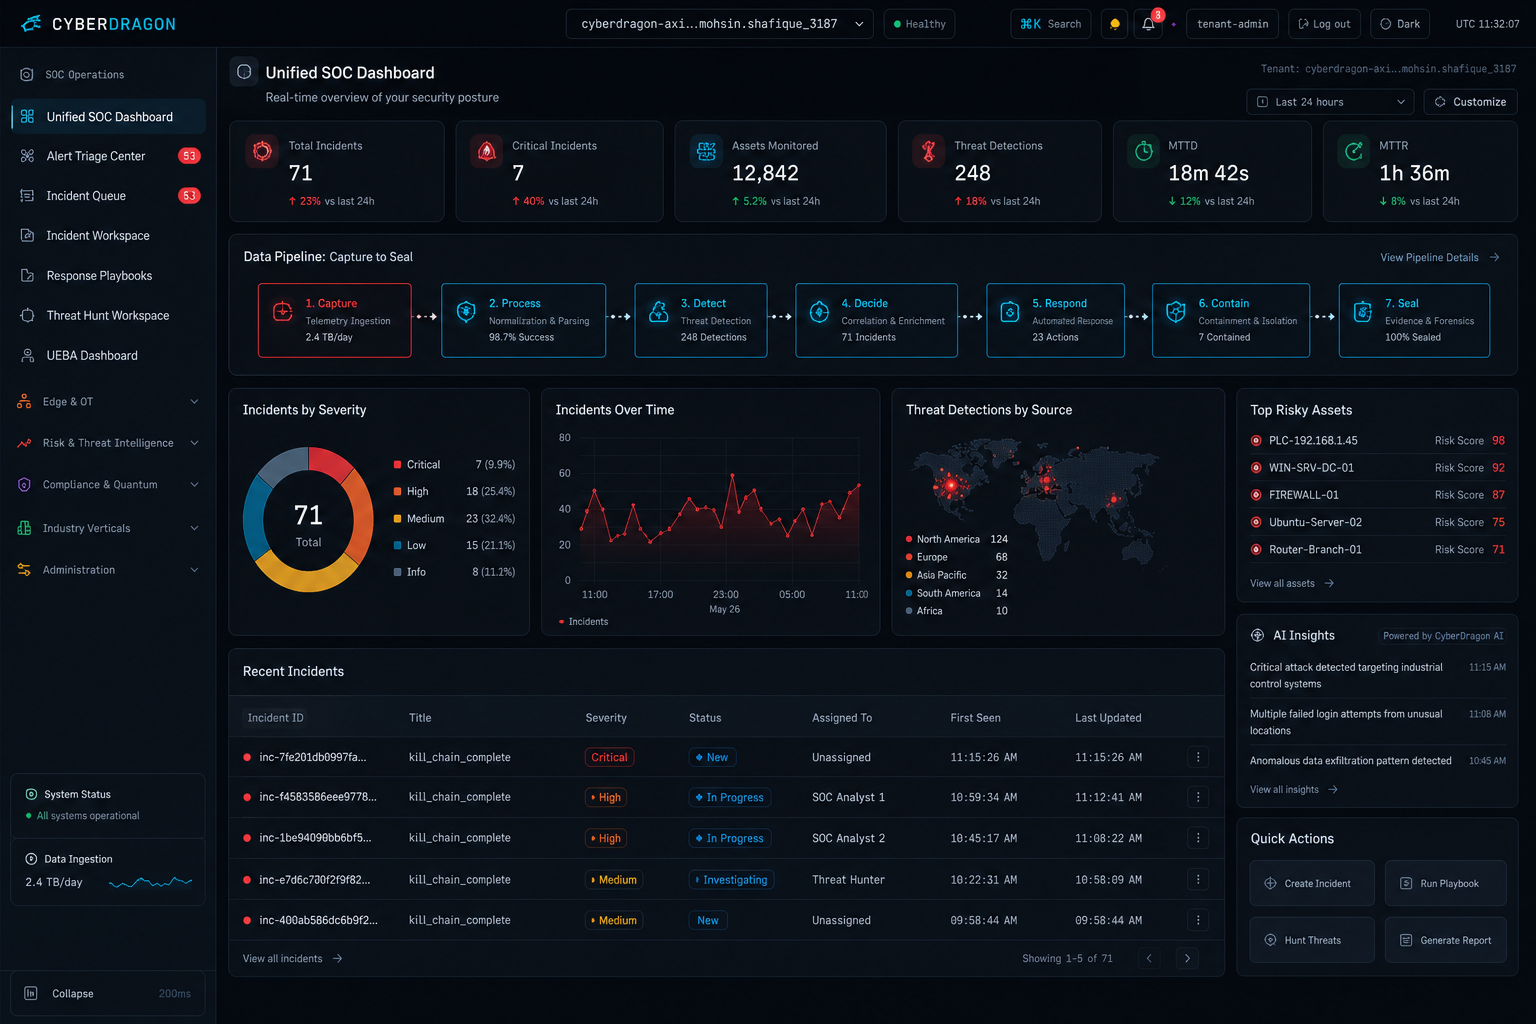
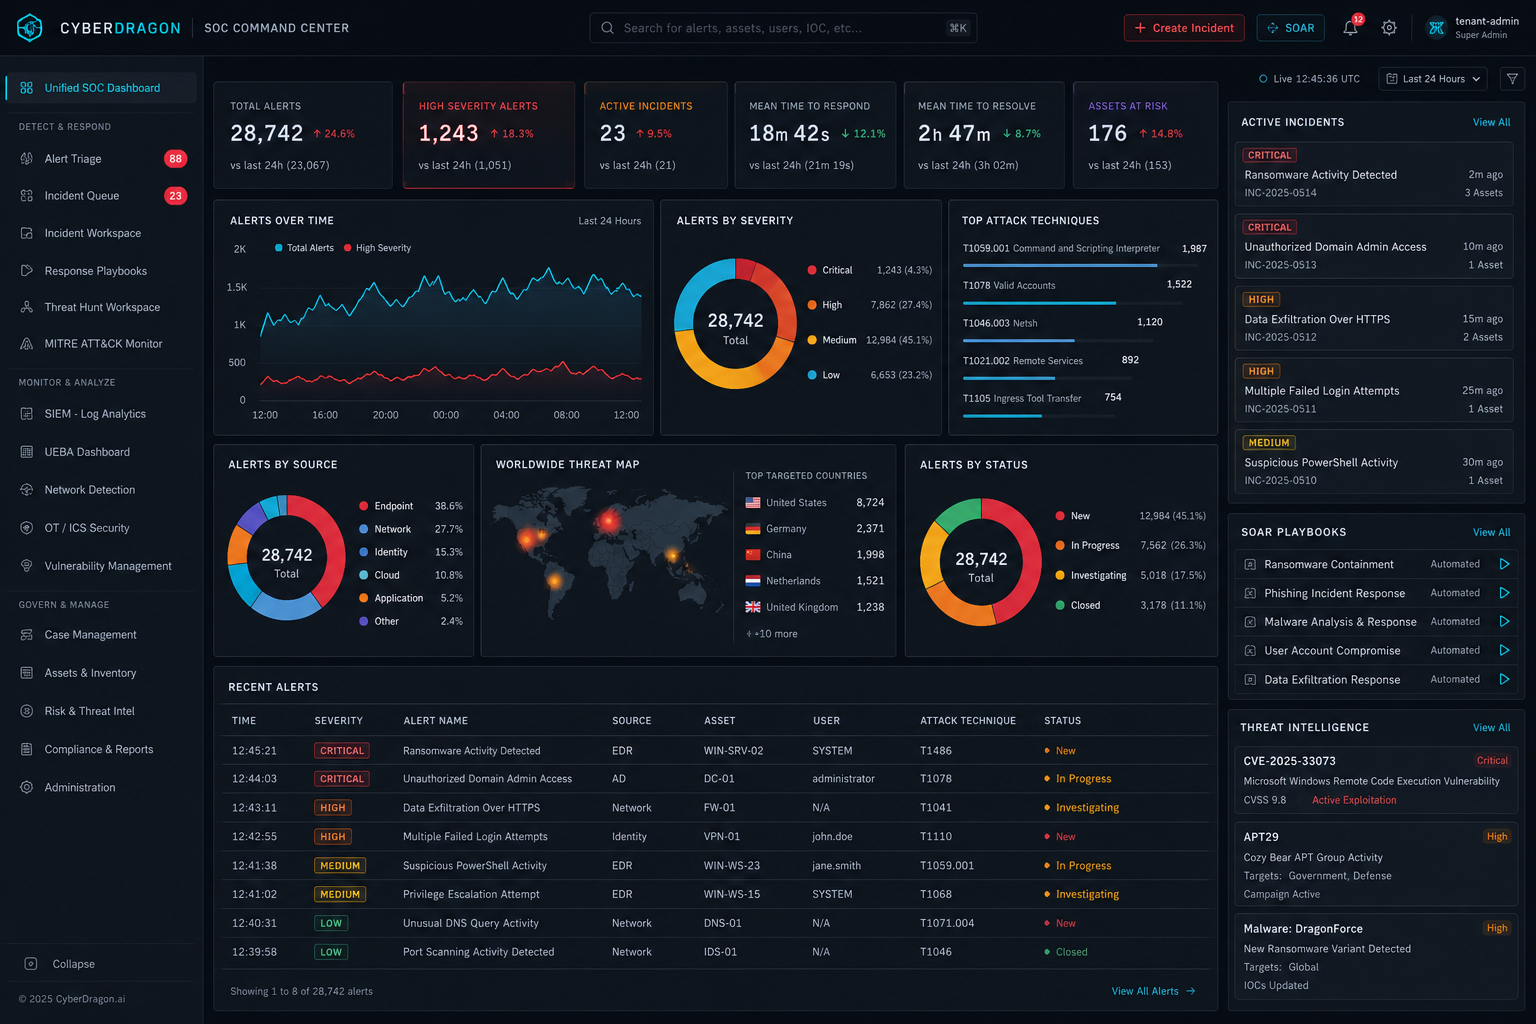
Unified SOC command center

  • Kafka ingest → normalize → detect → correlate → decide, indigenous end to end.
  • Temporal-orchestrated SOAR playbooks with human approval gates.
  • One plane for enterprise and OT and not adapters bolted onto a generic SIEM.
Alert Triage Center
Data pipeline

Capture → buffer → transport → enrich → correlate → decide → seal.

01

Capture

Edge mirrors traffic from a SPAN port or hardware TAP at the industrial DMZ and parses OT protocols locally.

02

Buffer

Events land in a SQLite WAL store-and-forward queue (~5,000 events) so a link outage never loses telemetry.

03

Transport

HMAC-SHA256 signed batches, optionally mTLS, are shipped to Core over the ingest network only.

04

Enrich

Threat-intel fusion adds OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise context in flight.

05

Correlate

Cascading W15 / W60 / W24 windows assemble events into kill chains and flag Enterprise→OT pivots explicitly.

06

Decide

Risk scoring, compliance auto-mapping, and Temporal playbooks with human approval and OPA guardrails.

07

Seal

Detections, approvals, and denials are hash-chained and Ed25519-signed into the evidence vault.

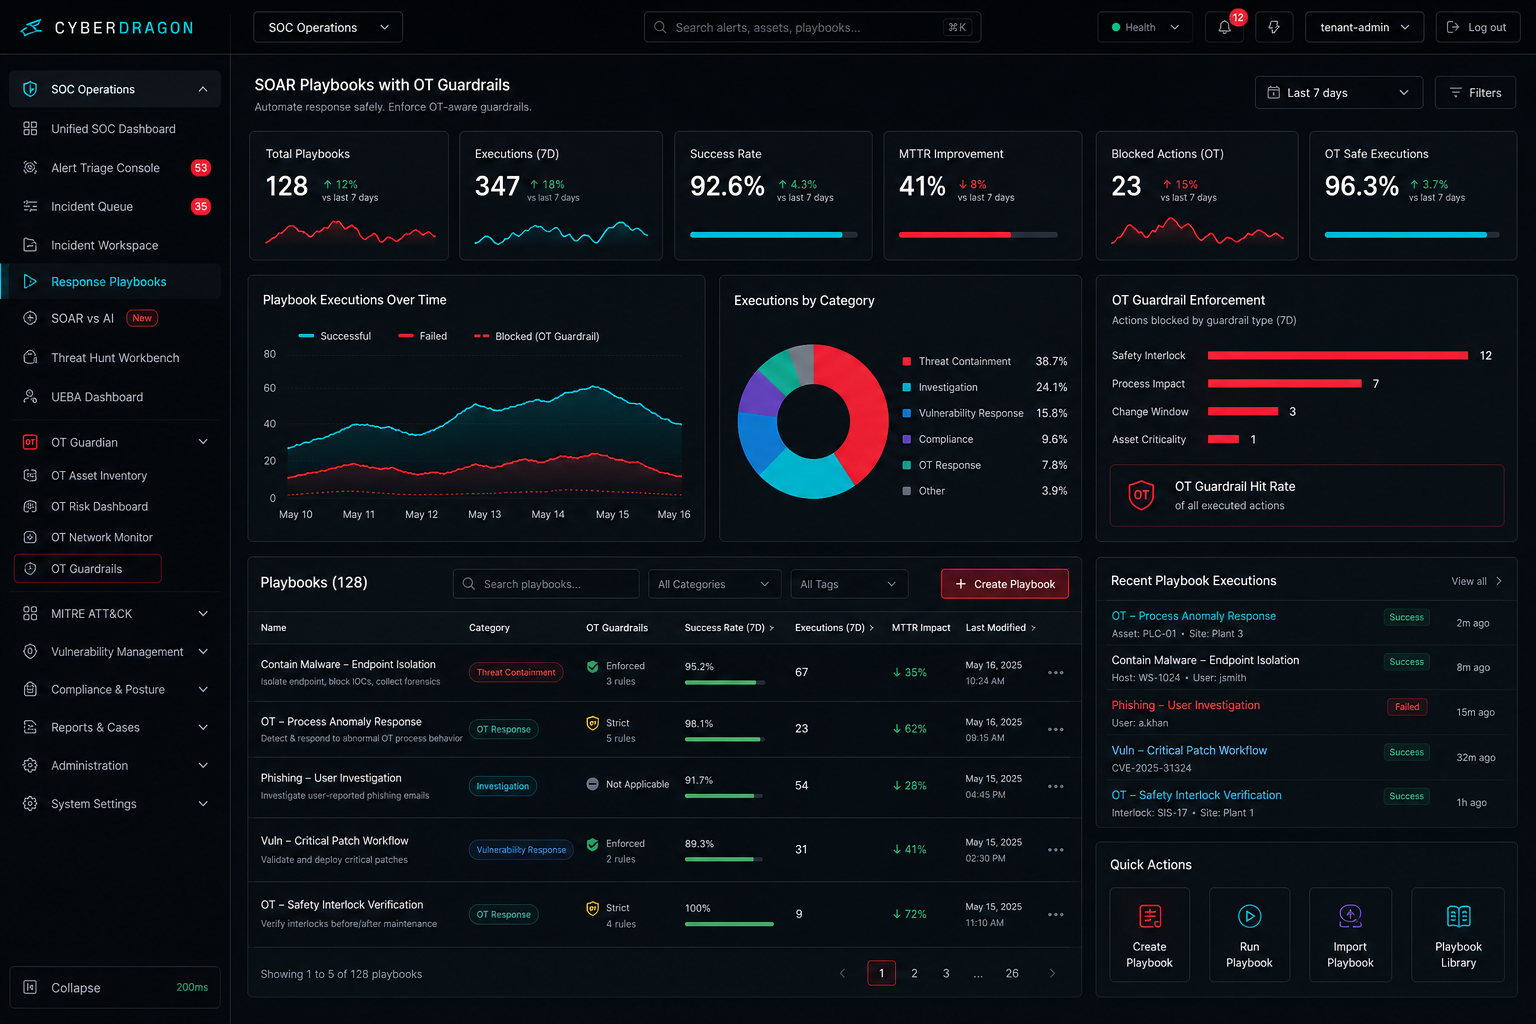
Response

SOAR playbooks with OT guardrails

  • Library → Run → Active workflows → Tier-3 OT queue.
  • OPA can still deny an OT-affecting action after a human approves.
  • Evidence written on every playbook decision.
CyberDragon Response playbooks
OT Safety Gate

SOAR that can still say no.

Playbooks require human approval on OT-affecting classes and and OPA evaluates the action independently, so it can deny even after an analyst approves it.

Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →

Correlation windows

W15 / W60 / W24 kill-chain windows

  • W15 burst correlation for scanning and brute force.
  • W60 lateral movement and engineering-workstation pivots.
  • W24 slow APT dwell and C2 staging.
Incident workspace
Evidence on every decision

Detections, approvals, and denials and all sealed.

01

Capture

Detection, response action, and approval decisions are written as immutable records.

02

Hash

Each record is hashed and chained to its predecessor and any edit breaks the chain.

03

Sign

Ed25519 signatures seal the chain using Vault-backed key material.

04

Verify

Chain verification runs on demand; lab run verified 66 entries OK.

05

Export

Auditor-ready ZIP packets with policy reason codes, including OT denials.

Data pipeline

Capture to seal in seven stages

  • Capture → buffer → transport → enrich → correlate → decide → seal.
  • Same pipeline feeding every SIEM/SOAR screen on this site.
  • Hash-chained, Ed25519-signed at the final stage.
Incident Queue
SOC Operations screens

Unified SOC, Alert Triage, Incident Queue, Workspace, Playbooks, Threat Hunt, UEBA

The Analyst Copilot console an analyst actually works in and Unified SOC through response playbooks and behind the same indigenous SIEM/SOAR plane described on this page.

FAQ

Frequently asked questions.

See a kill chain assemble in your own SIEM/SOAR tenant.

A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.