
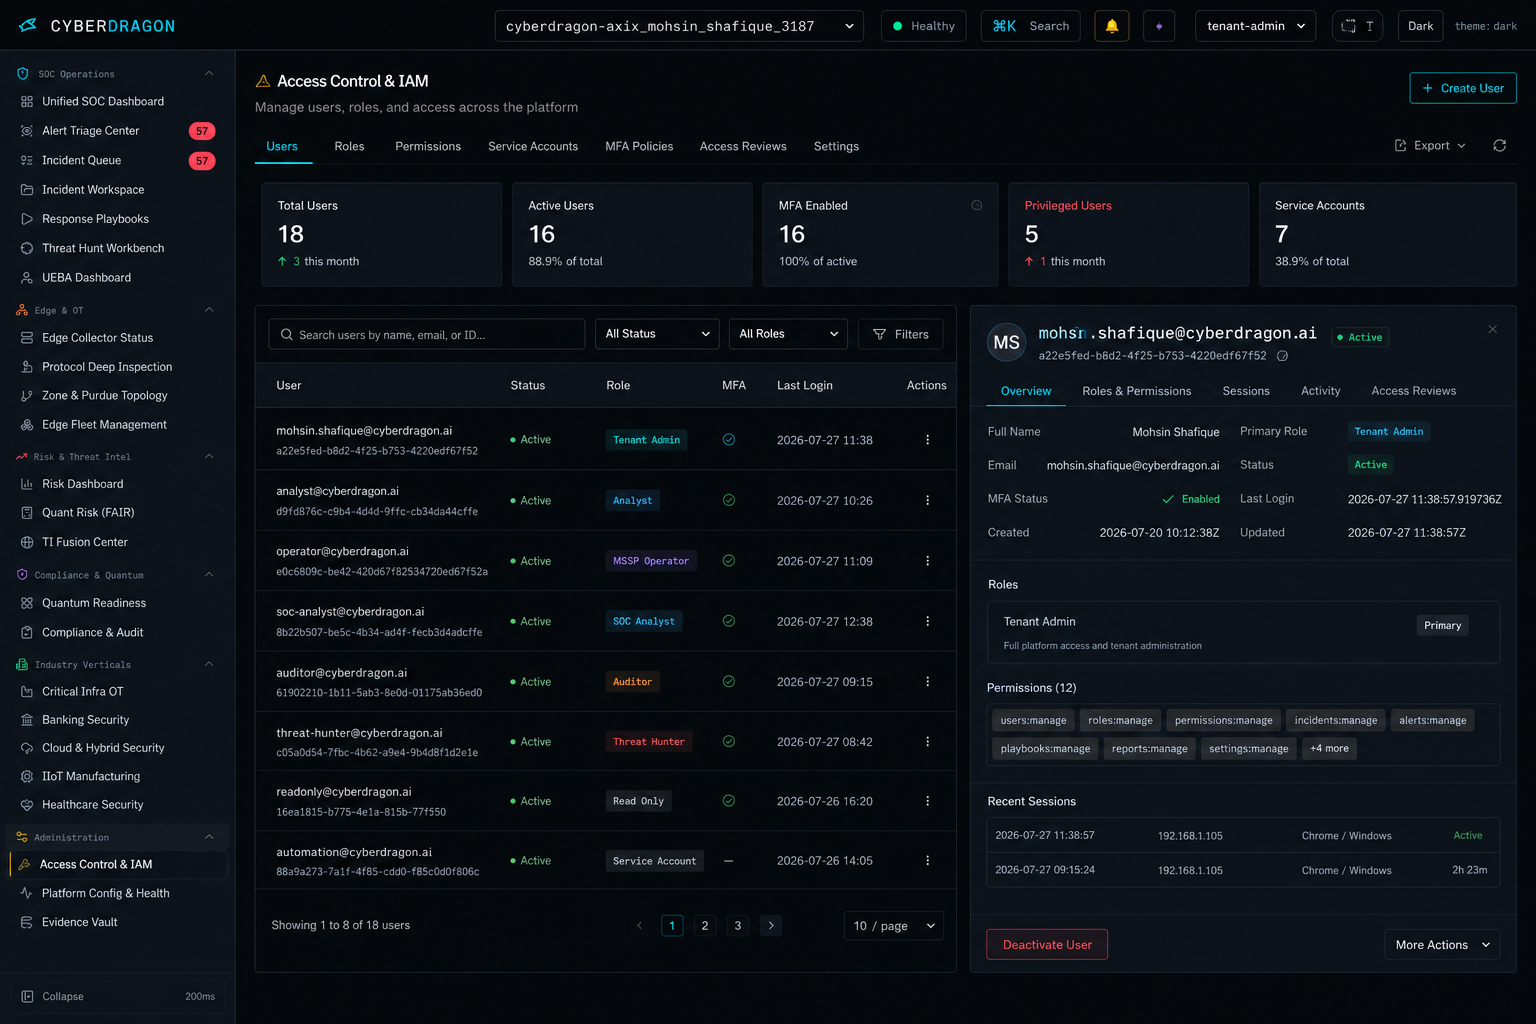
IAM
Who owns users and roles
- Tenant-admin owns IAM; Super Admin owns tenancy.
- Role matrix is enforced in UI and API.
- Leadership can take partnership intents from contact.
Axix Technologies LLC USA runs CyberDragon as one product organisation: detection engineering, OT delivery, applied cryptography, and threat research report into the same roadmap.
Founder & Chief Executive Officer
Sets the CyberDragon thesis: one platform that treats enterprise, OT, IoT, and IIoT as a single kill chain instead of four disconnected tool stacks. Owns the roadmap from Edge collection through evidence-grade auditor output.
Product strategy, OT security architecture, customer outcomes
IAM
Platform & Detection Engineering
Runs the Core control plane — ingest, threat-intel fusion, cascading W15/W60/W24 correlation, and the Neo4j attack-path graph — plus the signed YAML detection packs that ship to every tenant.
Kafka control plane, Temporal orchestration, detection content
Security, Trust & Compliance
Owns the security program behind the platform: hybrid post-quantum identity, OPA authorization, PostgreSQL row-level tenant isolation, break-glass procedure, and the tamper-evident evidence chain auditors rely on.
IEC 62443, NERC CIP, SOC 2, ISO 27001, evidence integrity
Edge & Industrial Delivery
Installs Edge at the industrial DMZ, validates SPAN/TAP capture, tunes Modbus, DNP3, OPC-UA, and MQTT parsing per site, and keeps the safety rule absolute — no command plane into Purdue L0–L2.
Purdue-aligned deployment, protocol parsers, plant-side rollout
Proof of Value, MSSP & Support
Runs the path from 7-day free trial to 30-day Proof of Value to production go-live, and enables MSSP partners on cross-tenant operations, white-label options, and client onboarding.
PoV delivery, MSSP enablement, hypercare and SLAs
Intelligence & Adversary Emulation
Maintains the live Threat Atlas feeds, the 15,093-IOC corpus, and the six lab-validated attack scenarios that measure detection quality — including the 14.3-second APT kill-chain benchmark.
Threat Atlas, IOC corpus, purple-team scenarios
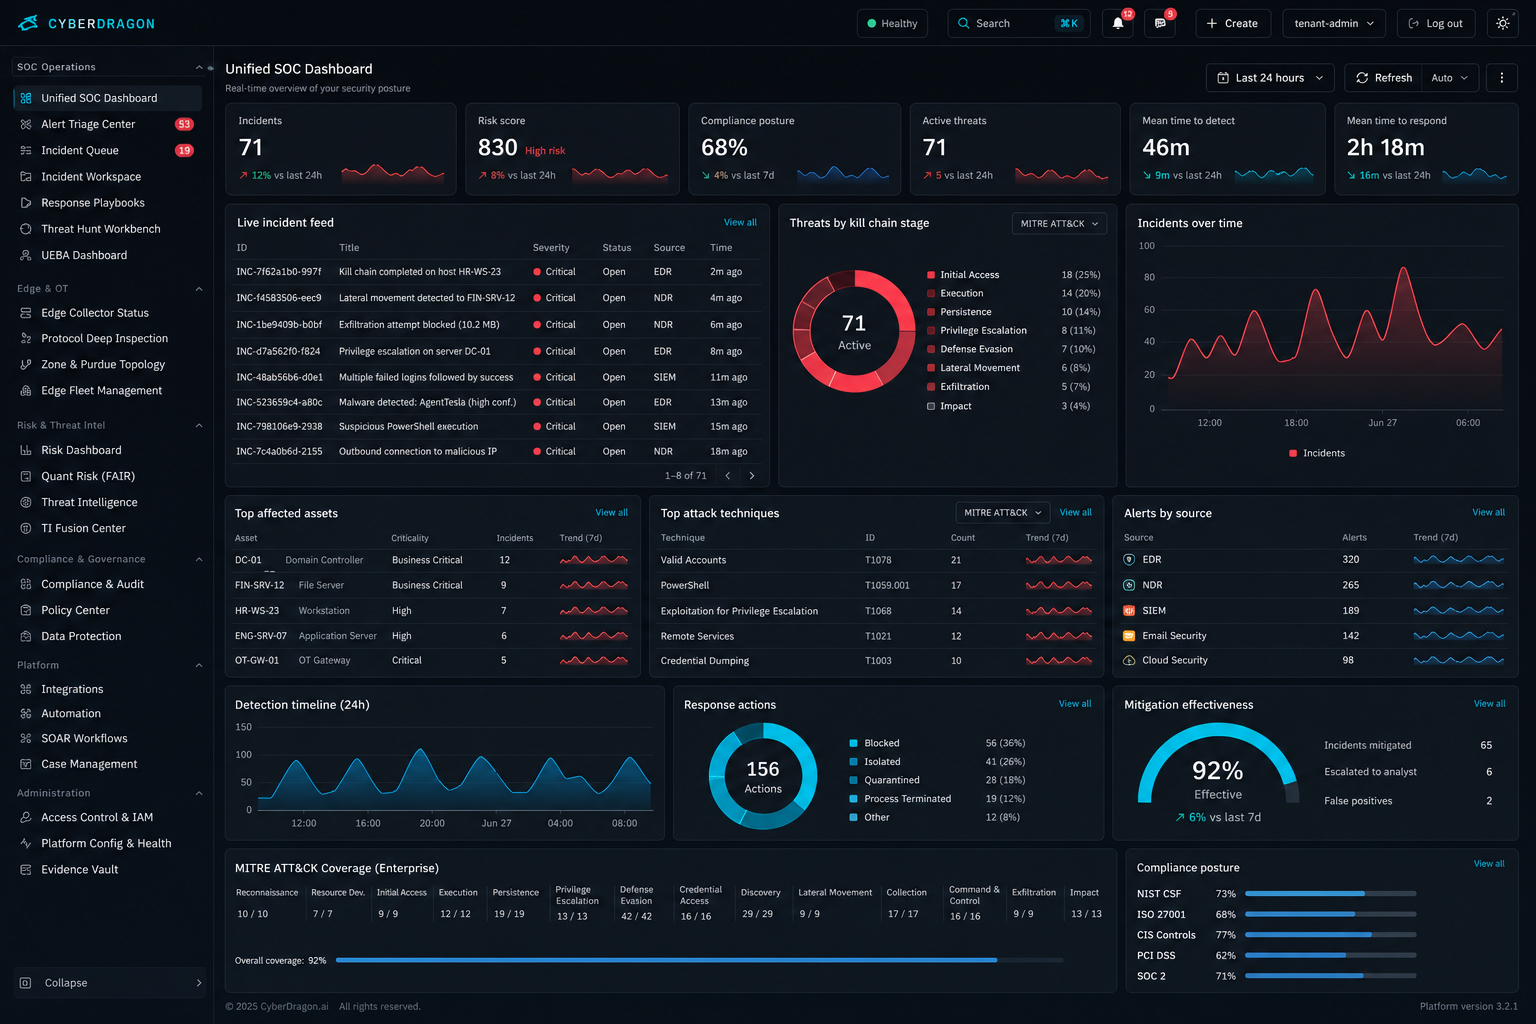
SOC
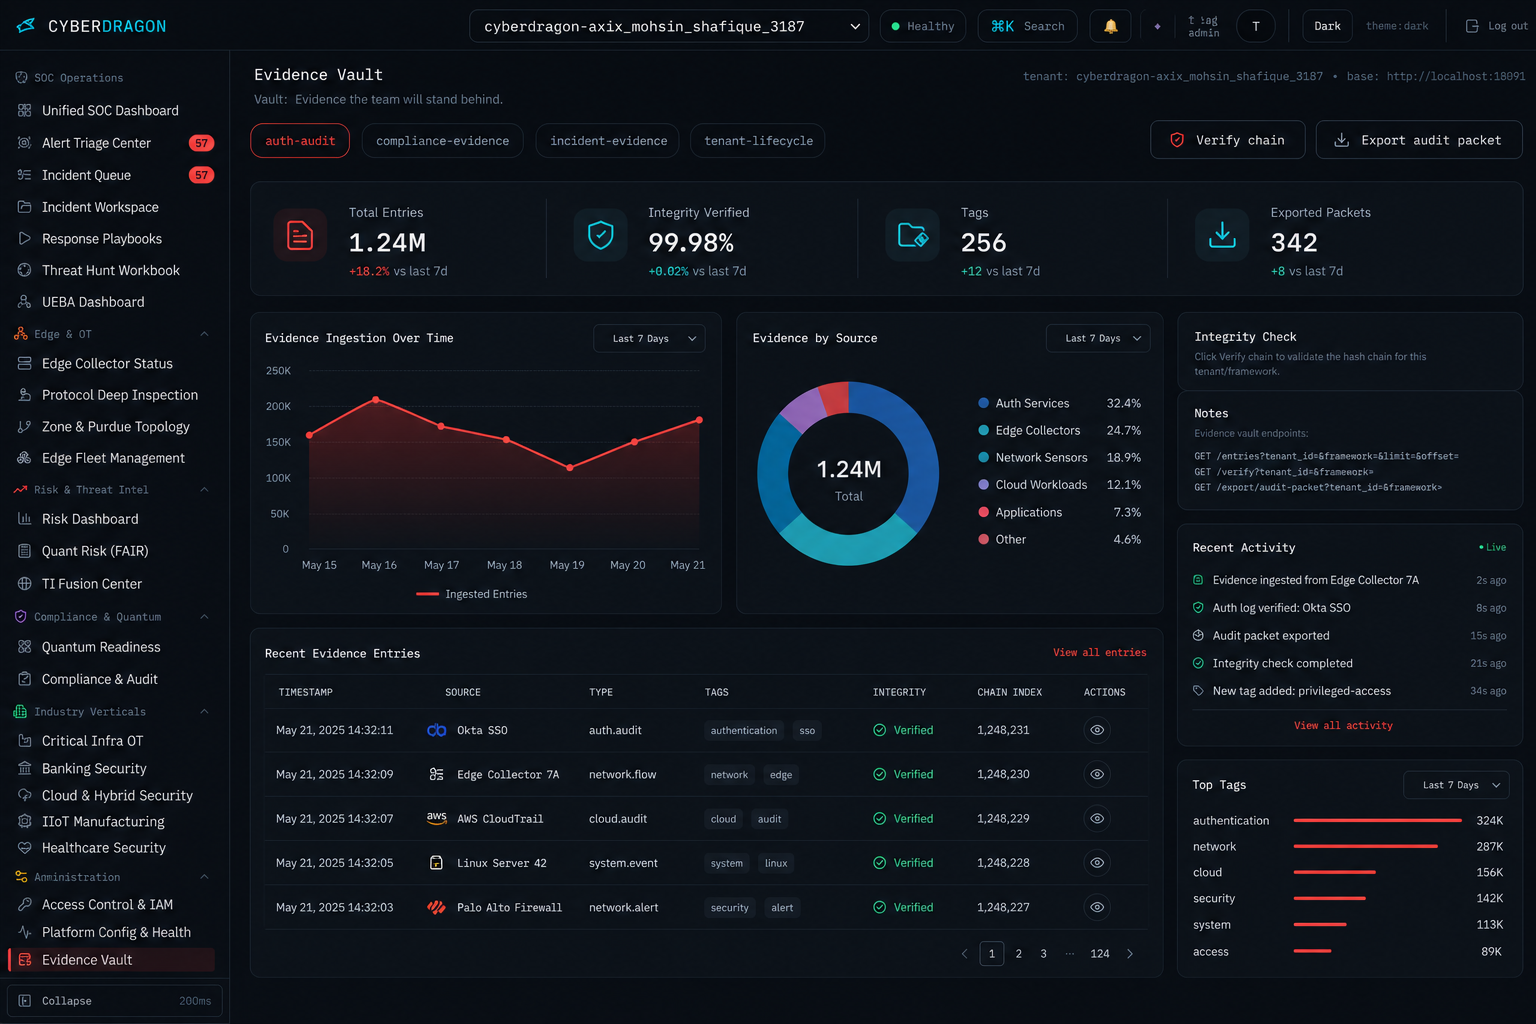
Vault
Kafka-backed Core, PostgreSQL RLS multi-tenancy, and the first Modbus/DNP3 Edge collector.
Hybrid ML-DSA-65 + Ed25519 session JWTs with Vault-backed signing material went live.
Cascading W15 / W60 / W24 windows plus explicit Enterprise→OT pivot signalling.
Hash-chained, signed audit trail with auditor ZIP export and verified 66-entry lab chain.
22.4-hour baseline: 41,959 events, 6/6 attack scenarios detected, 0 false incidents, 8.0–20.5s MTTD.
Public IoT/ICS threat, malware, and ICS advisory board built on live CISA and ransomware disclosure feeds.
| Role | What they care about | What CyberDragon gives them |
|---|---|---|
| CISO | Board-level risk narrative, quantified exposure, and audit readiness | Executive reporting, FAIR scenario scoring, and signed evidence packets. |
| SOC Manager | Alert quality, MTTD, and analyst throughput | Kill-chain correlation instead of raw alerts, plus playbooks with approval gates. |
| OT / Plant Engineer | Nothing may disturb the process | Passive SPAN capture, no agents on PLCs, no command plane into L0–L2. |
| Compliance Lead | Control coverage and evidence on demand | Auto-mapped IEC 62443, NERC CIP, NIST CSF, ISO 27001, and SOC 2 controls. |
| MSSP Operator | Margin, isolation, and onboarding speed | PostgreSQL RLS tenancy, cross-tenant portfolio views, and white-label options. |
| Auditor | Can this record be trusted? | Tamper-evident hash chain with Ed25519 signatures and reproducible verification. |
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.