
SOC
See the product, then the docs
- Unified SOC is the briefing the docs describe.
- Academy and case studies use the same console language.
- Start a trial on your traffic — not a slide deck.
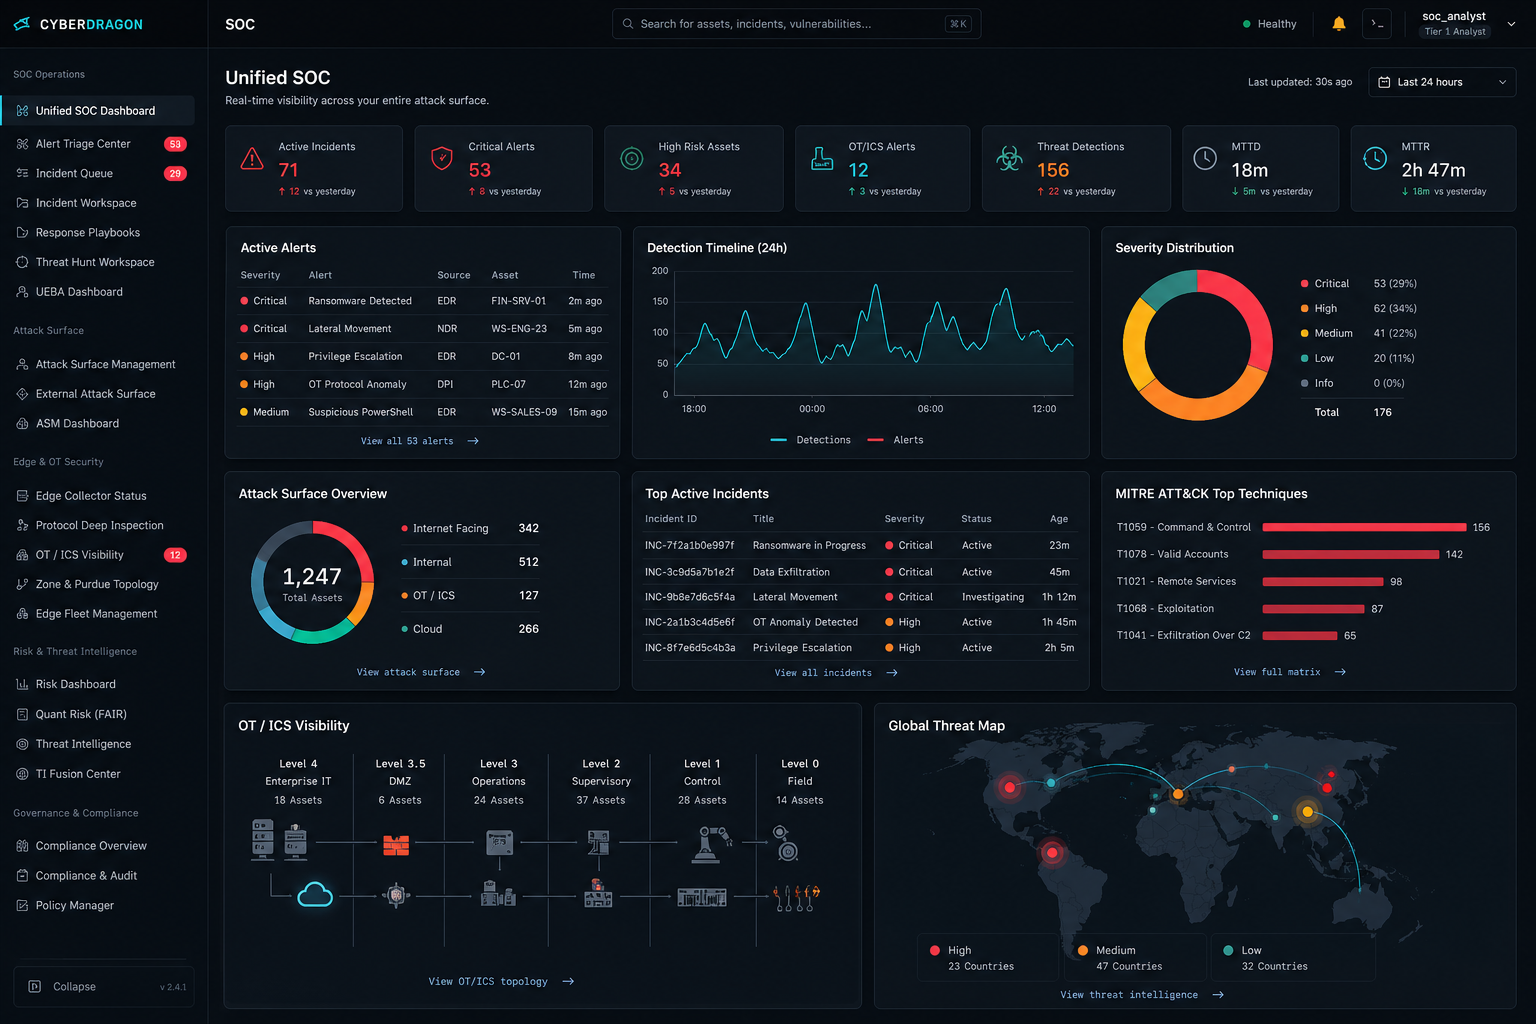
Everything buyers, operators, and partners need after the homepage.
SOC
| Role | What you are trying to answer | Where to go first |
|---|---|---|
| CISO | Board-level risk narrative, quantified exposure, and audit readiness | Executive reporting, FAIR scenario scoring, and signed evidence packets. |
| SOC Manager | Alert quality, MTTD, and analyst throughput | Kill-chain correlation instead of raw alerts, plus playbooks with approval gates. |
| OT / Plant Engineer | Nothing may disturb the process | Passive SPAN capture, no agents on PLCs, no command plane into L0–L2. |
| Compliance Lead | Control coverage and evidence on demand | Auto-mapped IEC 62443, NERC CIP, NIST CSF, ISO 27001, and SOC 2 controls. |
| MSSP Operator | Margin, isolation, and onboarding speed | PostgreSQL RLS tenancy, cross-tenant portfolio views, and white-label options. |
| Auditor | Can this record be trusted? | Tamper-evident hash chain with Ed25519 signatures and reproducible verification. |
Quantum
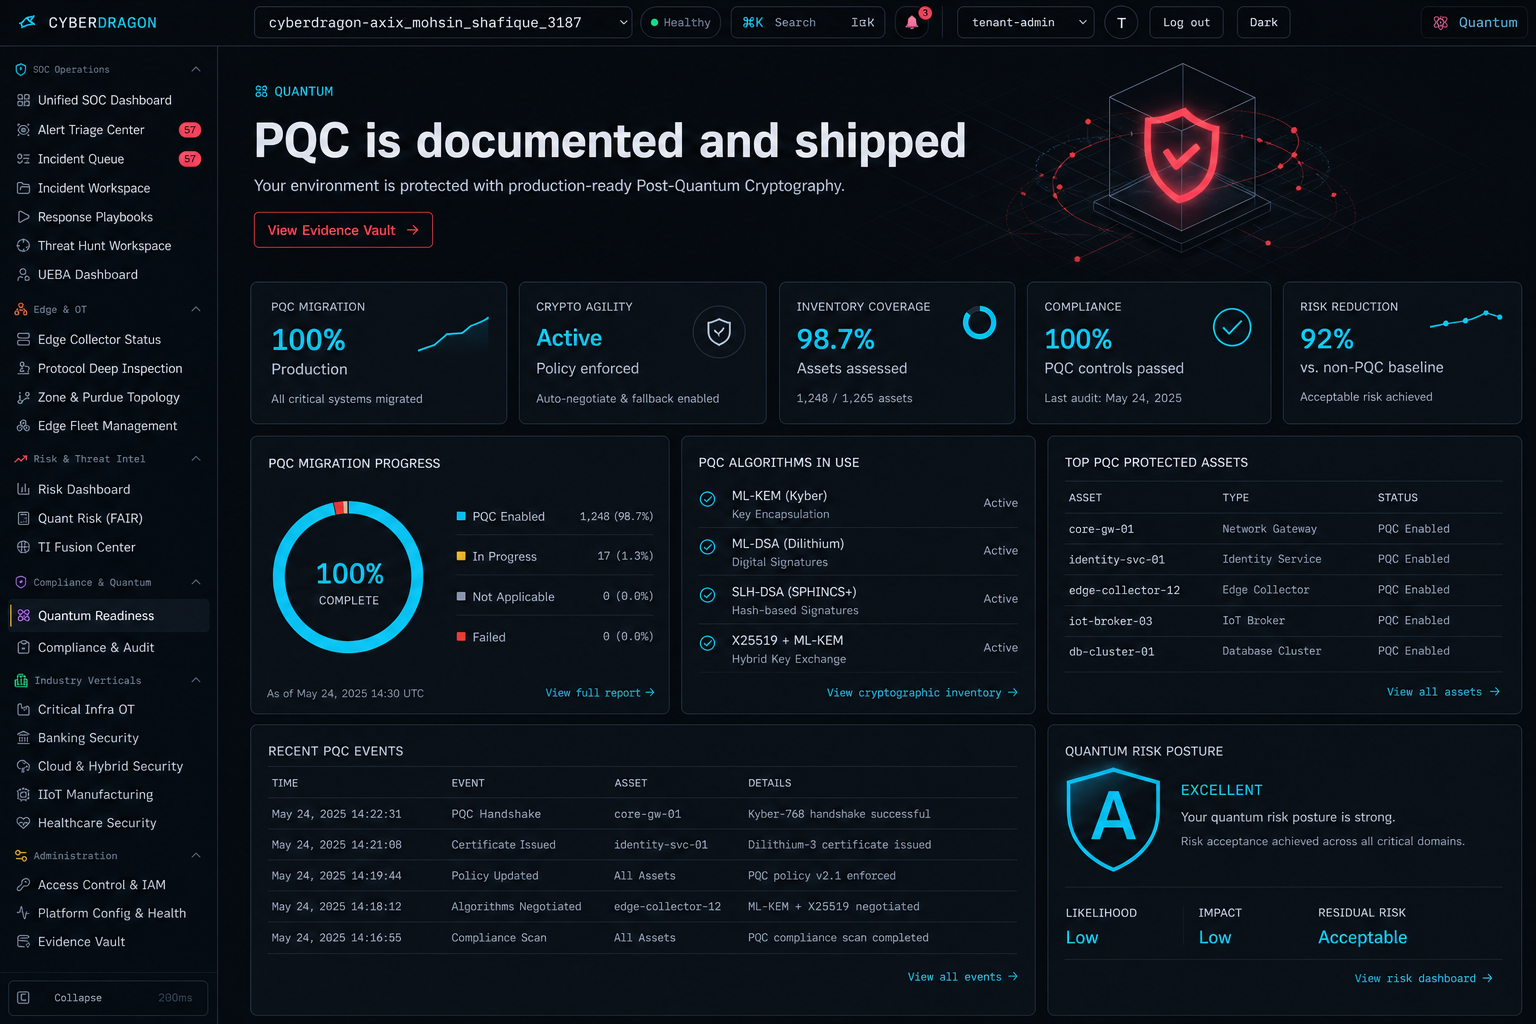
Seven days, no credit card. A tenant is created immediately with sample Enterprise/OT telemetry loaded.
Point syslog at the tenant or deploy an Edge collector in software mode on a mirrored port.
Run a scenario and watch W15 / W60 / W24 correlation assemble it into one incident timeline.
Verify the hash chain and export an auditor packet before the trial window closes.
Vault
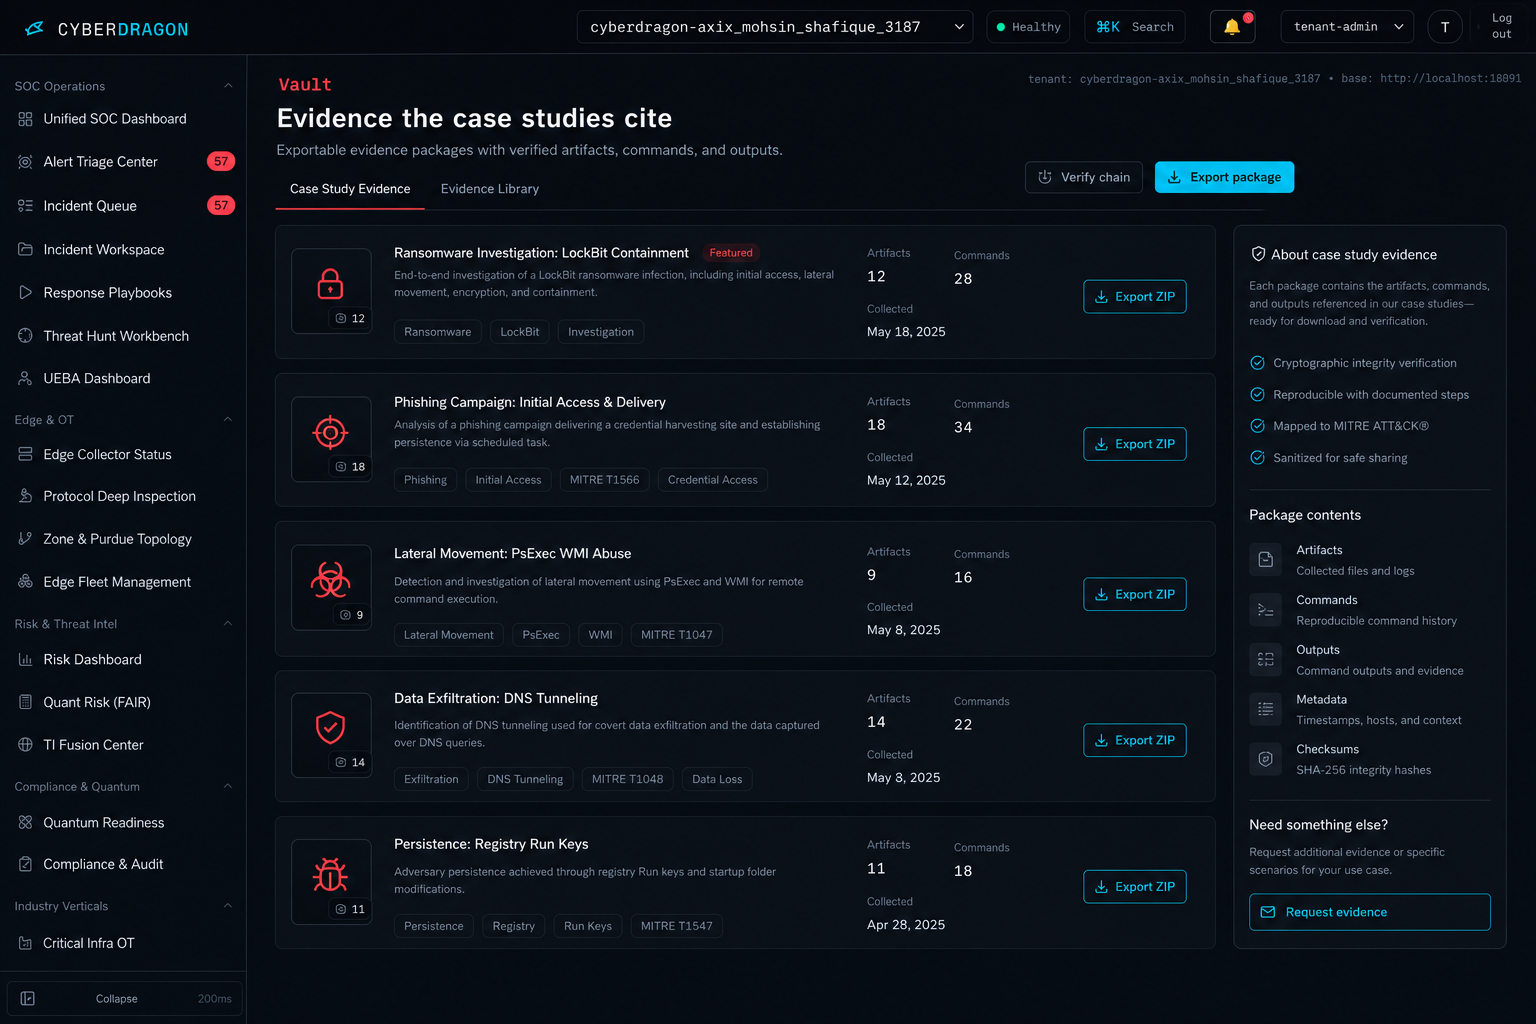
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.