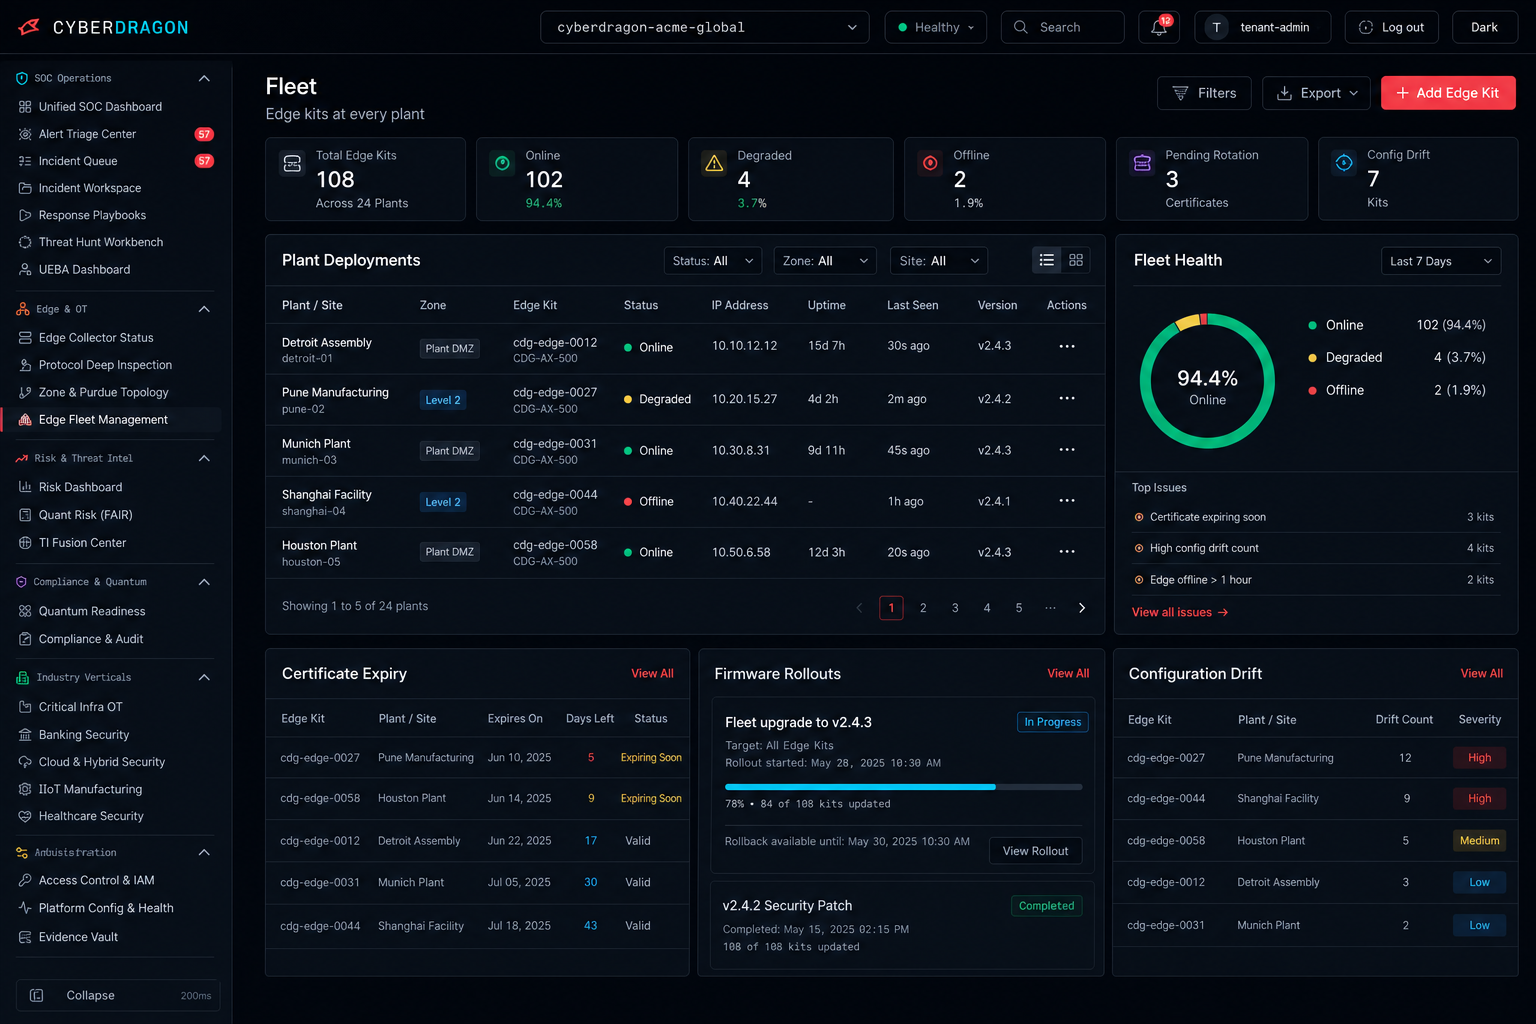
Fleet
Edge kits at every plant
- Mode A: Core in cloud, Edge on-site.
- Mode B: Core + Edge sovereign / air-gap.
- Certs and firmware tracked per node.
Edge stays at the plant DMZ. Core can live in cloud, sovereign region, or fully on-prem and including air-gap.
Core hosted in cloud; Edge on-site.
Best for: Mid-market, fast PoV
Core + Edge at customer site.
Best for: Air-gap, data sovereignty
Isolated VPC and database per customer.
Best for: Banks, national utilities
Edge stays local; Core runs in a sovereign cloud region.
Best for: National utilities
MSSP hosts the platform under an Axix license.
Best for: Service providers
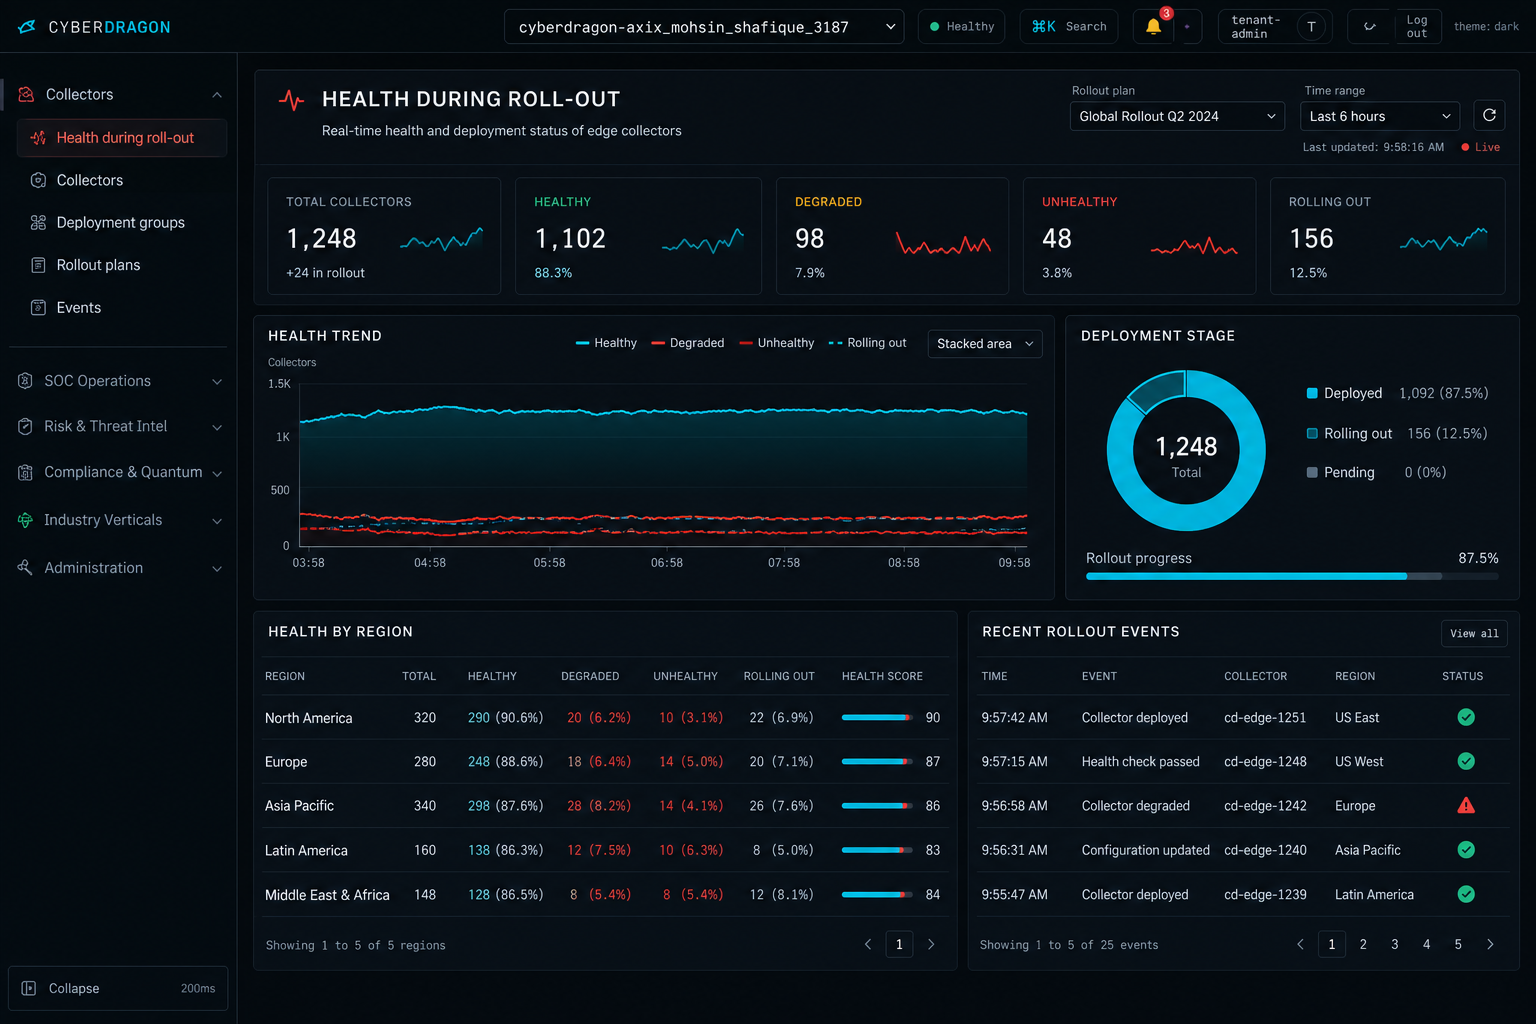
Fleet
Collectors
| Tier | Uptime | P1 response | Support |
|---|---|---|---|
| Standard | 99.5% | 4 hours | Business hours |
| Enterprise | 99.9% | 1 hour | 24×5 |
| Critical Infrastructure | 99.95% | 30 min | 24×7 |
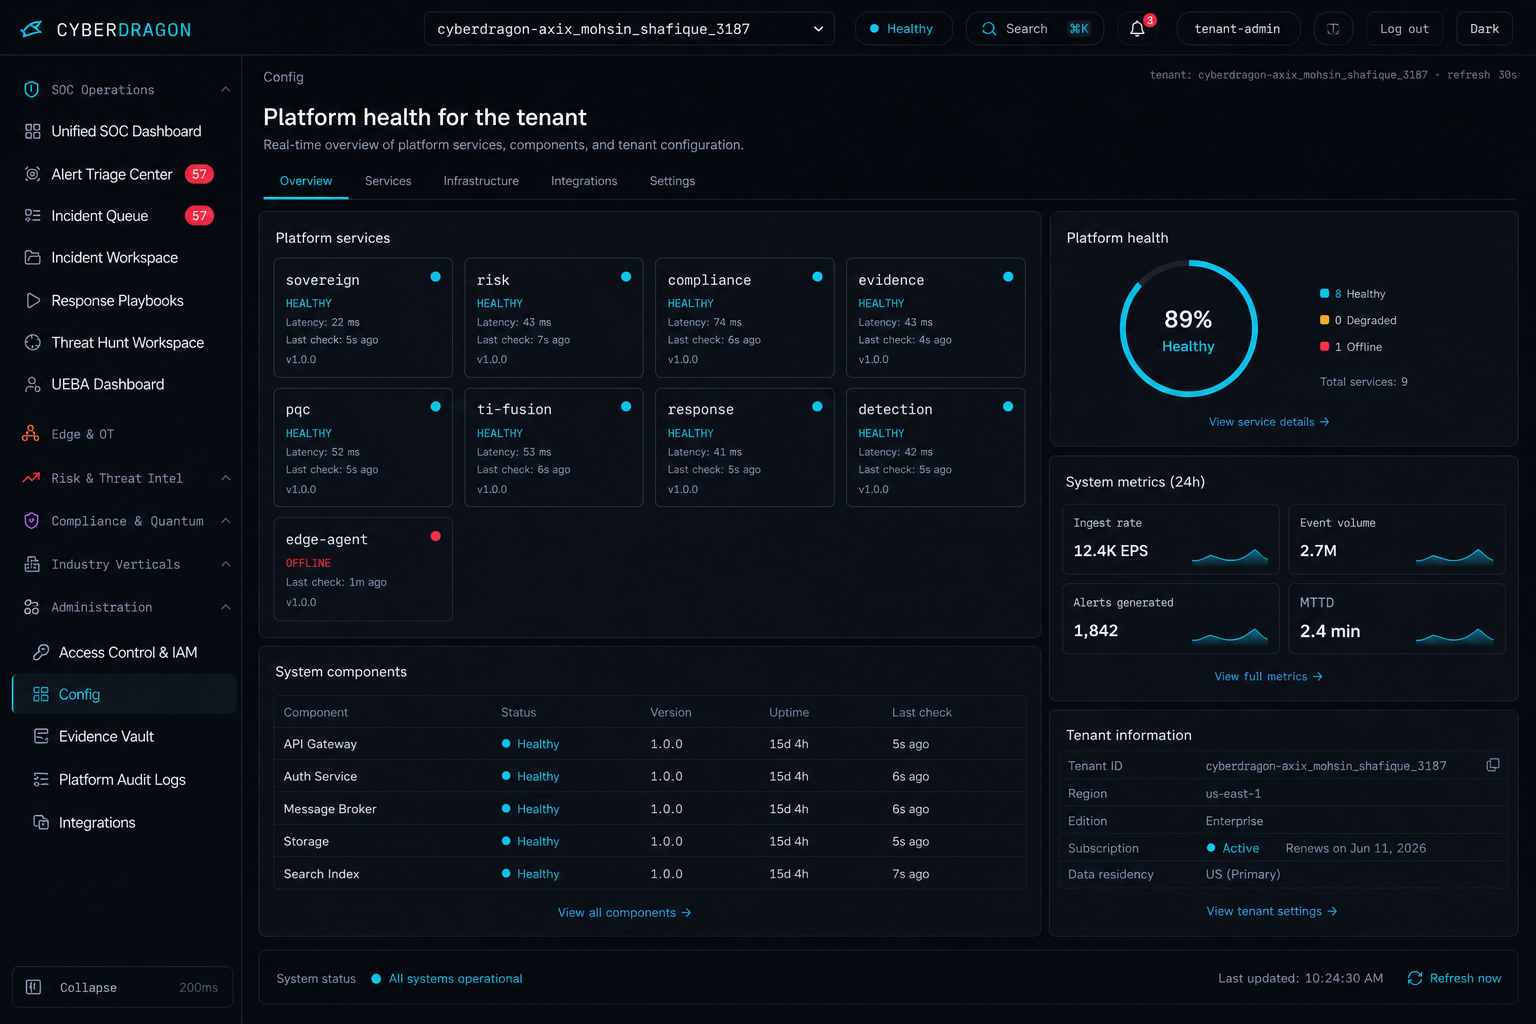
Config
Edge mirrors traffic from a SPAN port or hardware TAP at the industrial DMZ and parses OT protocols locally.
Events land in a SQLite WAL store-and-forward queue (~5,000 events) so a link outage never loses telemetry.
HMAC-SHA256 signed batches, optionally mTLS, are shipped to Core over the ingest network only.
Threat-intel fusion adds OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise context in flight.
Cascading W15 / W60 / W24 windows assemble events into kill chains and flag Enterprise→OT pivots explicitly.
Risk scoring, compliance auto-mapping, and Temporal playbooks with human approval and OPA guardrails.
Detections, approvals, and denials are hash-chained and Ed25519-signed into the evidence vault.
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.