
PQC
Already live — still hardening inventory views
- Hybrid identity is not a future epic.
- Readiness UI will keep gaining crypto-inventory depth.
- We label partial vs live on the platform page.
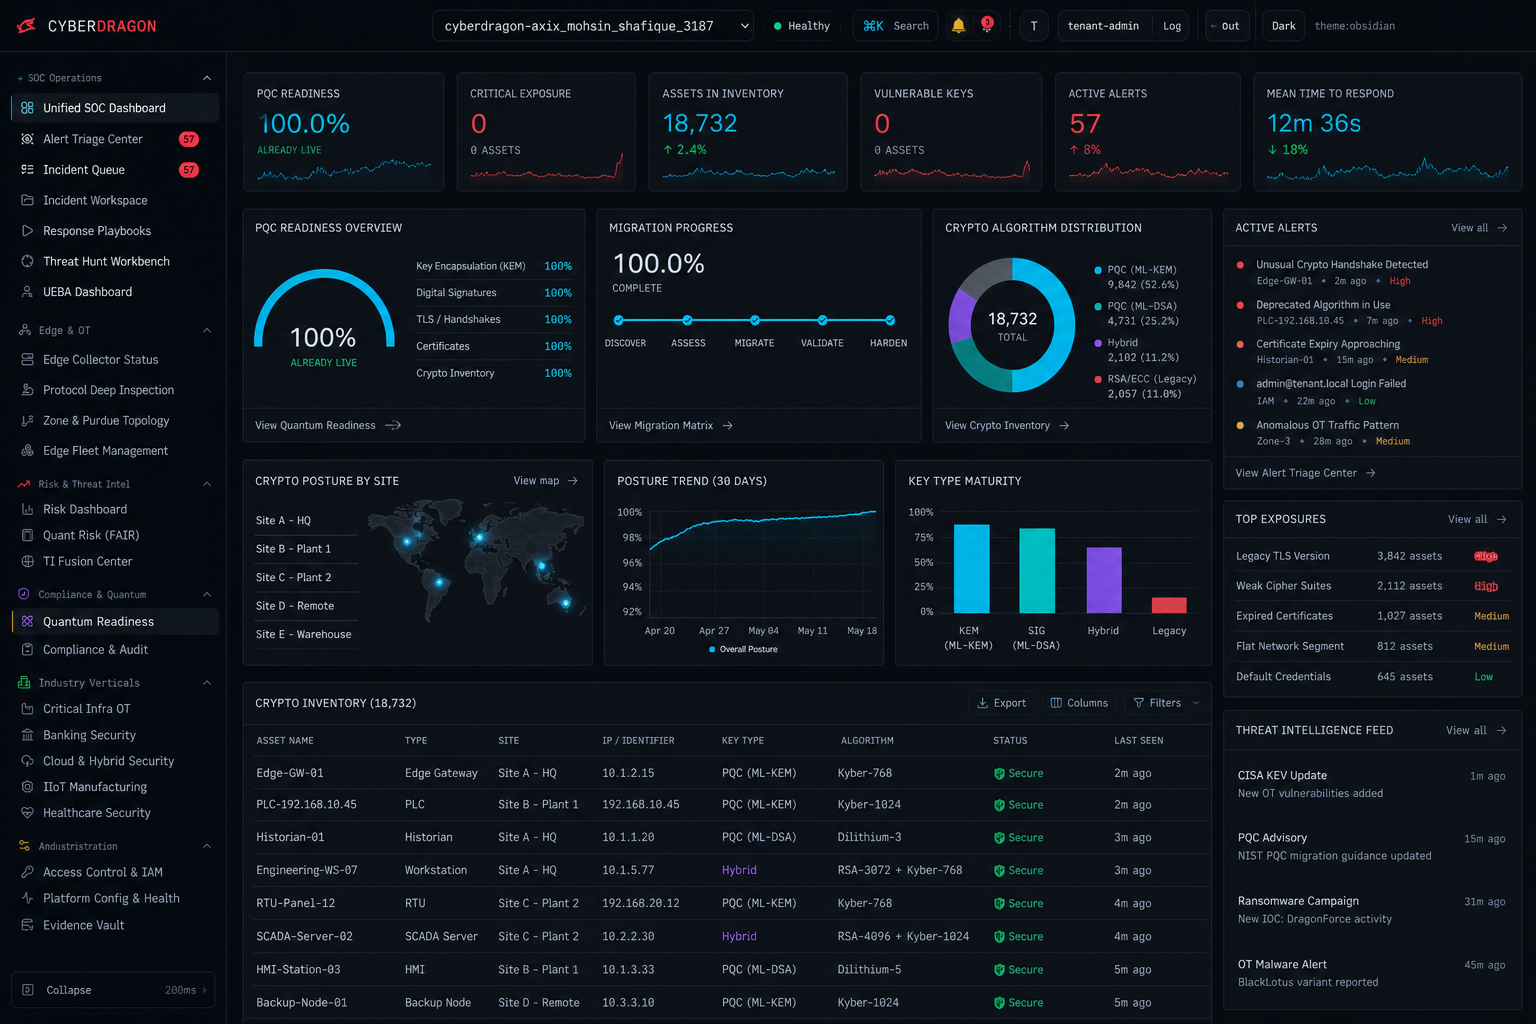
CyberDragon Core is available for Proof of Value and pilot deployments. Anything not shipping yet is marked so buyers can plan around it.
Guided hypothesis hunting over the unified Enterprise/OT event store.
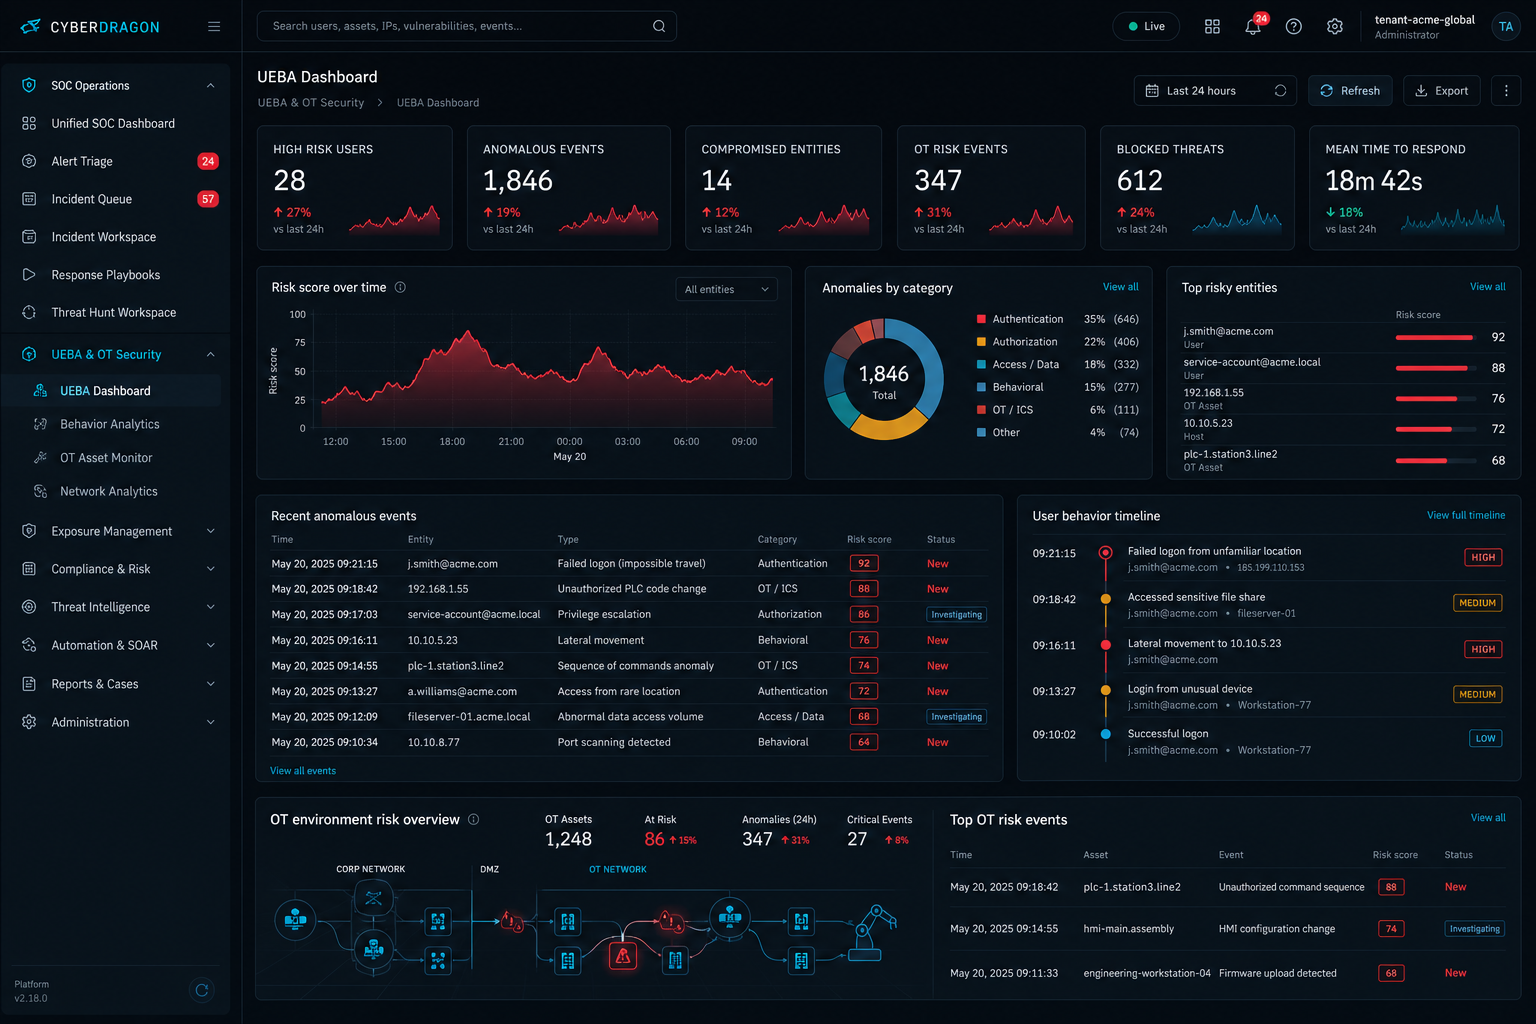
Behavior analytics for operator and service accounts.
Analyst-facing assistant grounded in tenant evidence.
Cyber Resilience Act control bridge on top of existing framework packs.
Until then, use the local Edge operations dashboard.
Live and shipping; visual and workflow hardening in progress.
Neo4j graph is live; incident-detail depth expanding.
Cross-tenant operations available to partner program members.
Post-quantum key encapsulation (NIST FIPS 203) alongside the existing ML-DSA-65 + Ed25519 hybrid signing.
Board PDFs and CISO digests ship; template and scheduling depth still expanding.
Detection pack and partner integration catalog live; catalog breadth still growing.
FAIR-style scoring is live; the pre-built scenario library is still expanding past the initial set.
PQC
| Feature | Status | Where you see it |
|---|---|---|
| Incident Queue | live | Show prominently |
| Login / JWT / MFA | live | Show prominently |
| Evidence verify/export | live | Show prominently |
| Tenant create/suspend | live | Admin section only |
| Unified SOC Dashboard | partial | Enhanced / hardening |
| Incident Detail / Attack Graph | partial | Real screenshots when available |
| Risk / Compliance Dashboards | partial | Framework cards |
| Threat Hunt / UEBA | roadmap | Coming soon |
| AI Copilot Chat | roadmap | Coming soon |
| MSSP Portal | partial | Partner page |
| Edge Analyst UI routes | roadmap | Use local Edge Dashboard |
SOAR
ML-DSA-65 + Ed25519 hybrid JWTs; MFA; API keys; Vault-backed signing keys.
Cascading W15 (15 min) / W60 (1 hr) / W24 (24 hr) correlation windows.
Explicit signaling when enterprise compromise precedes OT-side anomalies.
OTX, Abuse.ch, ThreatFox, MITRE TAXII, GreyNoise — in-flight enrichment.
Mirrored NVD/CVE/CPE, CISA ICS-KEV, and OSV for local, offline-safe query.
Asset risk plus FAIR-style scenario scoring, 0–100.
Events mapped to controls automatically — roughly 7 controls per network event.
IEC 62443-3-3, NERC CIP, NIST CSF 2.0, ISO 27001:2022, SOC 2.
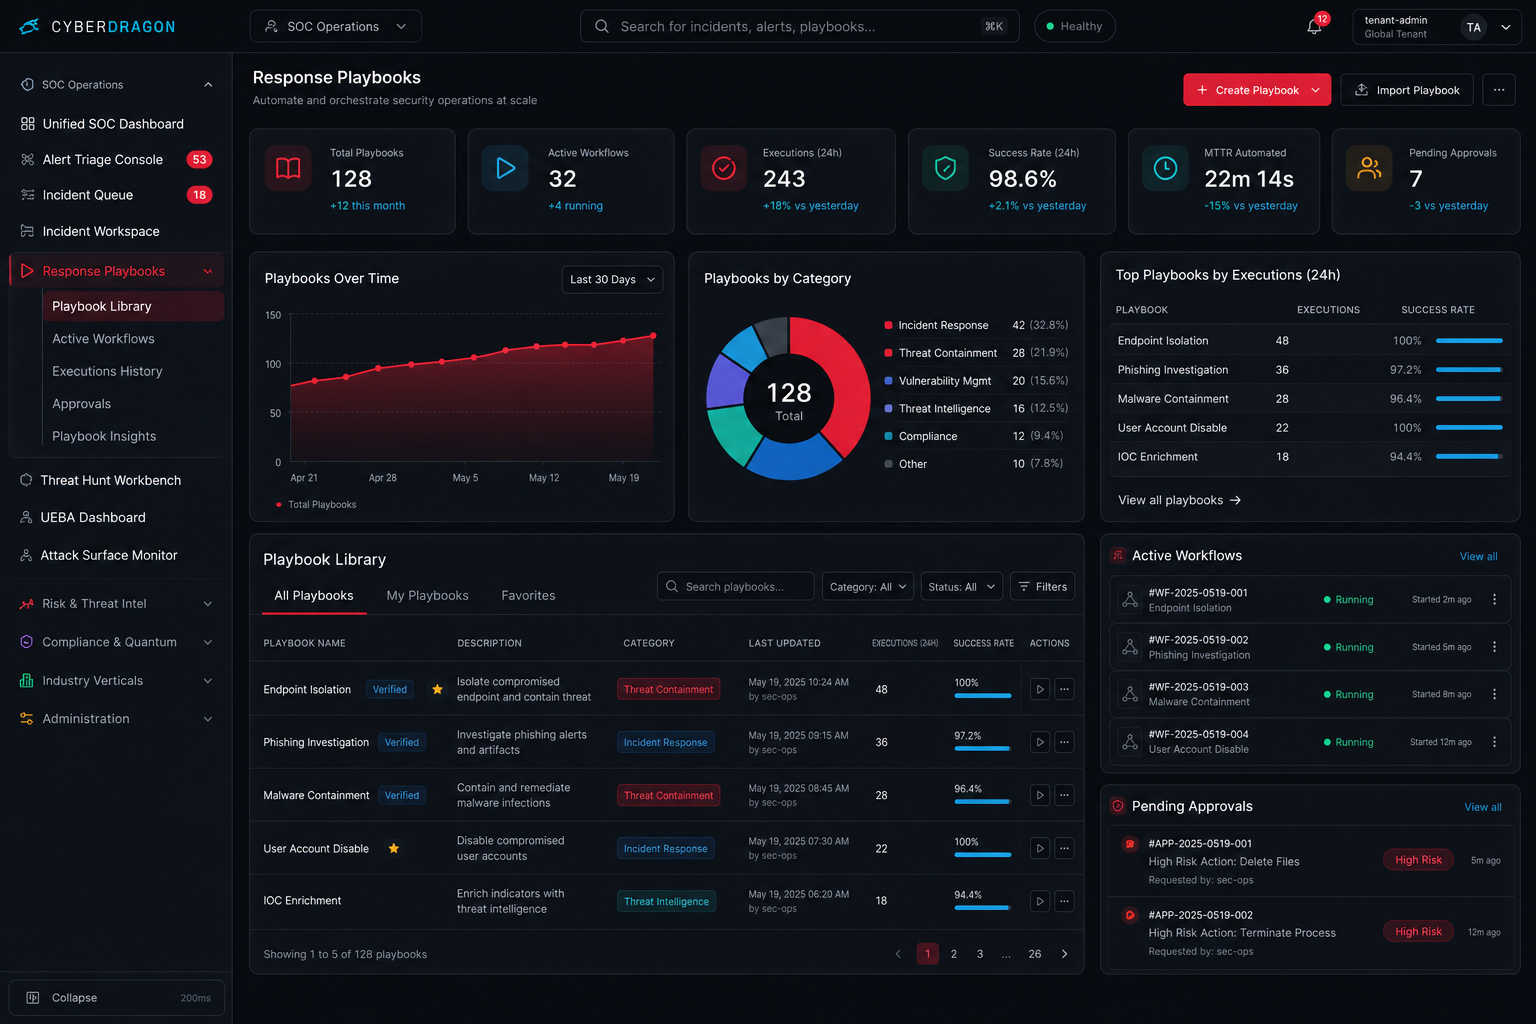
Temporal-orchestrated playbooks with human approval workflows.
OPA policy can deny actions even after human approval on OT-affecting classes.
Hash-chained, Ed25519-signed, tamper-evident audit trail with ZIP export.
Neo4j-backed cyber-physical knowledge graph.
Board PDFs, CISO monthly digests, auditor packets.
Detection packs and partner integration catalog.
Cross-tenant operations, client onboarding, portfolio views.
UEBA
Kafka-backed Core, PostgreSQL RLS multi-tenancy, and the first Modbus/DNP3 Edge collector.
Hybrid ML-DSA-65 + Ed25519 session JWTs with Vault-backed signing material went live.
Cascading W15 / W60 / W24 windows plus explicit Enterprise→OT pivot signalling.
Hash-chained, signed audit trail with auditor ZIP export and verified 66-entry lab chain.
22.4-hour baseline: 41,959 events, 6/6 attack scenarios detected, 0 false incidents, 8.0–20.5s MTTD.
Public IoT/ICS threat, malware, and ICS advisory board built on live CISA and ransomware disclosure feeds.
Industry outlook — not a CyberDragon delivery date. Public roadmaps from NIST, NSA CNSA 2.0, and ENISA are the basis; CyberDragon's own hybrid ML-DSA-65 + Ed25519 signing is live today, not part of this forward-looking timeline.
Hybrid classical + post-quantum signing (ML-DSA-65 + Ed25519) is live in CyberDragon on every session JWT — crypto agility in production, not a slide.
NIST FIPS 203/204/205 (ML-KEM, ML-DSA, SLH-DSA) move from published standard to mandatory in US federal and adjacent regulated procurement; crypto-agility inventories become a standard audit line item.
"Harvest now, decrypt later" risk peaks for data with long confidentiality windows — utilities, healthcare, and defense-adjacent estates — as public quantum-hardware roadmaps mature; migration shifts from optional to contractual.
Post-quantum key exchange (ML-KEM) is expected at most TLS termination points for regulated industrial and financial estates; classical-only stacks risk procurement exclusion in several jurisdictions.
A cryptographically relevant quantum computer is treated as a live planning scenario in national critical-infrastructure programs (per public NIST, NSA CNSA 2.0, and ENISA roadmaps); crypto-agility — not a single algorithm choice — is the deciding factor for survivors.
Legacy classical-only systems still in the field become the dominant quantum-risk surface; retrofit cost on old estates, not new deployments, drives most of the remaining migration spend.
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.