
SOC
Where every Core module lands
- Live, partial, and roadmap labeled honestly on the platform page.
- Detection, risk, compliance, and identity share the same incident.
- Click a module, then come back to the operator board.
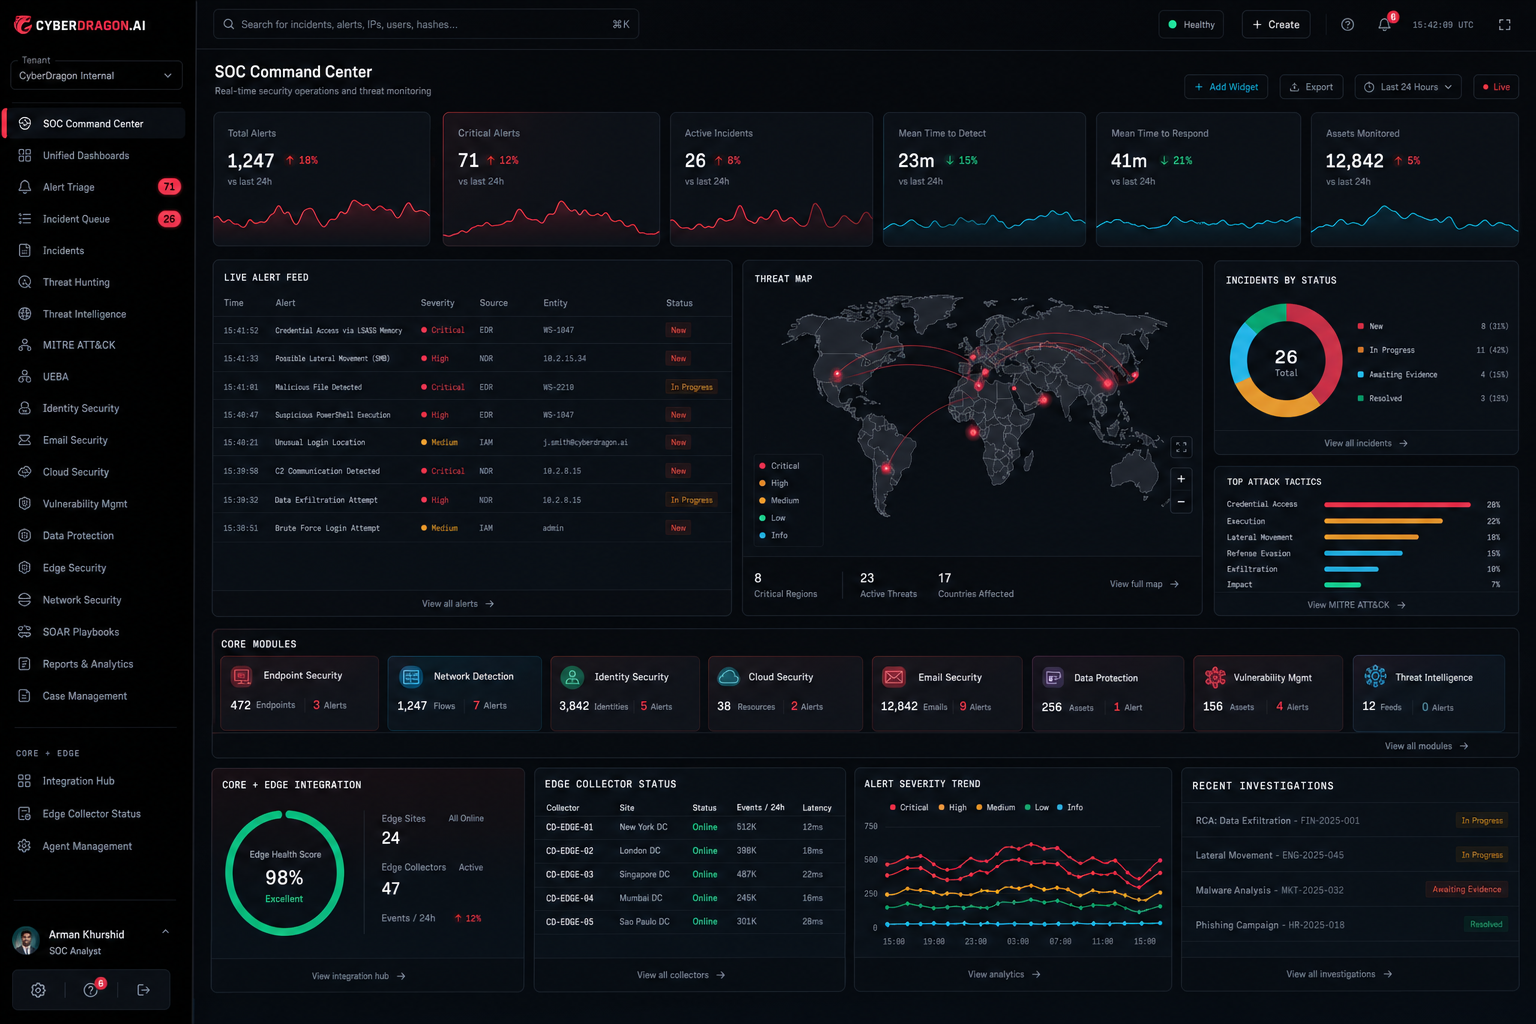
CyberDragon fuses open and commercial intel sources as events flow through the Kafka pipeline. IOCs match Edge protocol events, enterprise syslog, and cloud telemetry in the same indigenous SIEM plane — plus live Threat Atlas context for plant-floor operators.
OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise join the kill-chain timeline — this briefing is the public face of that fusion.
Multi-source in-flight enrichment on every normalized event
15,093+ IOC corpus matched against Edge and connector telemetry
STIX / TAXII2 exchange with your existing intel platform
Threat Atlas live board for IoT/ICS advisories and ransomware context
GreyNoise noise reduction for internet-facing assets
MITRE ATT&CK and ICS mapping on enriched incidents
SOC
Edge, syslog, Splunk HEC, and cloud connectors land in Kafka ingest topics.
Events are schema-normalized so OT protocol semantics and IT logs share one object model.
OTX, Abuse.ch, ThreatFox, TAXII feeds, and GreyNoise add context before detection rules run.
Kill-chain windows assemble enriched signals into one incident timeline.
Threat Atlas overlays IoT/ICS advisories and KEV entries for operator-readable risk.
Playbooks inherit intel verdicts; evidence vault seals enrichment provenance.
Playbooks
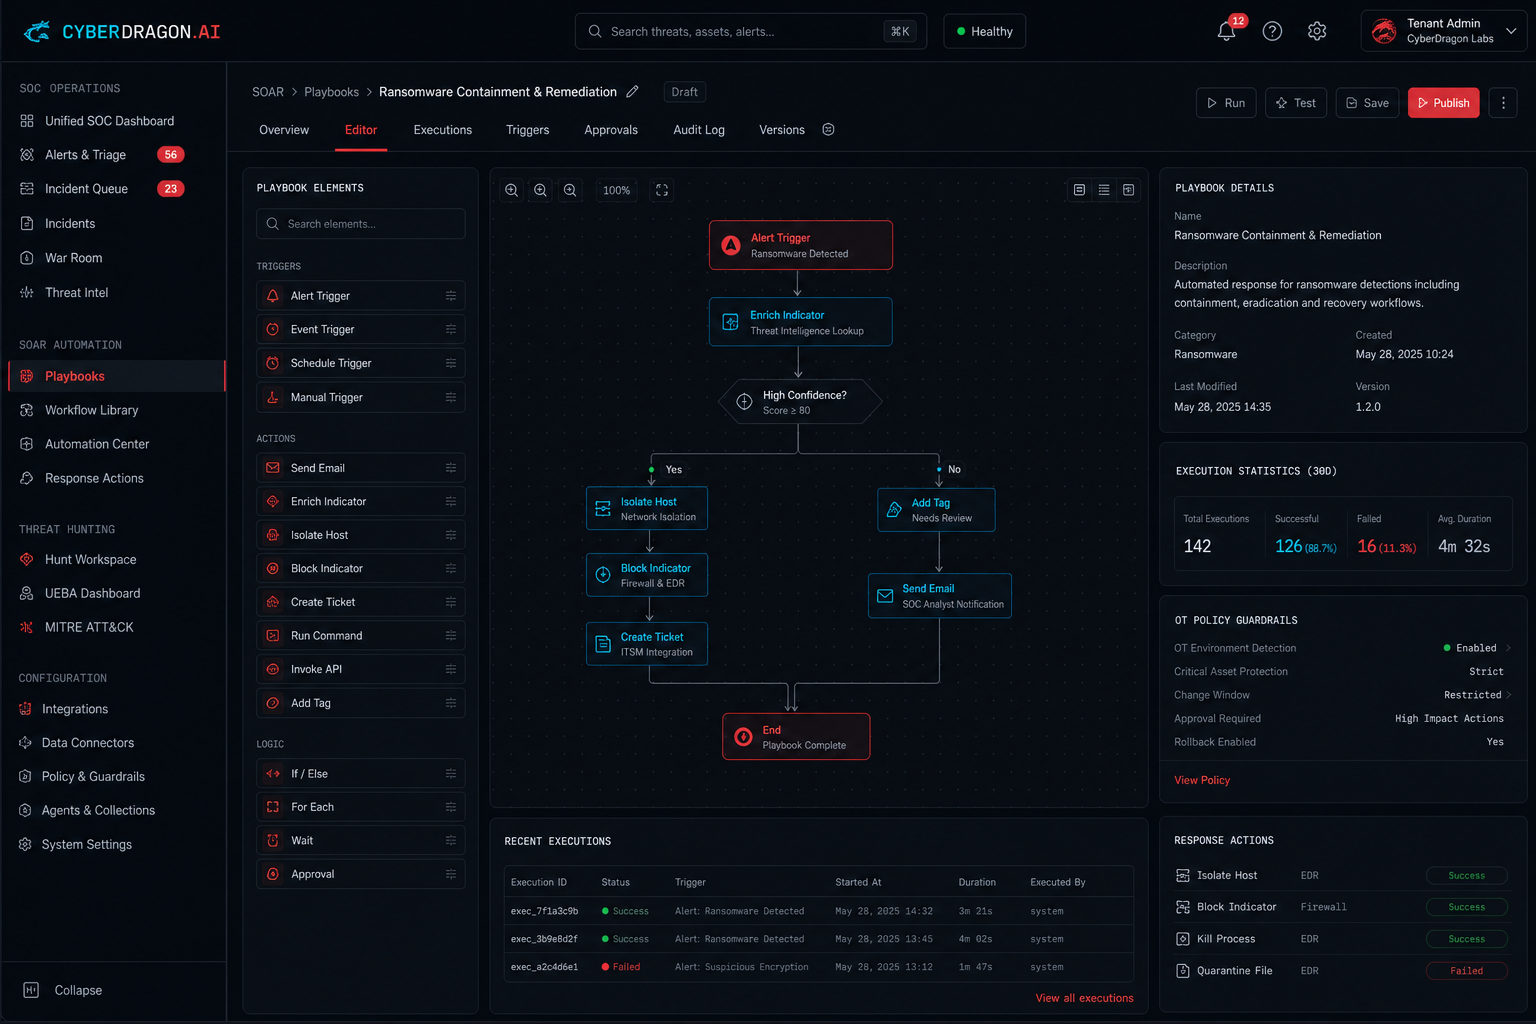
Modbus, DNP3, OPC-UA, and MQTT sessions enriched before local or Core detection.
Corporate identity and workstation telemetry joined to the same IOC matches.
AWS CloudTrail and GCP Security Command Center signals in one kill chain.
Mirrored NVD and CISA KEV data adds exposure weight to intel hits.
UEBA
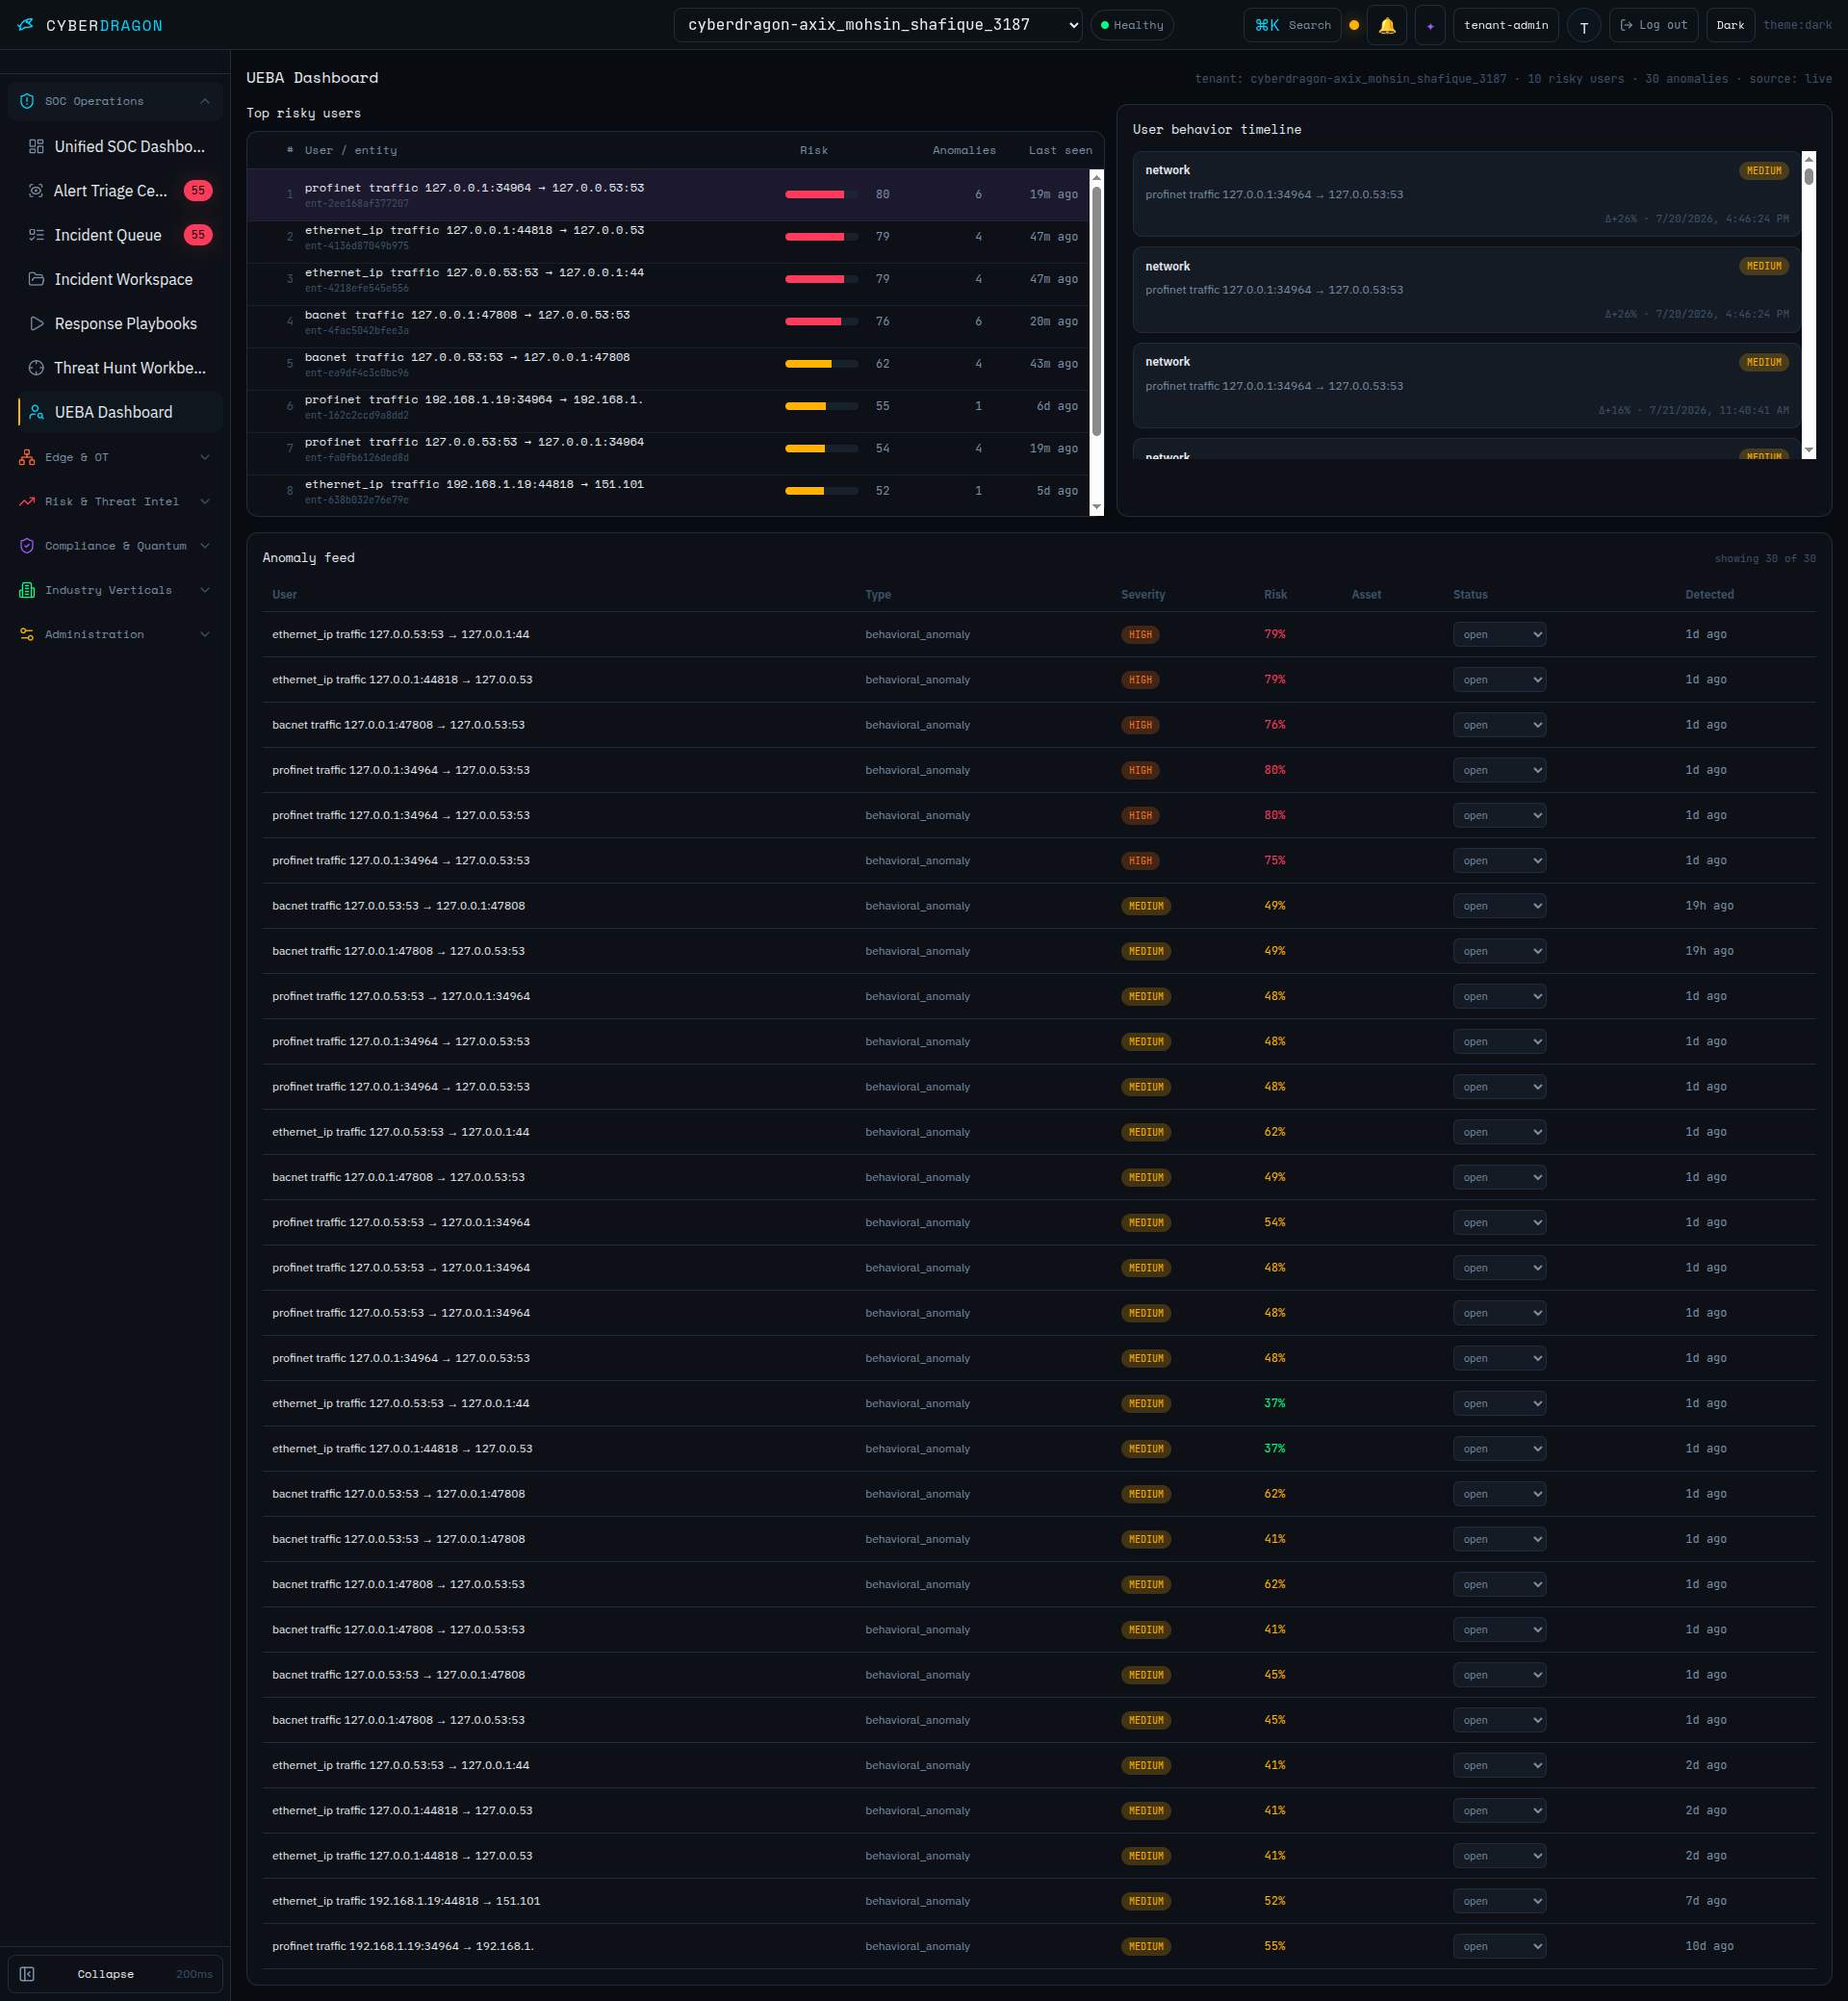
One platform, two planes — Core control plane and Edge collector for converged IT/OT.
Kafka-backed indigenous SIEM/SOAR — ingest, detection, risk, compliance, and response.
Passive SPAN capture at the industrial DMZ — telemetry up only, no PLC agents.
Modbus, DNP3, OPC-UA, and MQTT parsed natively at Purdue L3.
Indigenous global SIEM and Temporal-orchestrated SOAR with human approval gates.
W15 / W60 / W24 cascading windows across MITRE ATT&CK and ICS tactics.
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.