
SOC lab
Train on the real briefing board
- Unified SOC is the morning standup screen.
- Analysts learn triage hotkeys against live-looking queues.
- Cohort seats via contact — demo opens the trial.
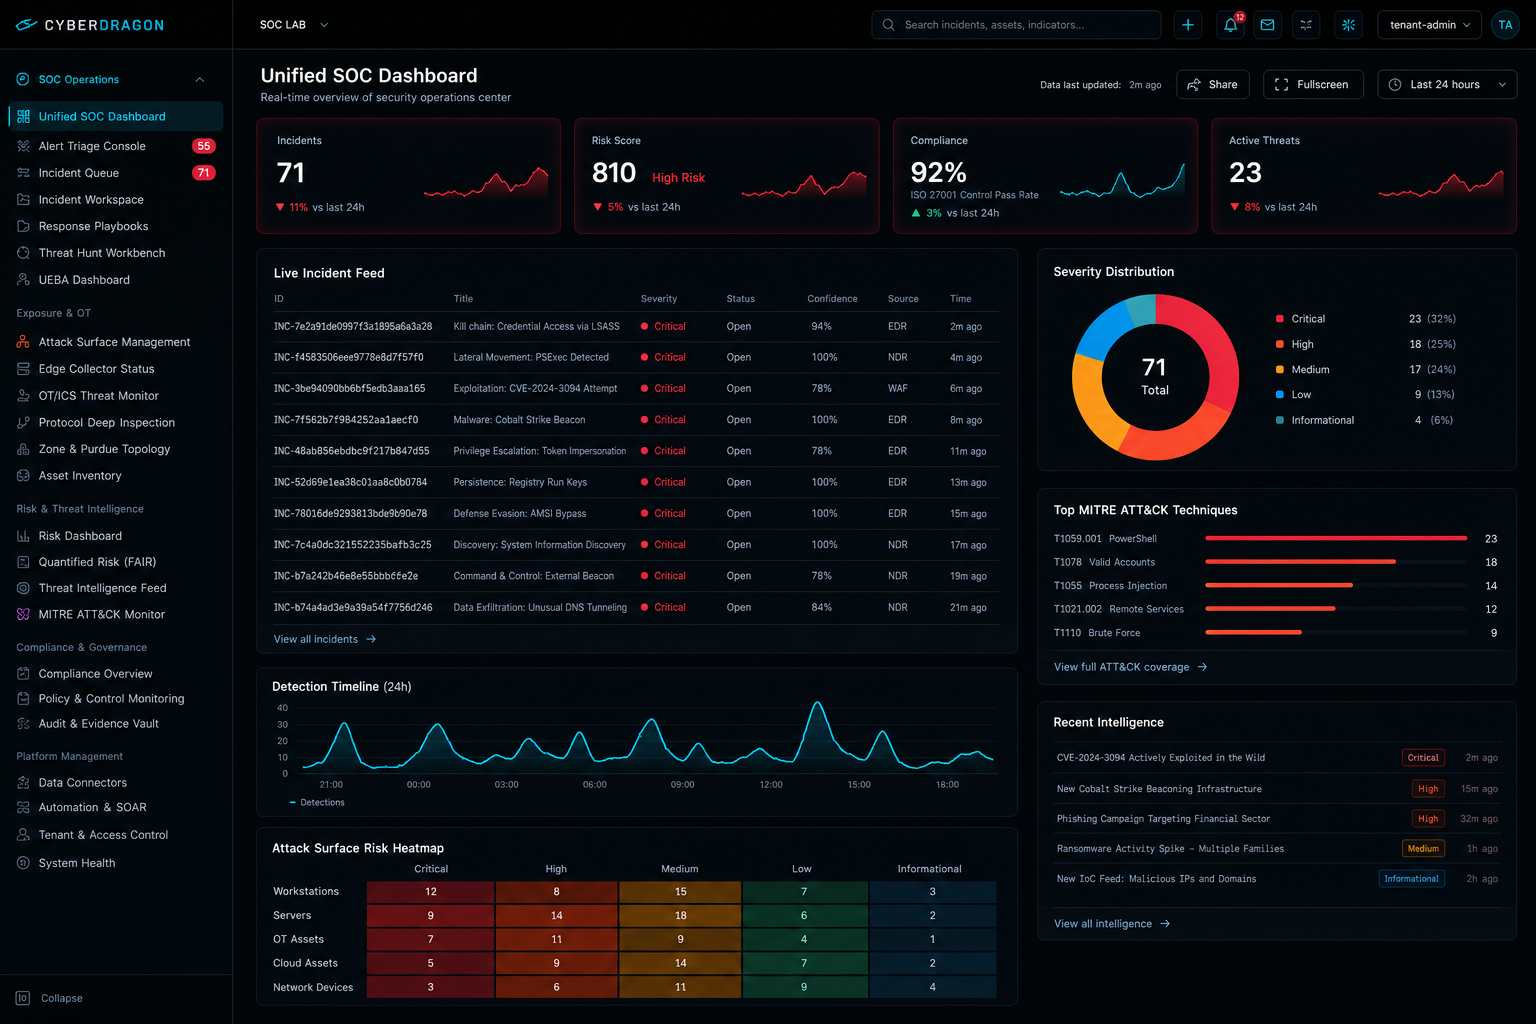
Per-student K8s namespace + simulated OT (OpenPLC + Modbus). Target: MTTD under 60 seconds for Tier 1 attacks.
SOC lab
Every exercise executes against simulated OT traffic in an isolated namespace, so a mistake costs a lab reset — never a process upset.
Hunt
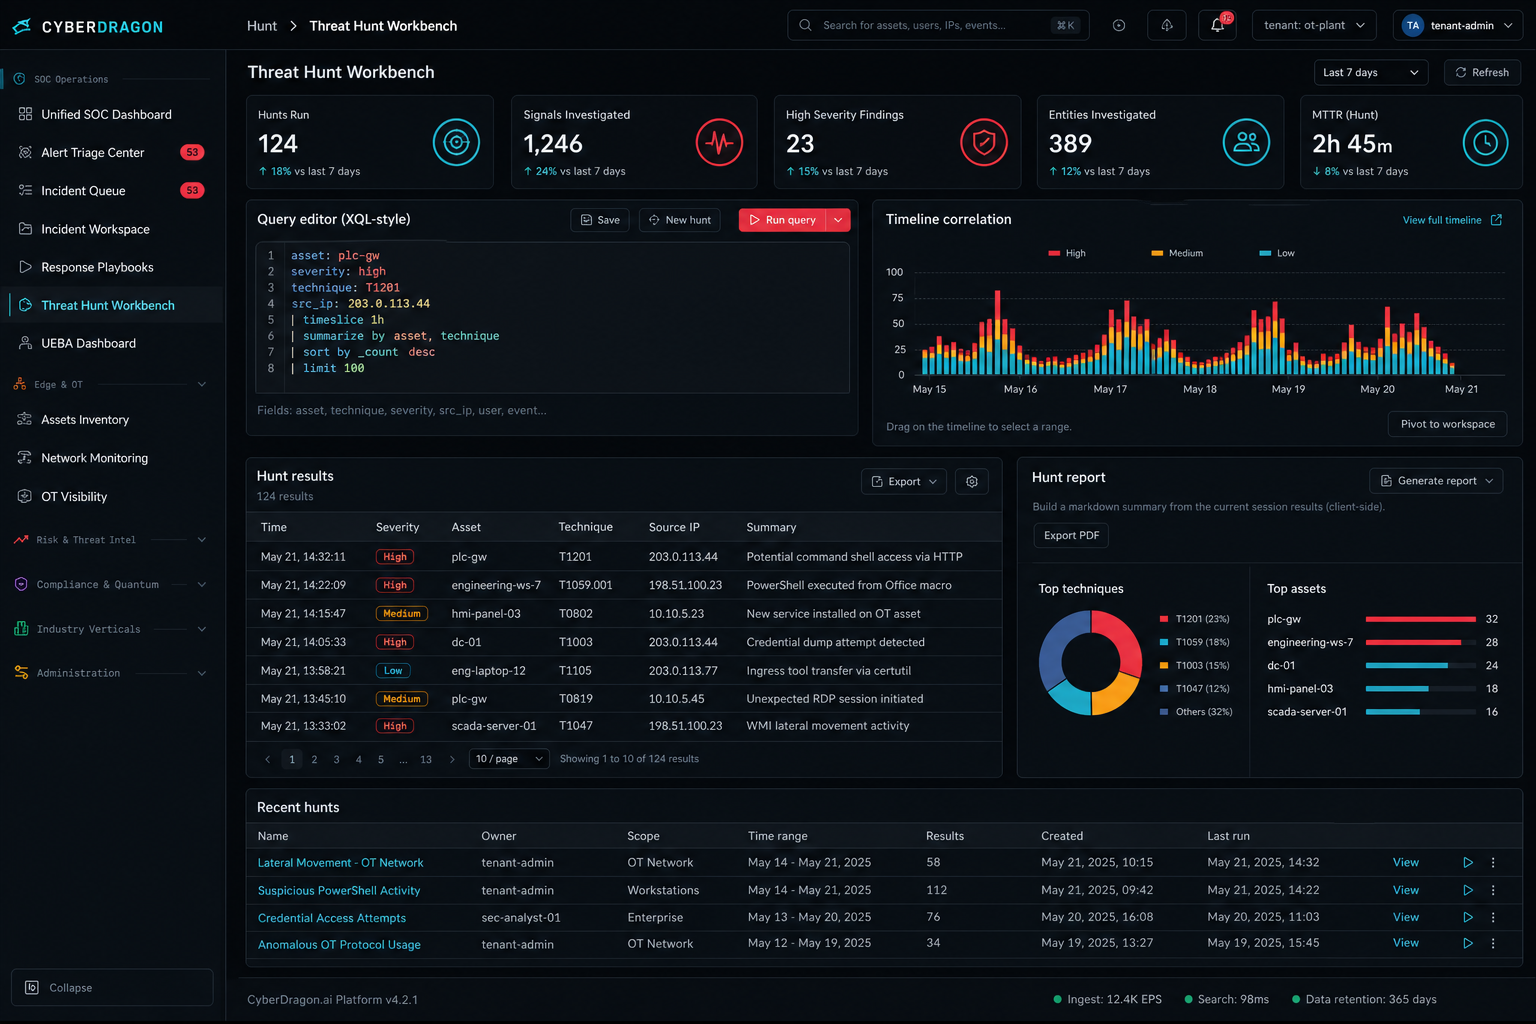
| Module group | Screens covered |
|---|---|
| SOC Operations | Unified SOC, Alert Triage, Incident Queue, Workspace, Playbooks, Threat Hunt, UEBA |
| Edge & OT | Collector Status, Protocol Inspector, Purdue Topology, Fleet Management |
| Risk & Threat Intel | Risk Dashboard, FAIR Quant, Threat Ops Queue, TI Fusion Center |
| Compliance & Quantum | Quantum Readiness, Compliance & Audit, Network Assurance, Governance Rollup |
| Industry Verticals | OT/Energy, Banking, Cloud, IIoT, Healthcare, Unified SOC Queue |
| Executive | CISO Executive, Board Risk Brief, Verticals Overview, Executive Briefing |
| MSSP & Partners | Cross-Tenant Ops, Client Onboarding, Marketplace |
Playbooks
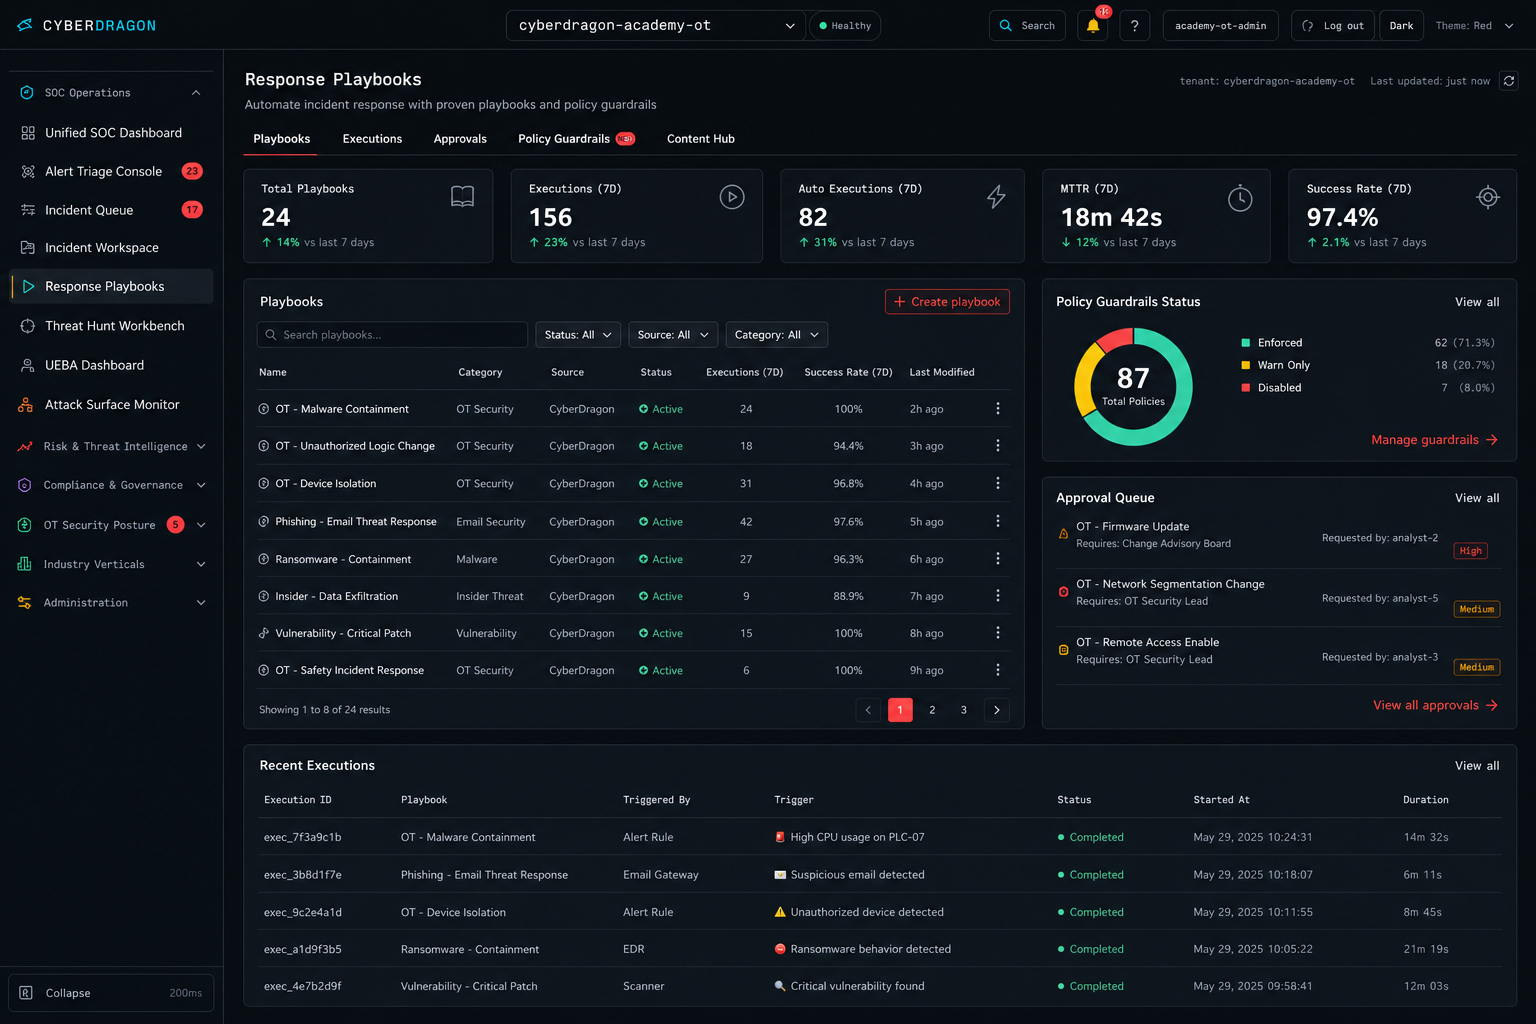
Start the 7-day free trial, then ask the team about Academy seats.