Config
Platform and ingest health
- Syslog, Splunk HEC, STIX/TAXII, webhooks and CyberDragon augments.
- You do not have to rip the SIEM you already run.
- OIDC/SAML federation when the estate requires it.
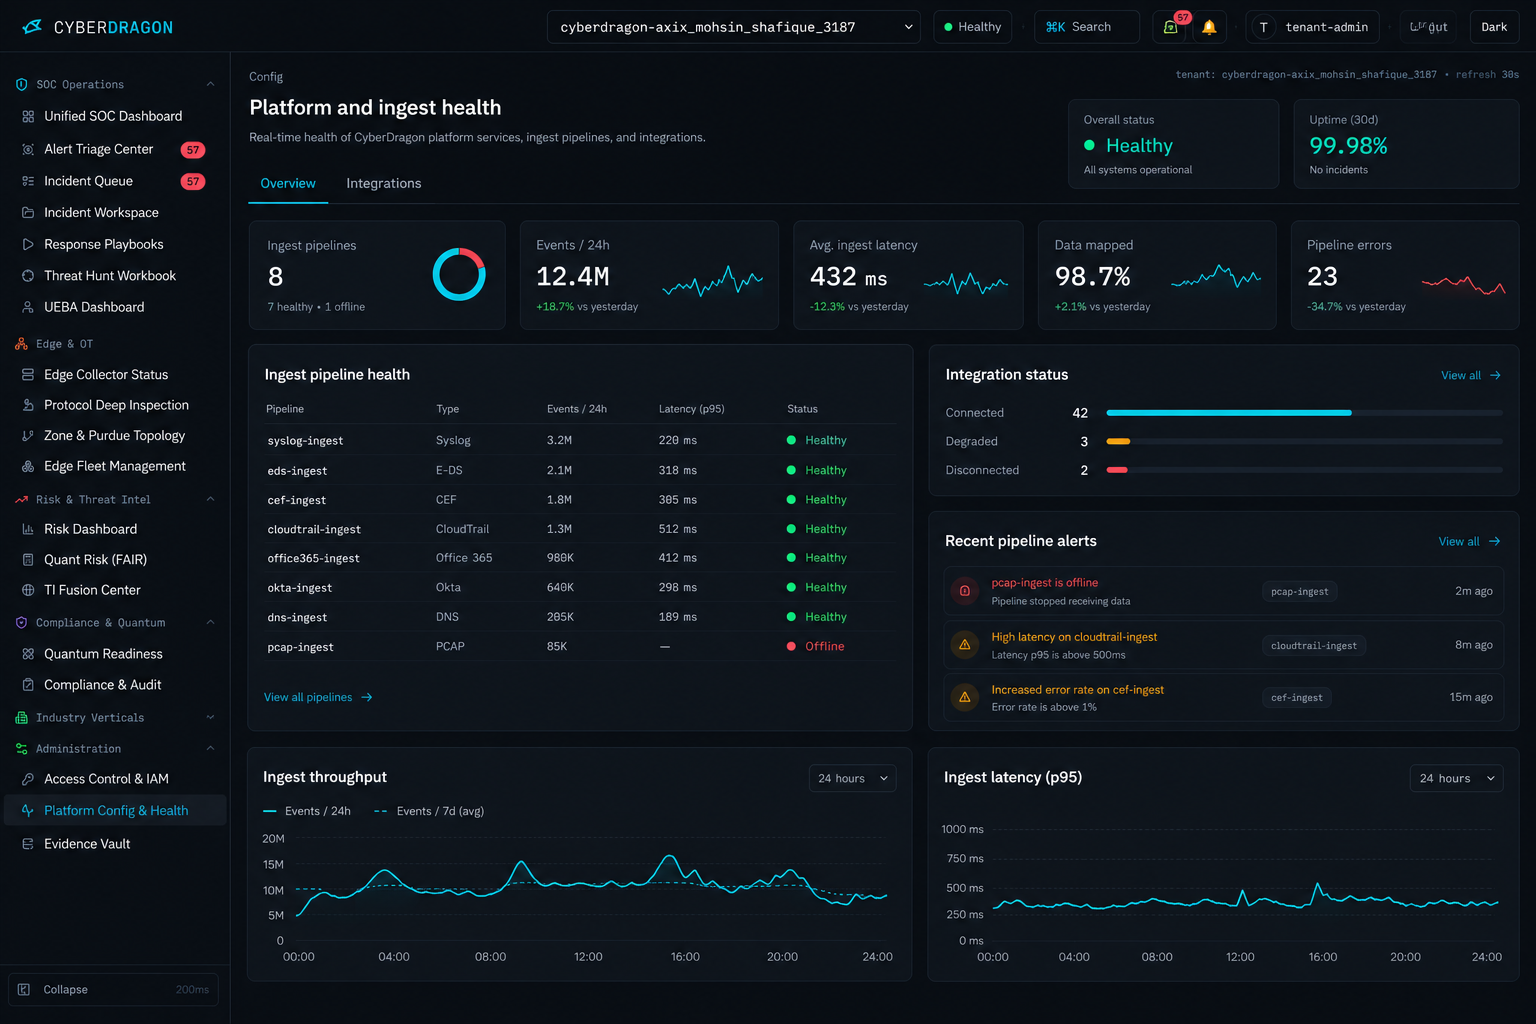
Syslog, Splunk HEC, STIX/TAXII, webhooks, SCIM, and native OT protocol capture. Not a rip-and-replace.
Config
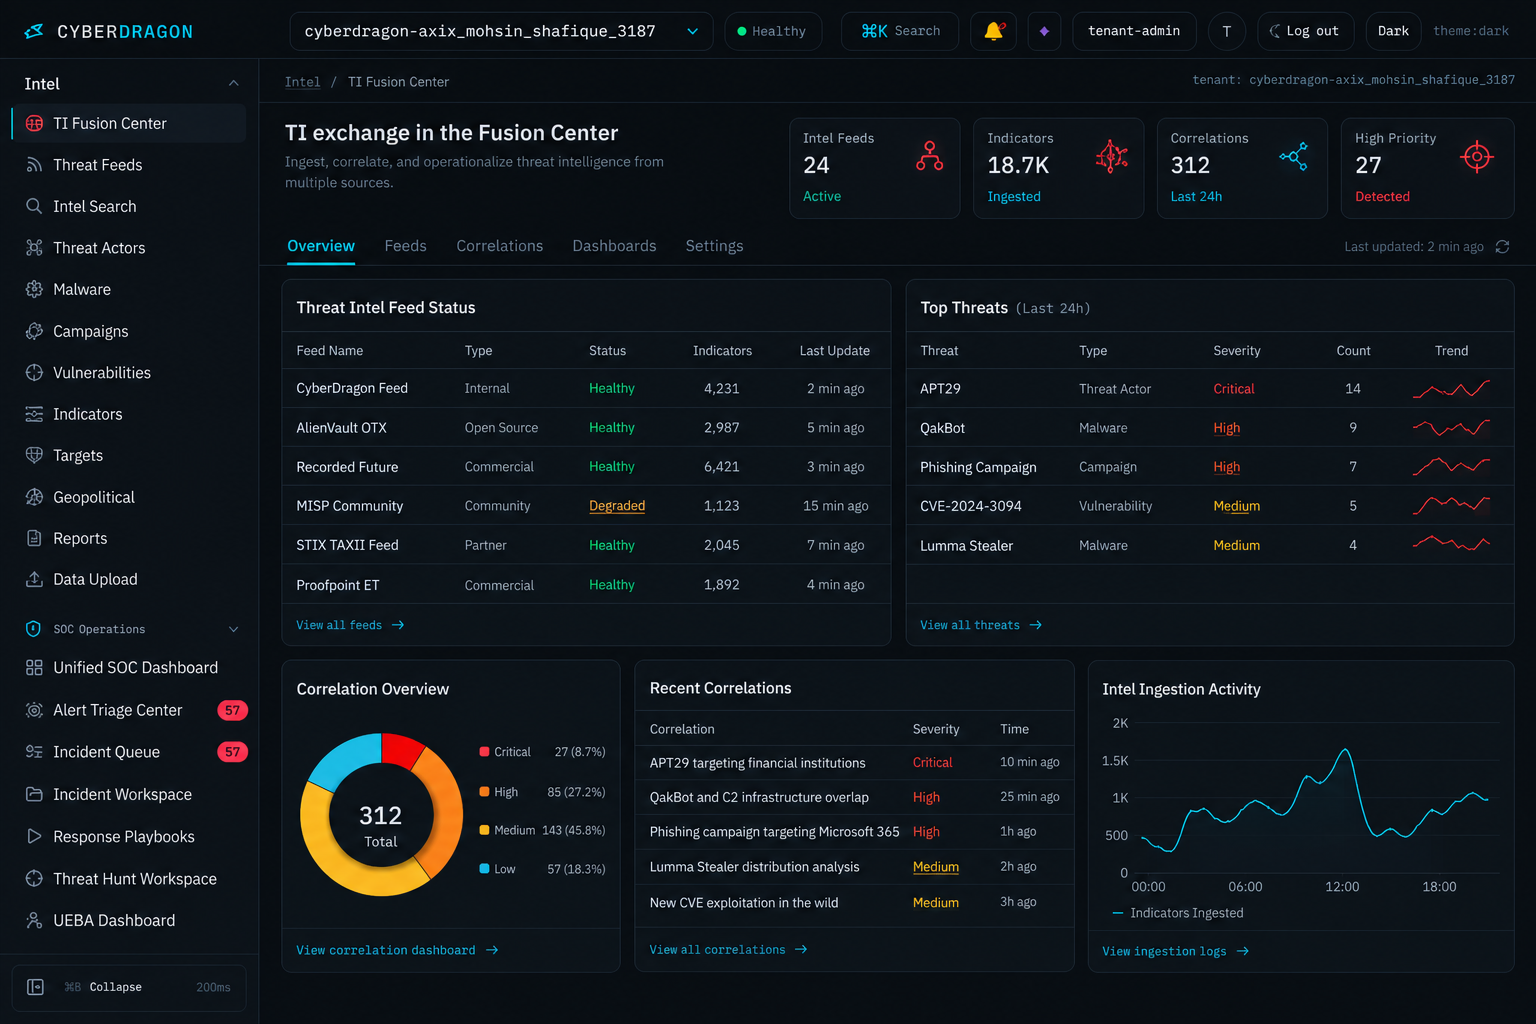
Intel
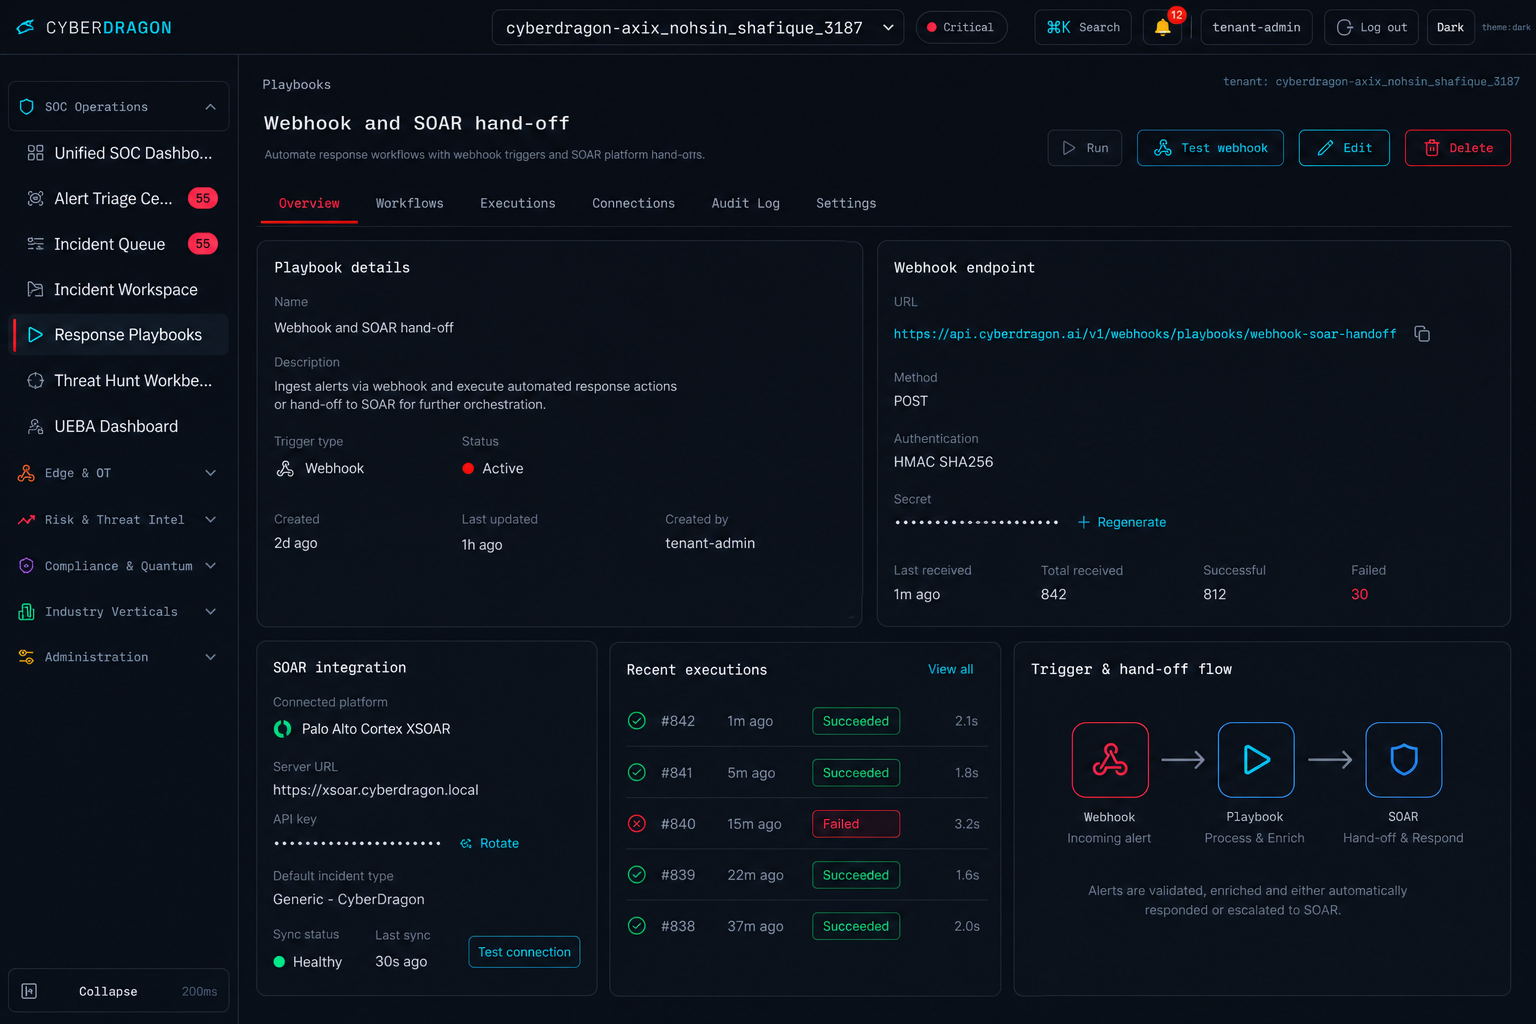
Playbooks
| Format | Typical destination | Contents |
|---|---|---|
| STIX 2.1 / TAXII2 | Threat intelligence platforms | Indicators, campaign context, and observed kill-chain sightings. |
| CEF / syslog | SIEM and log pipelines | Normalised detections with tenant, asset, and Purdue-zone fields. |
| Splunk HEC | Splunk indexes | Correlated incidents rather than raw event noise. |
| Signed evidence ZIP | Auditors and regulators | Hash-chained records, Ed25519 signatures, and OPA policy reason codes. |
| Webhooks | ITSM, chat, and automation | Incident lifecycle events with approval and denial transitions. |
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.