Vault
Hash-chained Evidence Vault
- Verify chain. Export an auditor packet.
- Ed25519-signed, tamper-evident.
- Tenant-admin and auditors get export; operators do not mix client evidence.
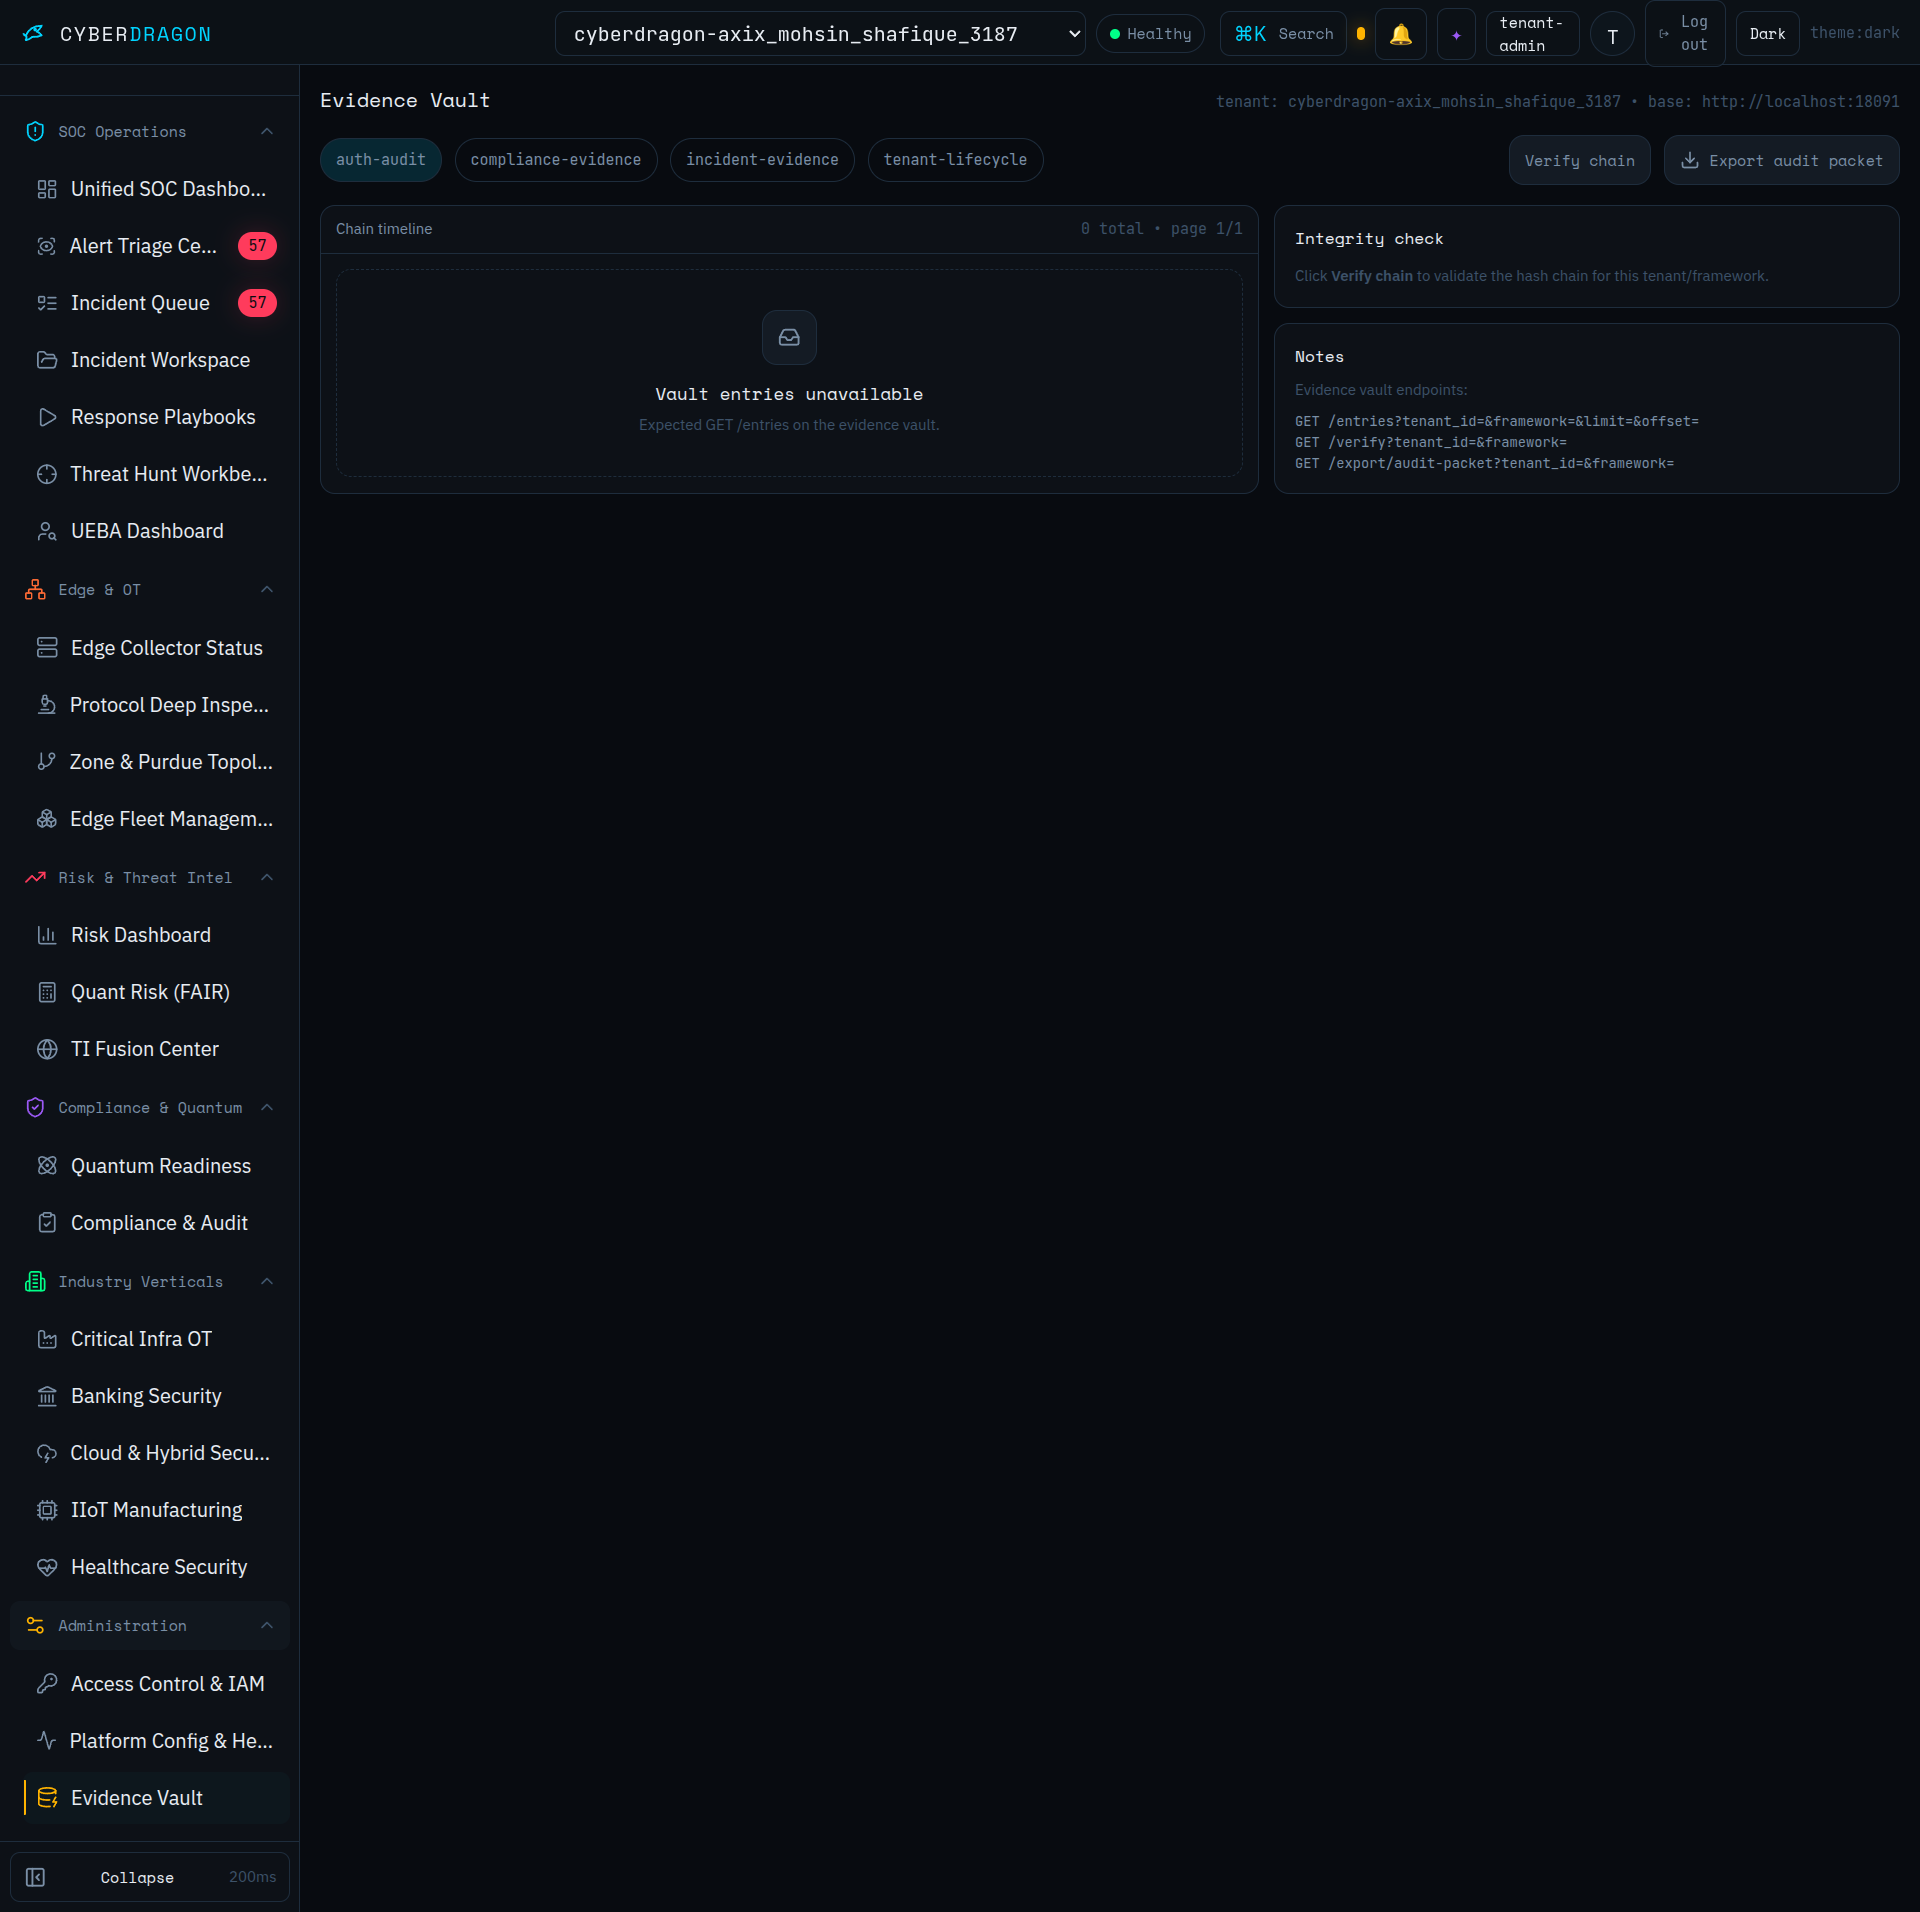
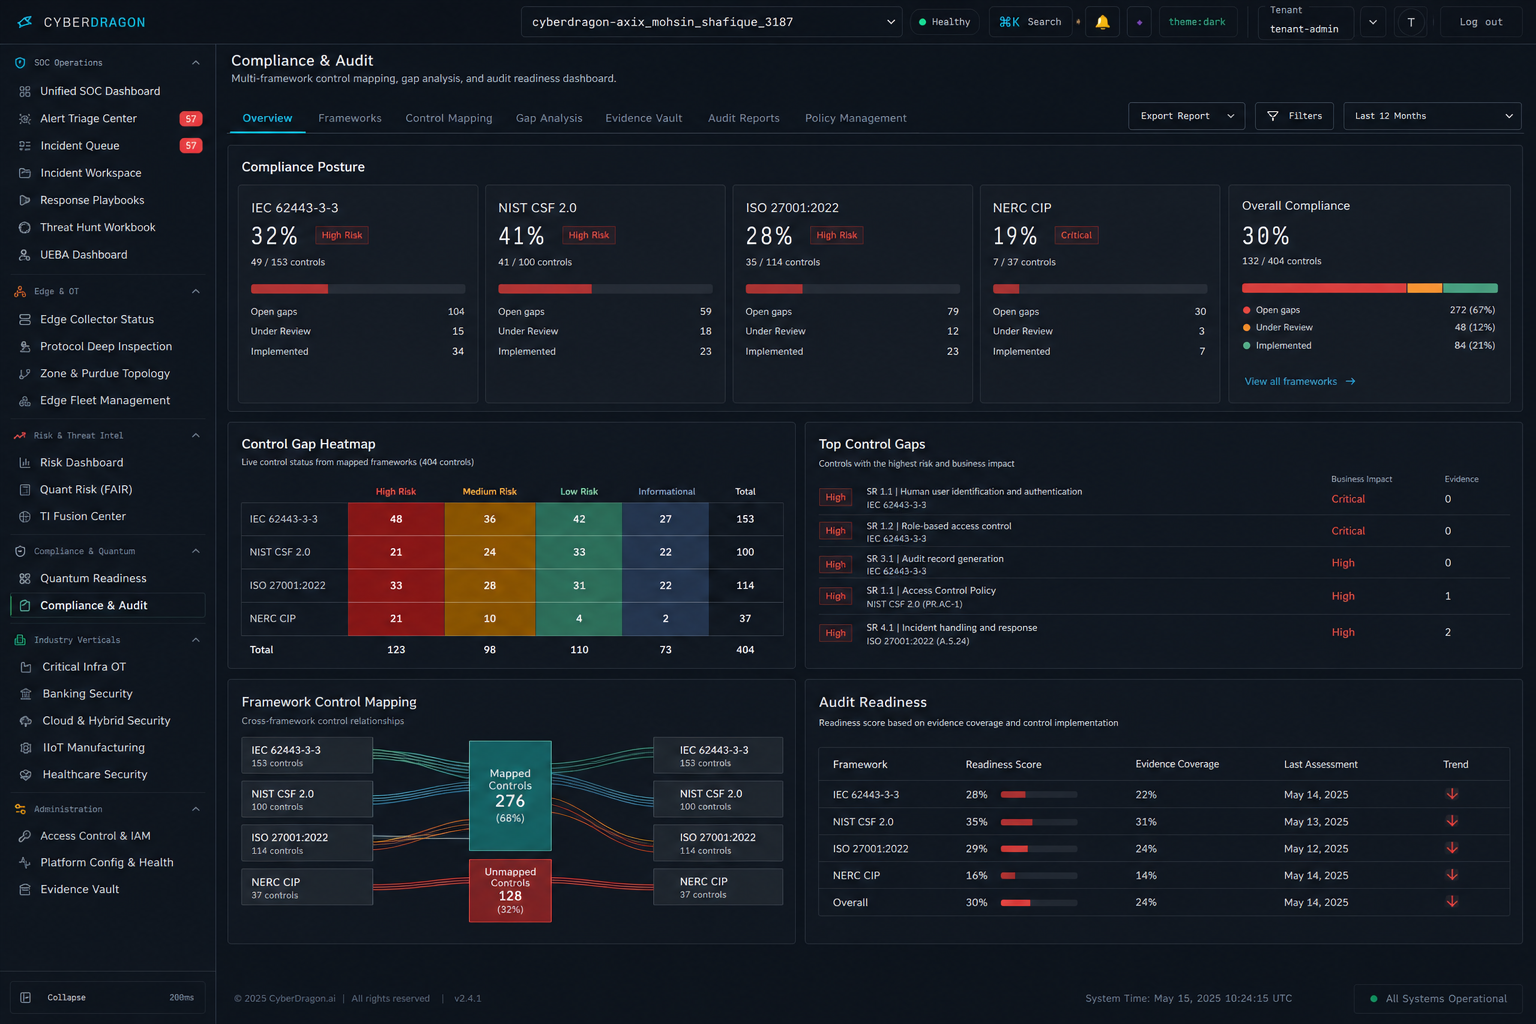
Detections, response actions, approvals, and policy denials are hash-chained and Ed25519-signed. Distinct evidence theme and not the same layout as Core or Edge.
Detection, response action, and approval decisions are written as immutable records.
Each record is hashed and chained to its predecessor and any edit breaks the chain.
Ed25519 signatures seal the chain using Vault-backed key material.
Chain verification runs on demand; lab run verified 66 entries OK.
Auditor-ready ZIP packets with policy reason codes, including OT denials.
Vault
Frameworks
| Field | Why it is there |
|---|---|
| Sequence and previous hash | Position in the chain. Any reordering or deletion breaks verification. |
| Tenant and actor | Which tenant, which analyst or service identity, under which RBAC tier. |
| Event references | The correlated detections and raw event IDs that justified the decision. |
| Policy decision | The OPA verdict with reason code and including denials issued after human approval. |
| Timestamps | Detection, approval, and execution times, so dwell and response are reconstructable. |
| Ed25519 signature | Seals the record using Vault-backed key material that application code never handles. |
Access
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.