Frameworks
Compliance and audit board
- IEC 62443-3-3, NERC CIP, NIST CSF 2.0, ISO 27001:2022, SOC 2.
- Gaps next to live events.
- Auto-map into the vault.
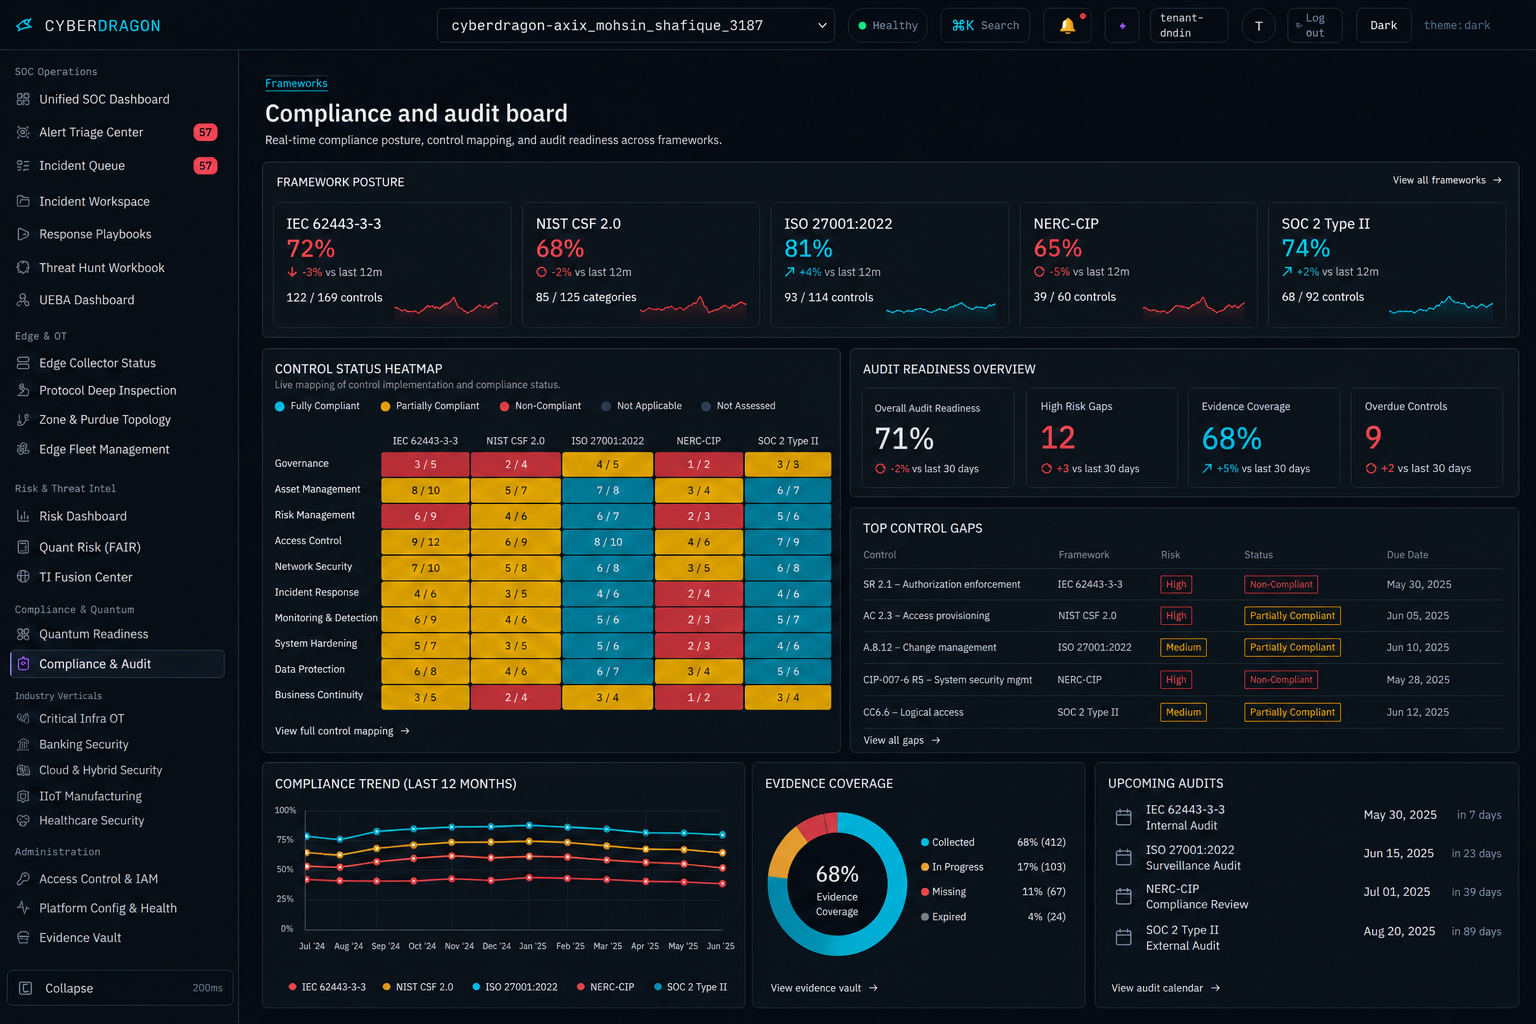
Framework packs map live events to controls automatically, so the quarterly audit is an export rather than a project.
Frameworks
A network or identity event lands in the Kafka pipeline and is normalized.
The compliance auto-mapper links the event to framework controls and around seven controls per network event.
Mapped controls are sealed into the hash-chained vault with signatures and reason codes.
Auditor packets, CISO monthly digests, and board PDFs are generated from the same records.
Quantum
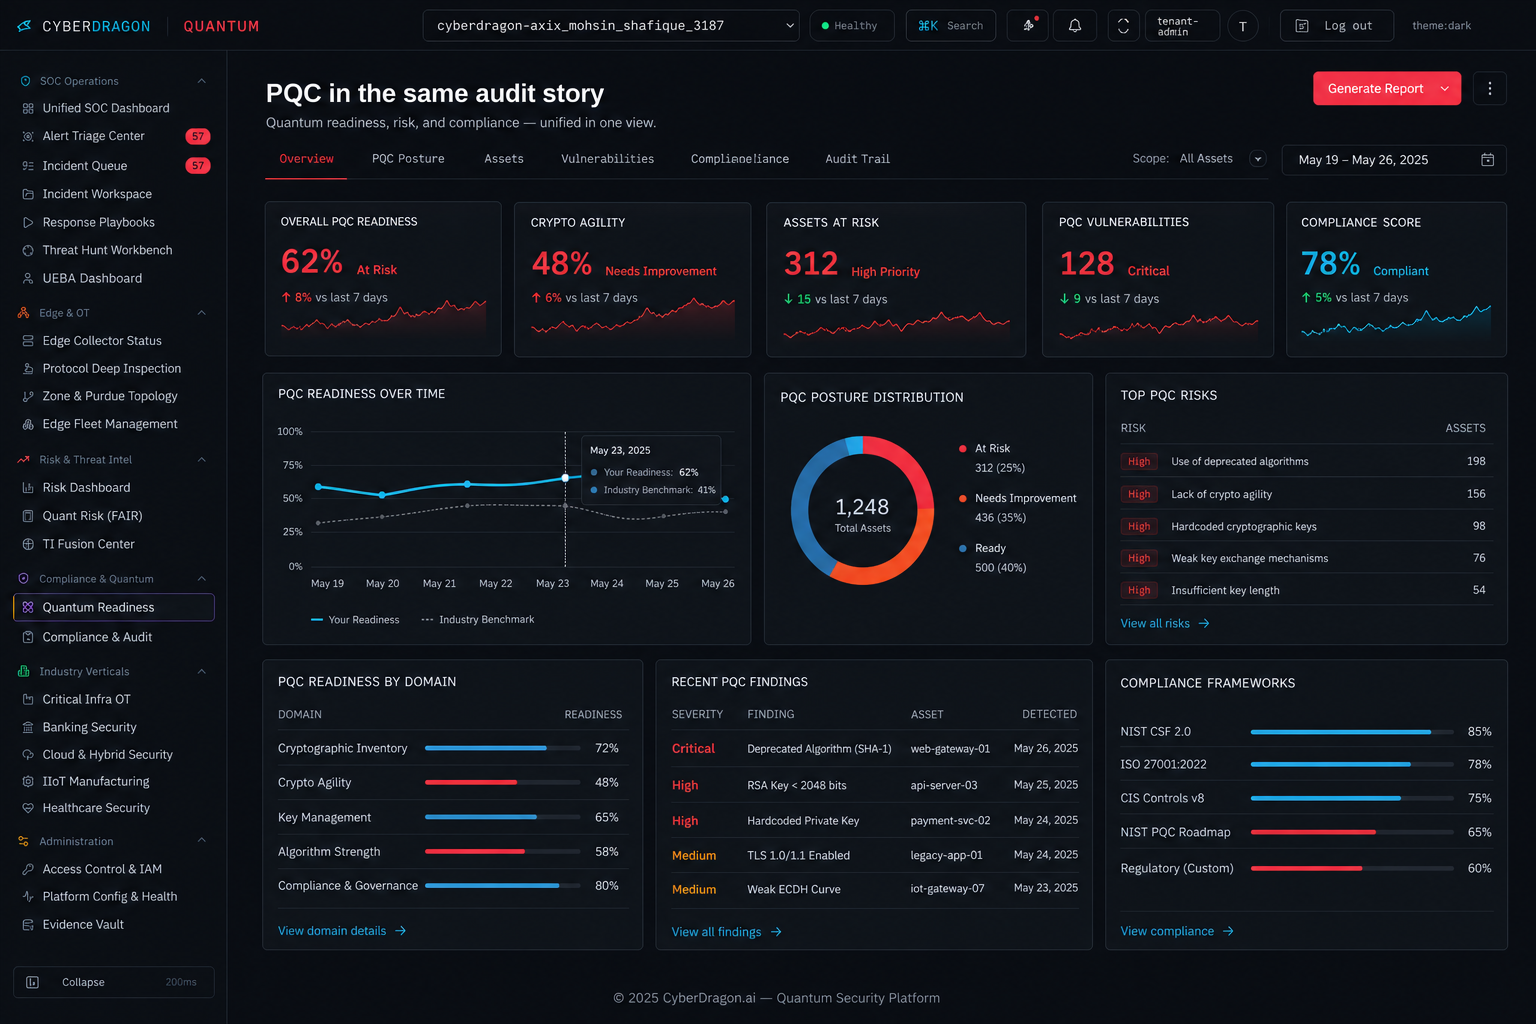
| Framework | Control | Evidence produced |
|---|---|---|
| IEC 62443-3-3 | SR 6.1 and Audit log accessibility | Hash-chained detection and approval records exportable per zone and conduit. |
| NERC CIP | CIP-007 and System security management | Protocol-level access observations tied to asset and Purdue level. |
| NIST CSF 2.0 | DE.CM and Continuous monitoring | Passive OT capture coverage with per-collector transport health. |
| ISO 27001:2022 | A.8.16 and Monitoring activities | Correlated incidents with analyst decisions and timestamps. |
| SOC 2 | CC7.2 and Anomaly detection | Kill-chain incidents with W15/W60/W24 window provenance. |
| IEC 62443-3-3 | SR 5.1 and Network segmentation | Zone-crossing events flagged against your declared conduit map. |
Export
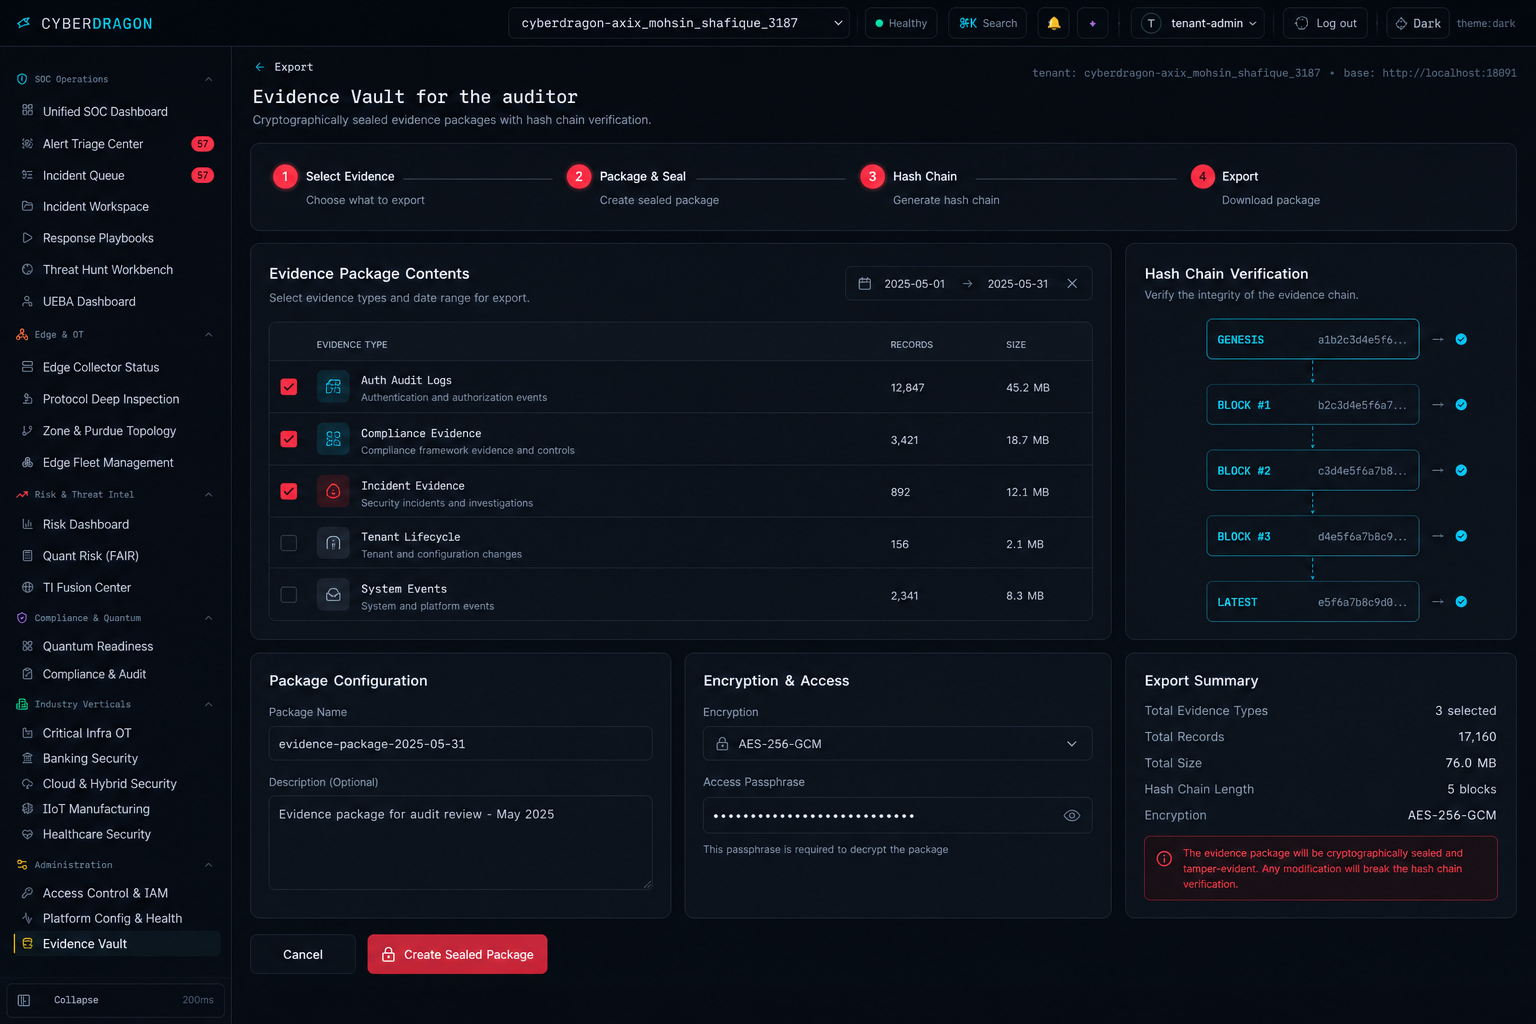
Detection, response action, and approval decisions are written as immutable records.
Each record is hashed and chained to its predecessor and any edit breaks the chain.
Ed25519 signatures seal the chain using Vault-backed key material.
Chain verification runs on demand; lab run verified 66 entries OK.
Auditor-ready ZIP packets with policy reason codes, including OT denials.
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.