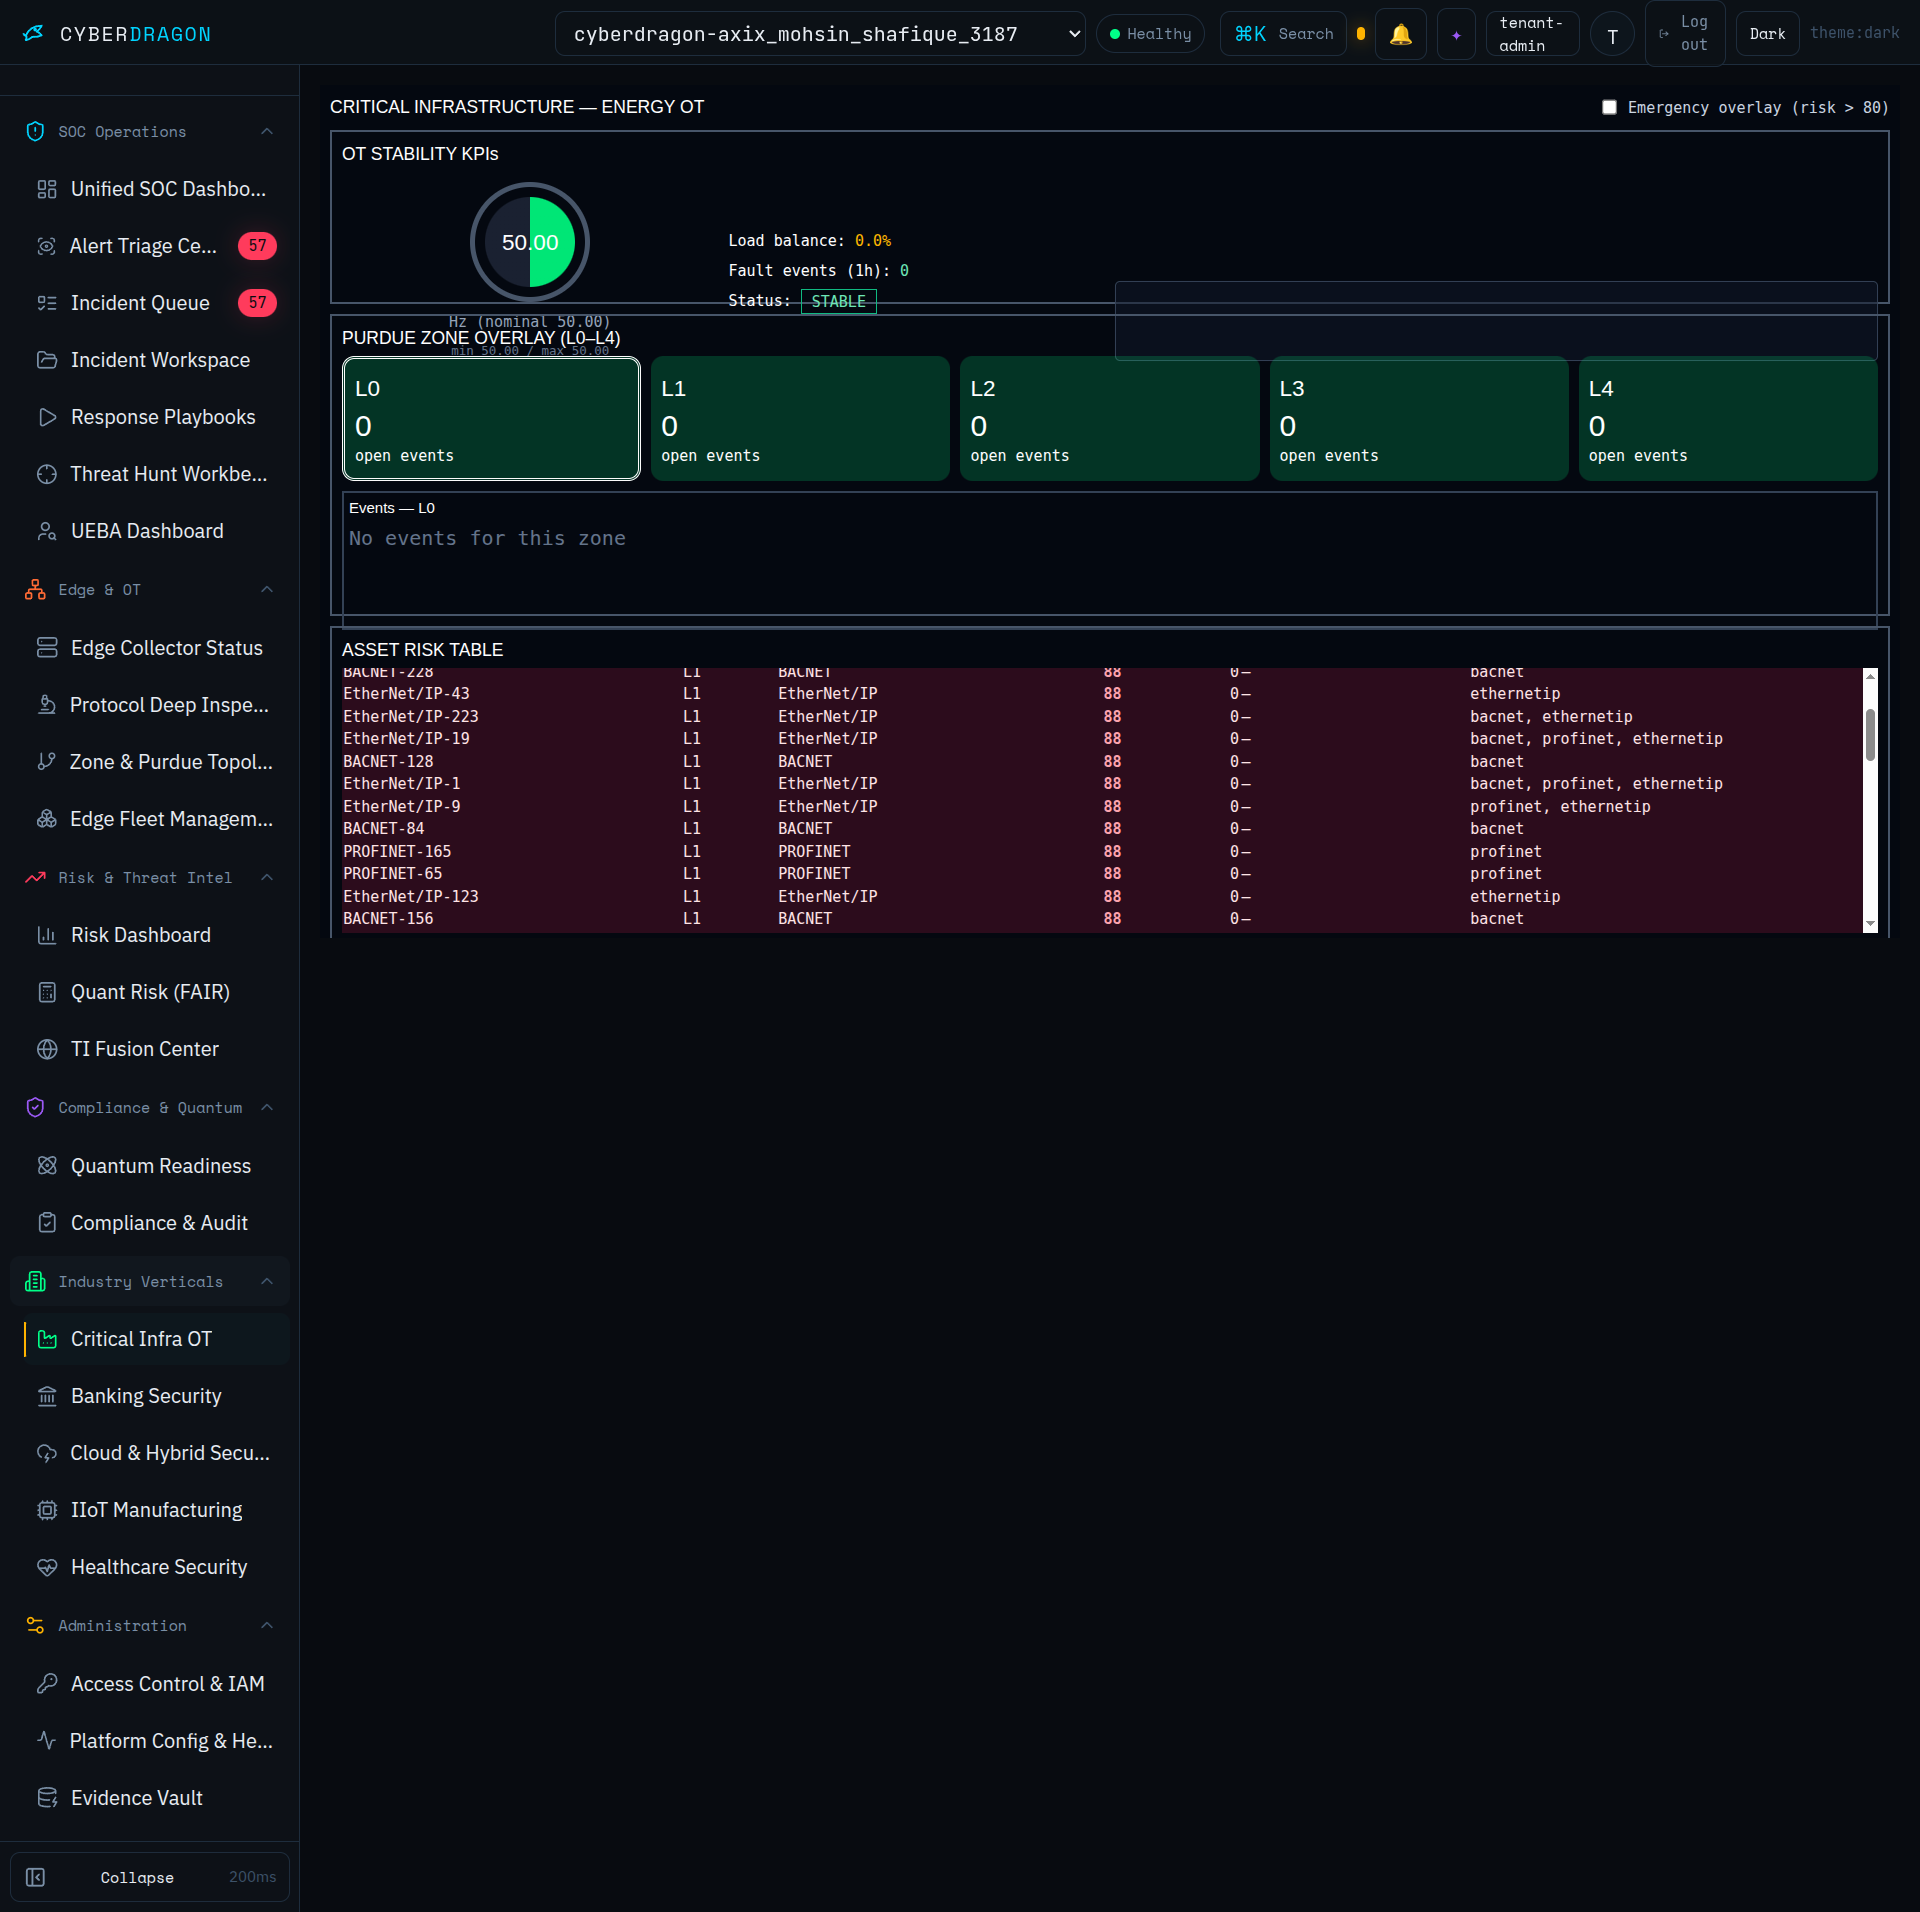
Critical infrastructure
OT for grids and CI
- Passive Edge at generation, transmission, and remote cells.
- NERC CIP evidence without agents on the SIS.
- Nation-state dwell needs W24 windows and Threat Atlas context.
Zone-aware, quantum-resilient cyber defense by vertical and same Core + Edge indigenous SIEM/SOAR stack, industry-specific pain, regs, Threat Atlas context, and evidence.
Quantum-resilient cyber defense for generation, transmission, and distribution and passive Edge capture at the industrial DMZ, NERC CIP evidence, and no command plane into L0–L2 or the SIS.
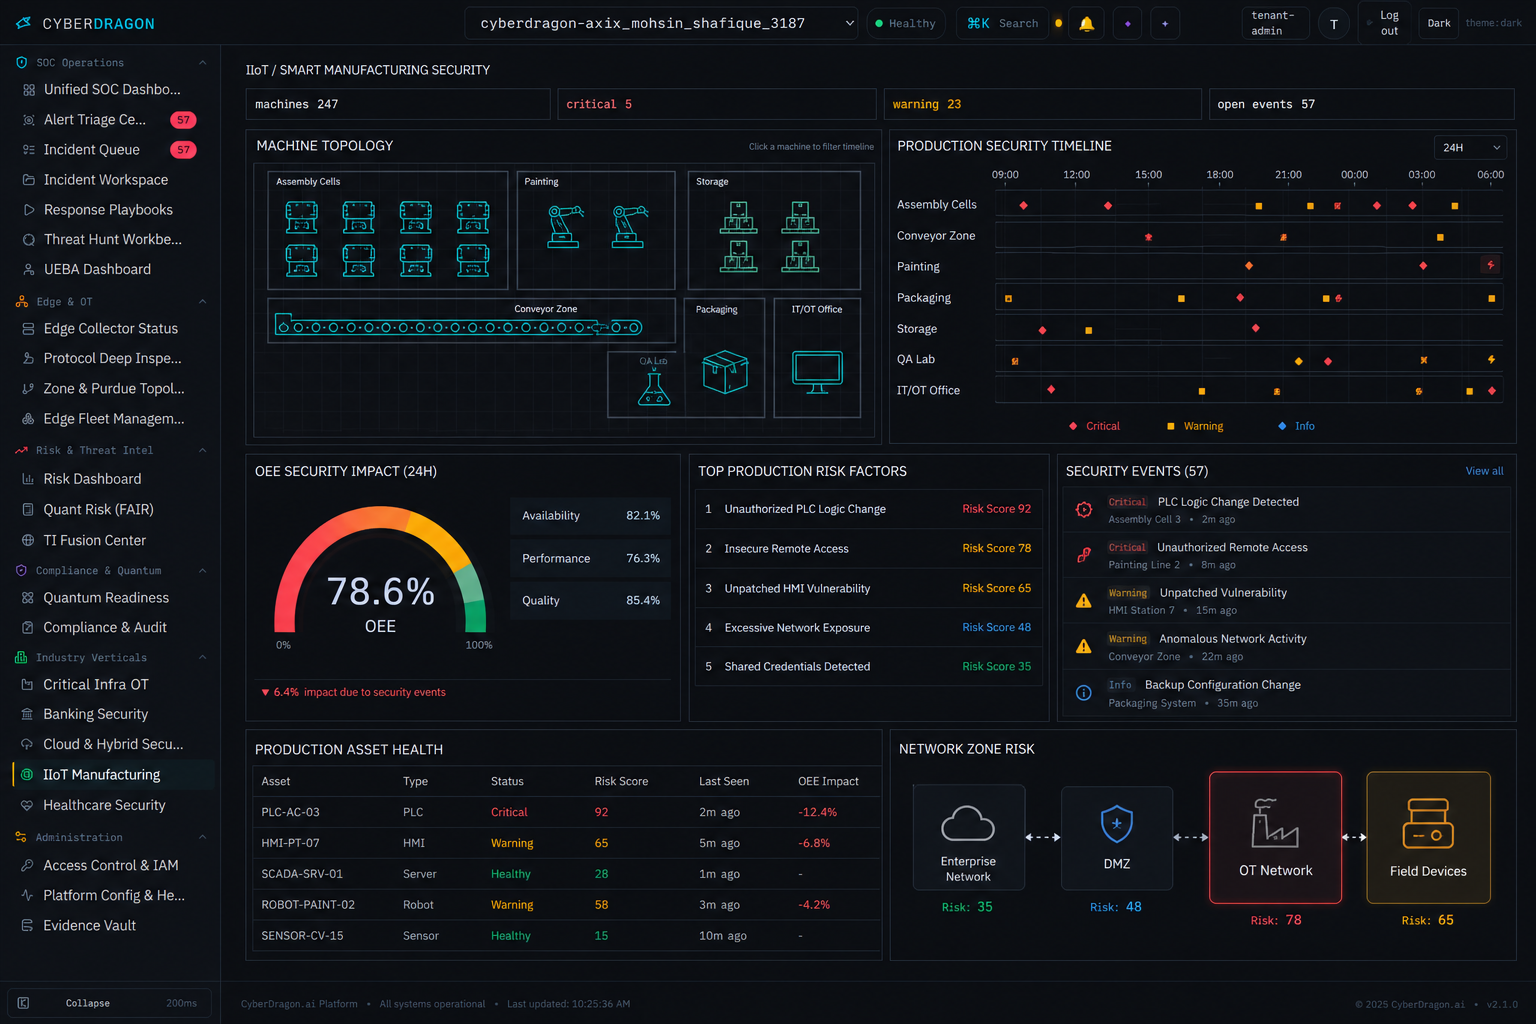
Industry 4.0 and smart-factory cyber defense that treats Modbus writes and OPC-UA session changes as first-class SOC signals and not afterthoughts bolted onto an endpoint stack.
Quantum-resilient cyber defense for banks and financial groups and passive Edge capture at branch OT corridors, SWIFT and PCI-aligned evidence, and Enterprise→OT correlation without agents on trading or core systems.
Agentless visibility for connected clinical and facilities devices and passive capture that never installs on FDA-cleared equipment, with PHI-adjacent network risk in one kill-chain SOC.
Built for operators facing long APT dwell, supply-chain compromise, and national CI policy and with W24 kill-chain windows, live hybrid PQC identity, and Threat Atlas awareness.
Structural multi-tenancy for managed providers who need OT protocol depth, kill-chain SIEM/SOAR, and client SLAs and without stacking five tools per industrial account.
Critical infrastructure
| Sector | Primary pain | How CyberDragon answers it | Frameworks |
|---|---|---|---|
| Energy & Utilities | SIS and safety-system exposure when security tools demand agents or active probing | Passive Edge SPAN capture at IEC 62443 L3 / industrial DMZ and Modbus, DNP3, OPC-UA, MQTT | IEC 62443, NERC CIP |
| Manufacturing & IIoT | Unauthorized Modbus / DNP3 writes that alter setpoints or recipes before anyone notices | Native Modbus, DNP3, OPC-UA, MQTT parsing at the Edge and no agents on PLCs or robots | ISO 27001, NIST CSF |
| Banking & Finance | Branch OT and facilities systems invisible to endpoint-first stacks | Banking vertical dashboard with branch OT and corporate identity on one timeline | PCI DSS, SWIFT CSP, ISO 27001 |
| Healthcare | Connected medical device and IoMT sprawl with no supported agent path | Healthcare vertical + asset identification without device agents | HIPAA-style programs |
| Critical Infrastructure | Long APT dwell across enterprise identity and OT corridors | TI fusion + cascading W15 / W60 / W24 kill-chain windows | National CI frameworks |
| MSSP | Margin pressure from tool sprawl across endpoint, SIEM, and OT vendors | PostgreSQL RLS structural isolation across managed tenants | Client contract SLAs |
MSSP
Framework packs and dashboards change by sector. The collection model, correlation windows, and evidence chain do not.
Edge mirrors traffic from a SPAN port or hardware TAP at the industrial DMZ and parses OT protocols locally.
Events land in a SQLite WAL store-and-forward queue (~5,000 events) so a link outage never loses telemetry.
HMAC-SHA256 signed batches, optionally mTLS, are shipped to Core over the ingest network only.
Threat-intel fusion adds OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise context in flight.
Cascading W15 / W60 / W24 windows assemble events into kill chains and flag Enterprise→OT pivots explicitly.
Risk scoring, compliance auto-mapping, and Temporal playbooks with human approval and OPA guardrails.
Detections, approvals, and denials are hash-chained and Ed25519-signed into the evidence vault.
Manufacturing
Healthcare
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.