CyberDragon Core is live — indigenous SIEM/SOAR with Edge protocol capture. Start a 7-day free trial on your own traffic →
Banking & Finance · Global cyber defense

Branch OT and core banking in one kill chain

Quantum-resilient cyber defense for banks and financial groups — passive Edge capture at branch OT corridors, SWIFT and PCI-aligned evidence, and Enterprise→OT correlation without agents on trading or core systems.

The challenge

What Banking & Finance operators face on the Enterprise→OT corridor.

Attackers do not respect the DMZ. Banking & Finance estates need quantum-resilient cyber defense that treats OT protocols, Industry 4.0 cells, and corporate identity as one kill chain — with evidence auditors can trust.

Branch OT and facilities systems invisible to endpoint-first stacks

SWIFT CSP and PCI DSS evidence scattered across SIEM, GRC, and manual exports

Corporate identity abuse that pivots into building automation or ATM back-office networks

Regulators asking about crypto agility while legacy tools still show a 2030 PQC slide

Banking vertical

Branch OT and corporate identity

  • Banking security dashboard with branch OT and enterprise kill-chain context.
  • PCI and SWIFT-oriented controls mapped from live events.
  • No agents on core banking or trading systems.
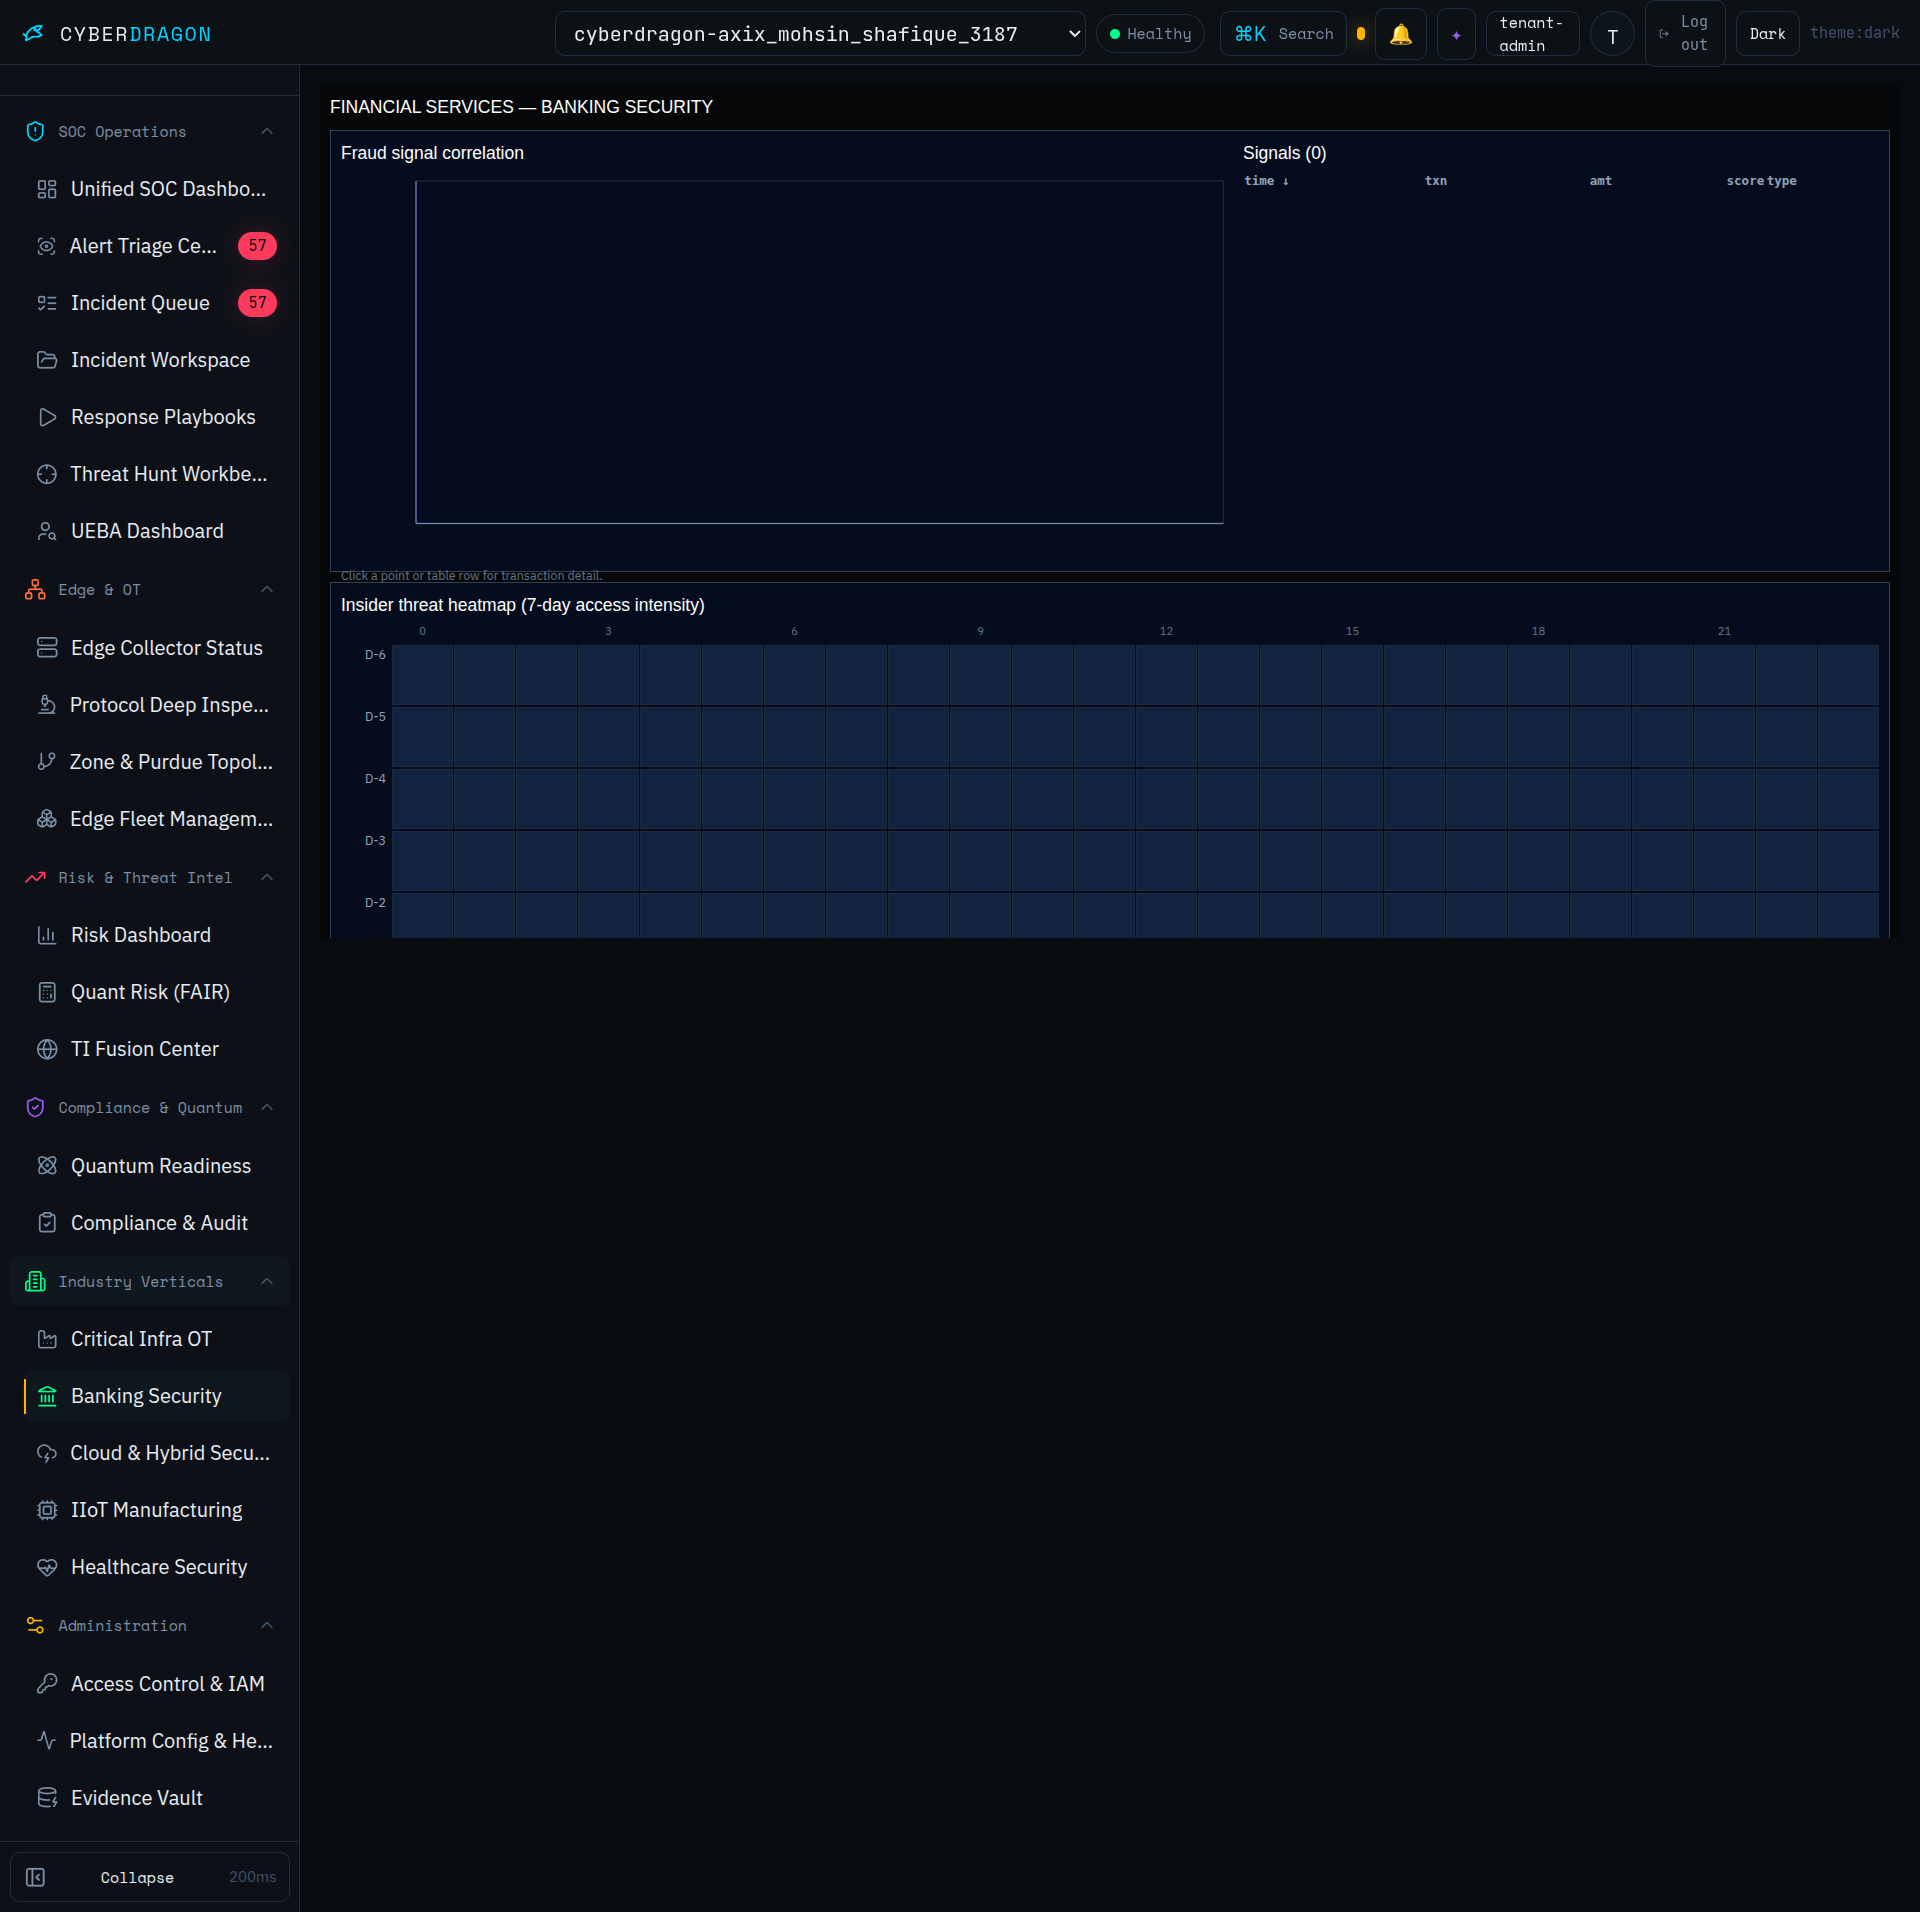
CyberDragon Banking security dashboard
How CyberDragon helps

Unified SIEM/SOAR, Edge capture, and zone-aware policy for Banking & Finance.

Banking vertical dashboard with branch OT and corporate identity on one timeline

Passive Edge SPAN capture at branch DMZs — no agents on core banking systems

PCI DSS, SWIFT CSP, and ISO 27001 controls auto-mapped into the evidence vault

Hybrid PQC identity (ML-DSA-65 + Ed25519) live today for regulated sessions

Dedicated single-tenant and sovereign on-prem Core for national and regional banks

Regulatory alignment: PCI DSS, SWIFT CSP, ISO 27001. Controls auto-map from live events into the tamper-evident evidence vault.

Identity
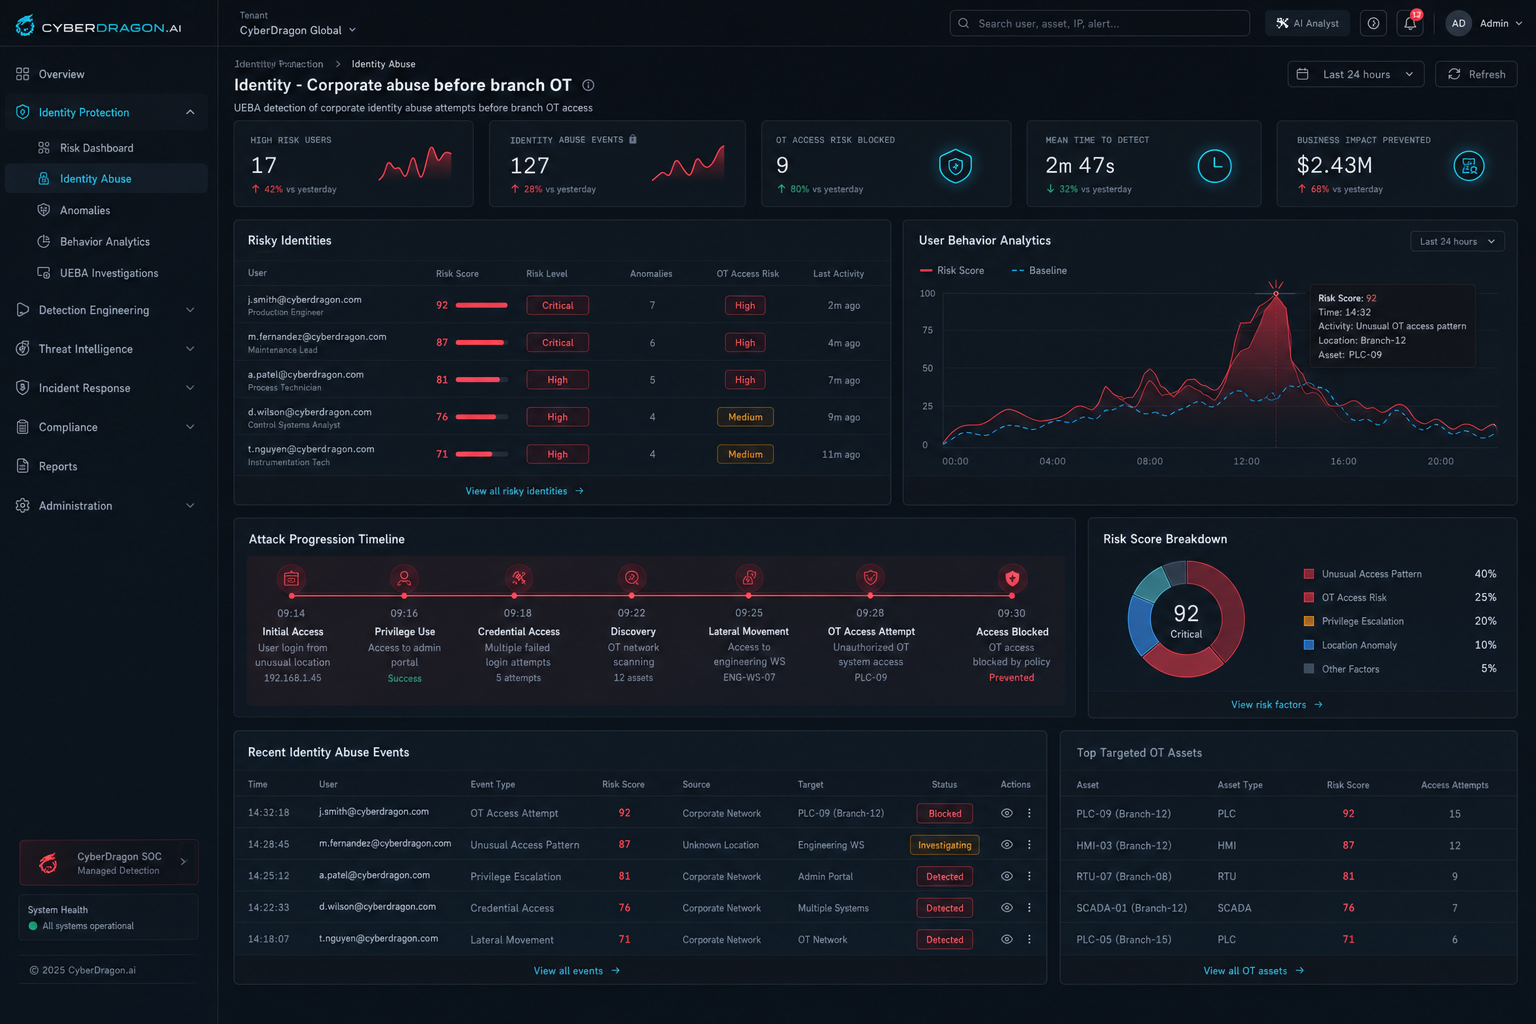
Corporate abuse before branch OT

  • Phishing and SaaS abuse correlated to facilities OT anomalies.
  • UEBA plus Edge closes the enterprise→branch corridor.
  • One indigenous SIEM/SOAR timeline for the CISO.
UEBA dashboard
Outcomes

What a PoV is designed to prove.

01

Branch OT correlated

02

Audit week saved

03

PQC identity live

Evidence

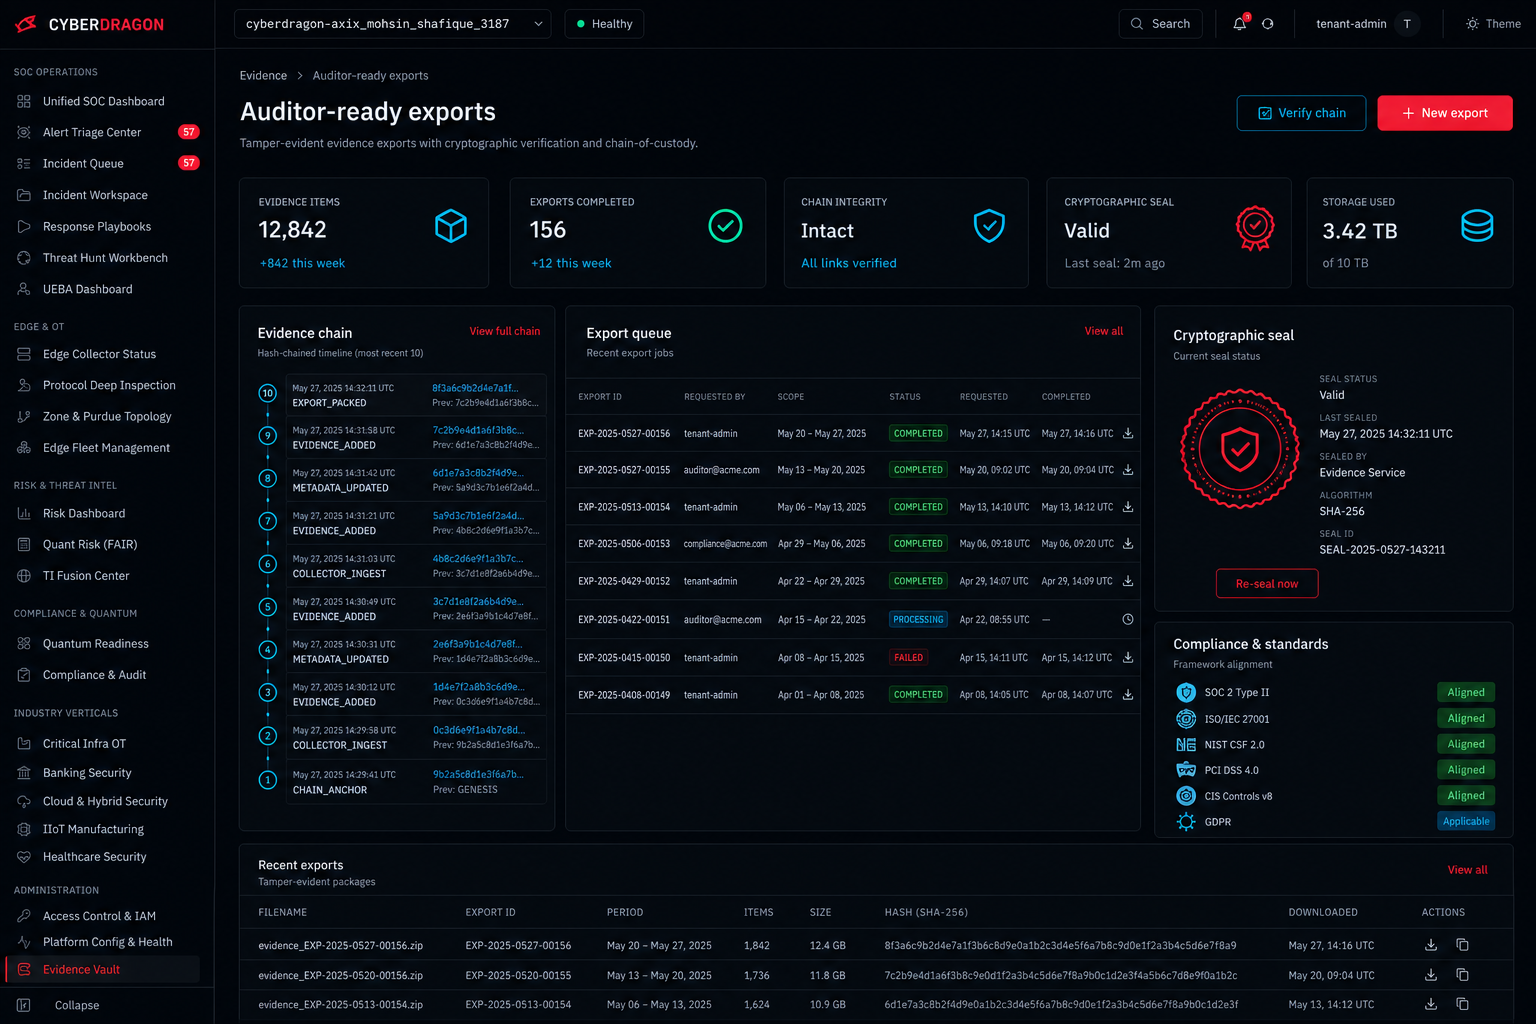
Auditor-ready exports

  • Hash-chained vault exports for PCI and SWIFT examinations.
  • Verify chain before the regulator arrives.
  • PoV metric: saved a week of manual log stitching.
Evidence Vault
Purdue L0–L5

Industry 4.0 and classic ICS on one zone model.

Edge deploys at L3 / industrial DMZ. Telemetry flows up. Command plane into L0–L2: none.

Explore Now
Explore Now
Explore Now
Explore Now
Explore Now
Explore Now

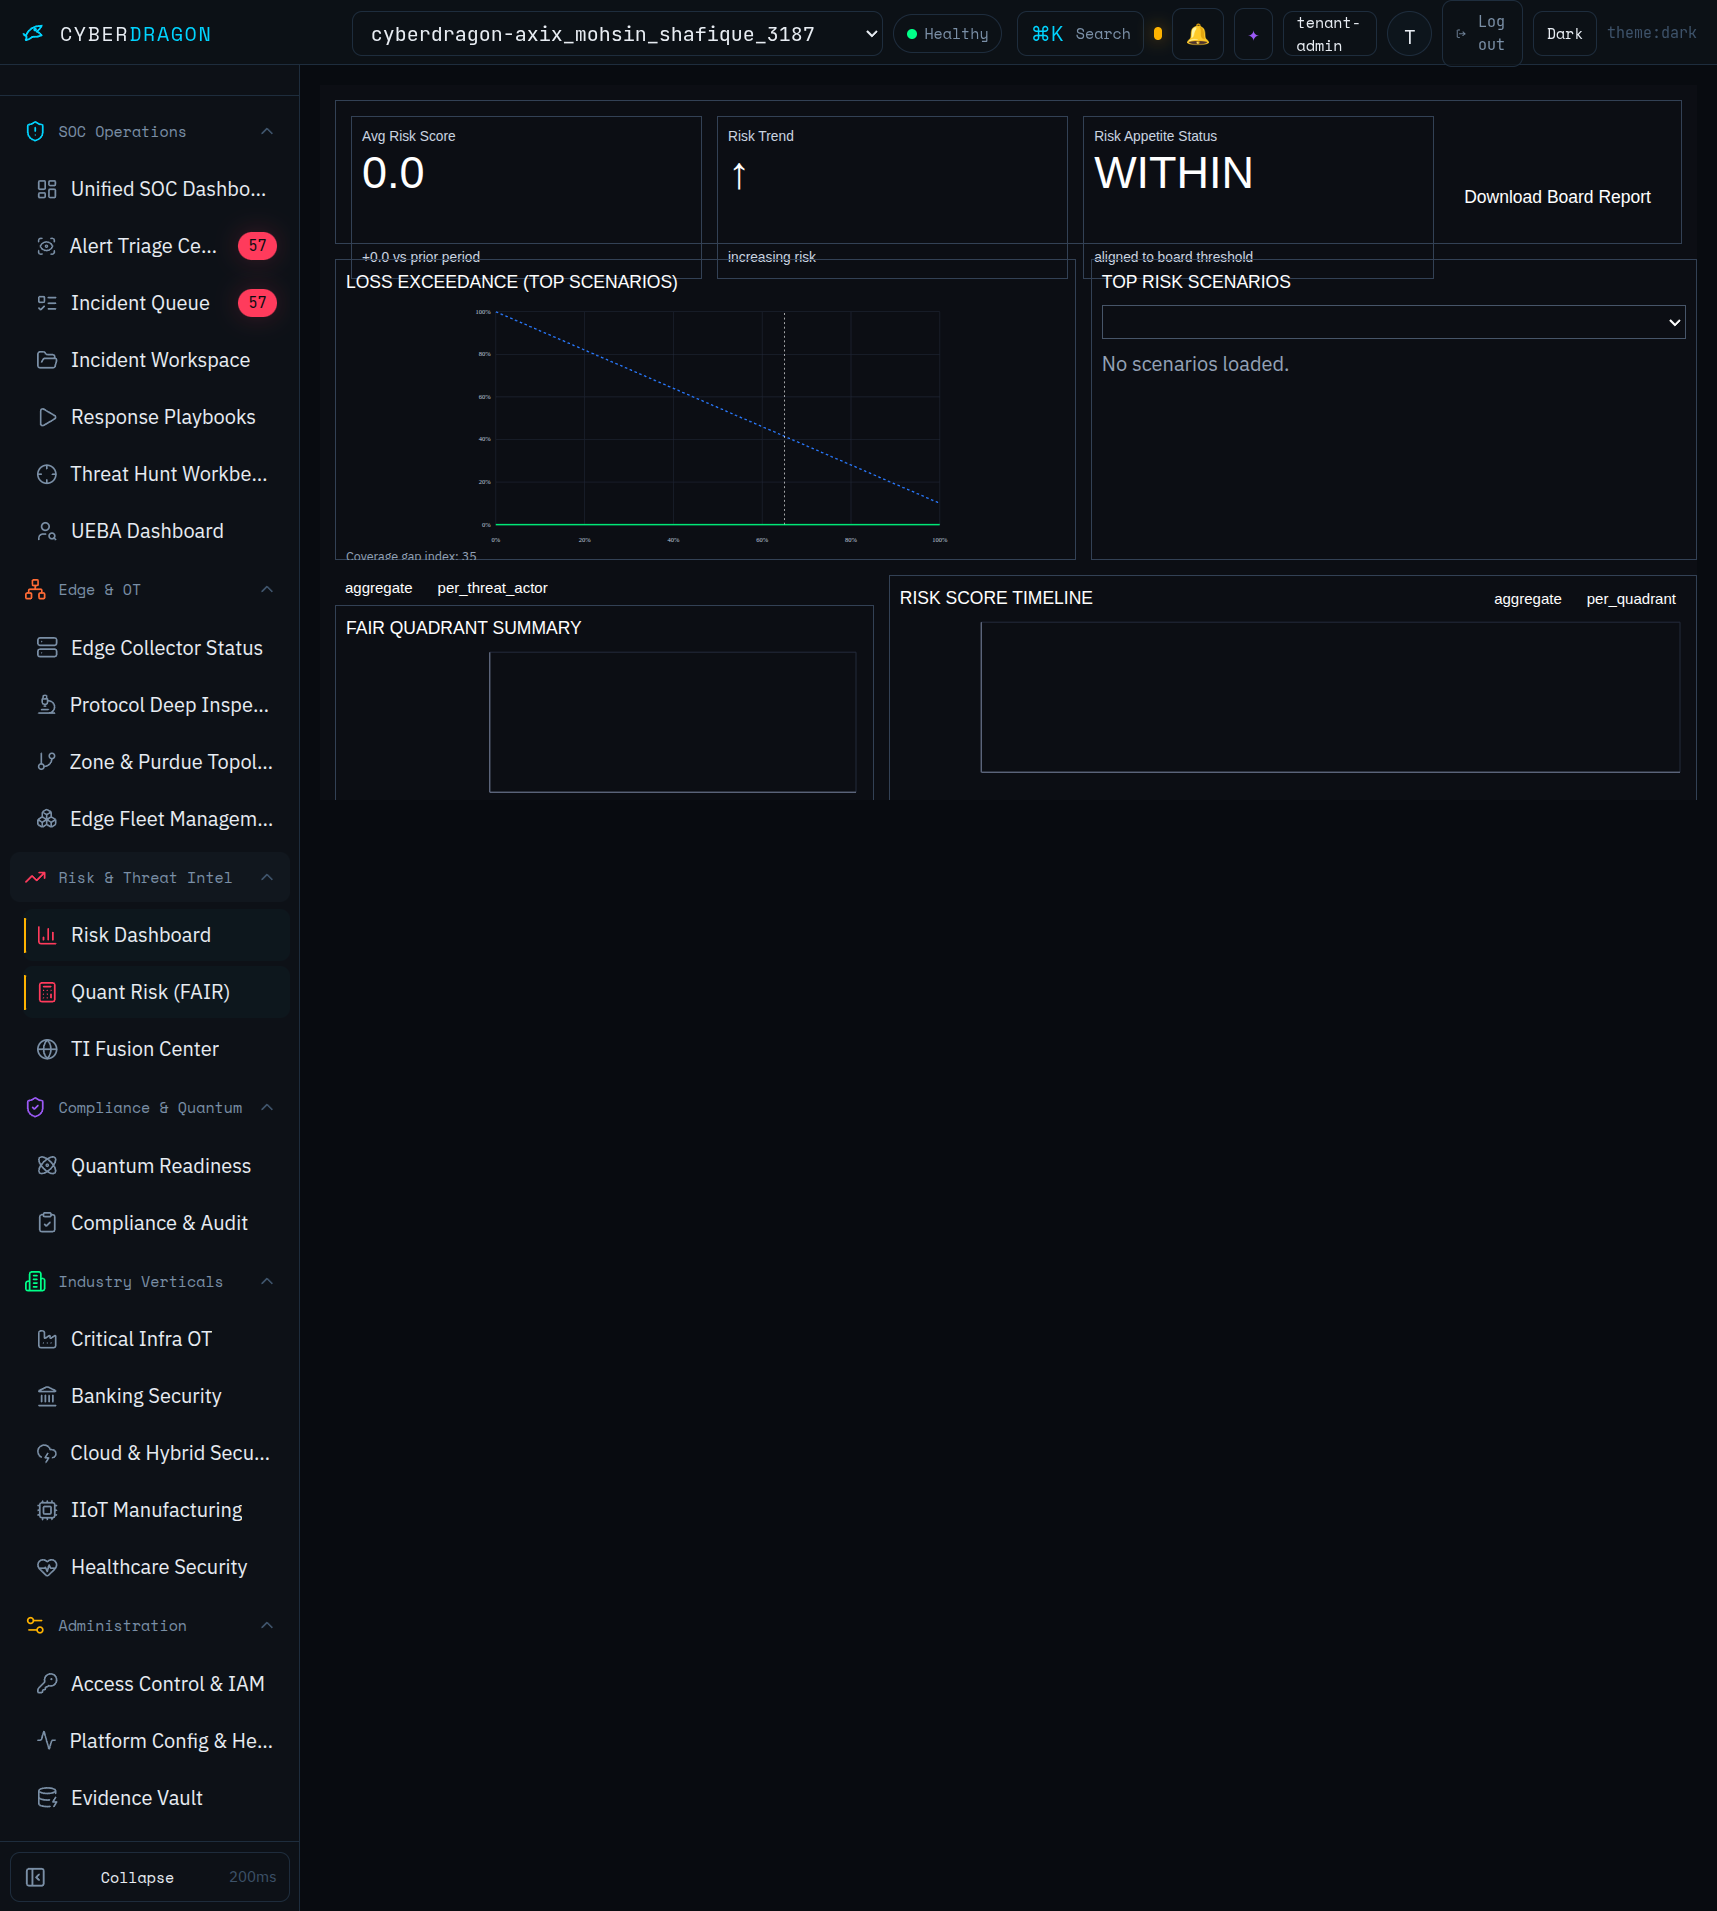
Risk

FAIR-style scenario scoring

  • Quantitative risk views for branch OT and hybrid cloud estates.
  • Same risk engine as energy and manufacturing verticals.
  • Dedicated single-tenant for national banks.
CyberDragon Quant Risk (FAIR) dashboard
FAQ

Frequently asked questions.

How does a Banking & Finance deployment start?
With a 7-day free trial on the cloud tenant, then a single Edge collector at the industrial DMZ for passive capture during the Proof of Value.
Which regulations are mapped?
PCI DSS, SWIFT CSP, ISO 27001. Controls are auto-mapped from live events and sealed into the evidence vault for auditors.
Do we need agents on operational devices?
No. Collection is passive from a SPAN tap or hardware TAP, so no agents are installed on PLCs, RTUs, or medical and field devices.
Is CyberDragon a SIEM replacement?
CyberDragon includes an indigenous SIEM/SOAR plane and also forwards to existing SIEMs via syslog, Splunk HEC, STIX/TAXII, and webhooks.

Request a Banking & Finance trial.

A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.