CyberDragon Core is live — indigenous SIEM/SOAR with Edge protocol capture. Start a 7-day free trial on your own traffic →
Security

Cyber defense in depth — from identity to evidence.

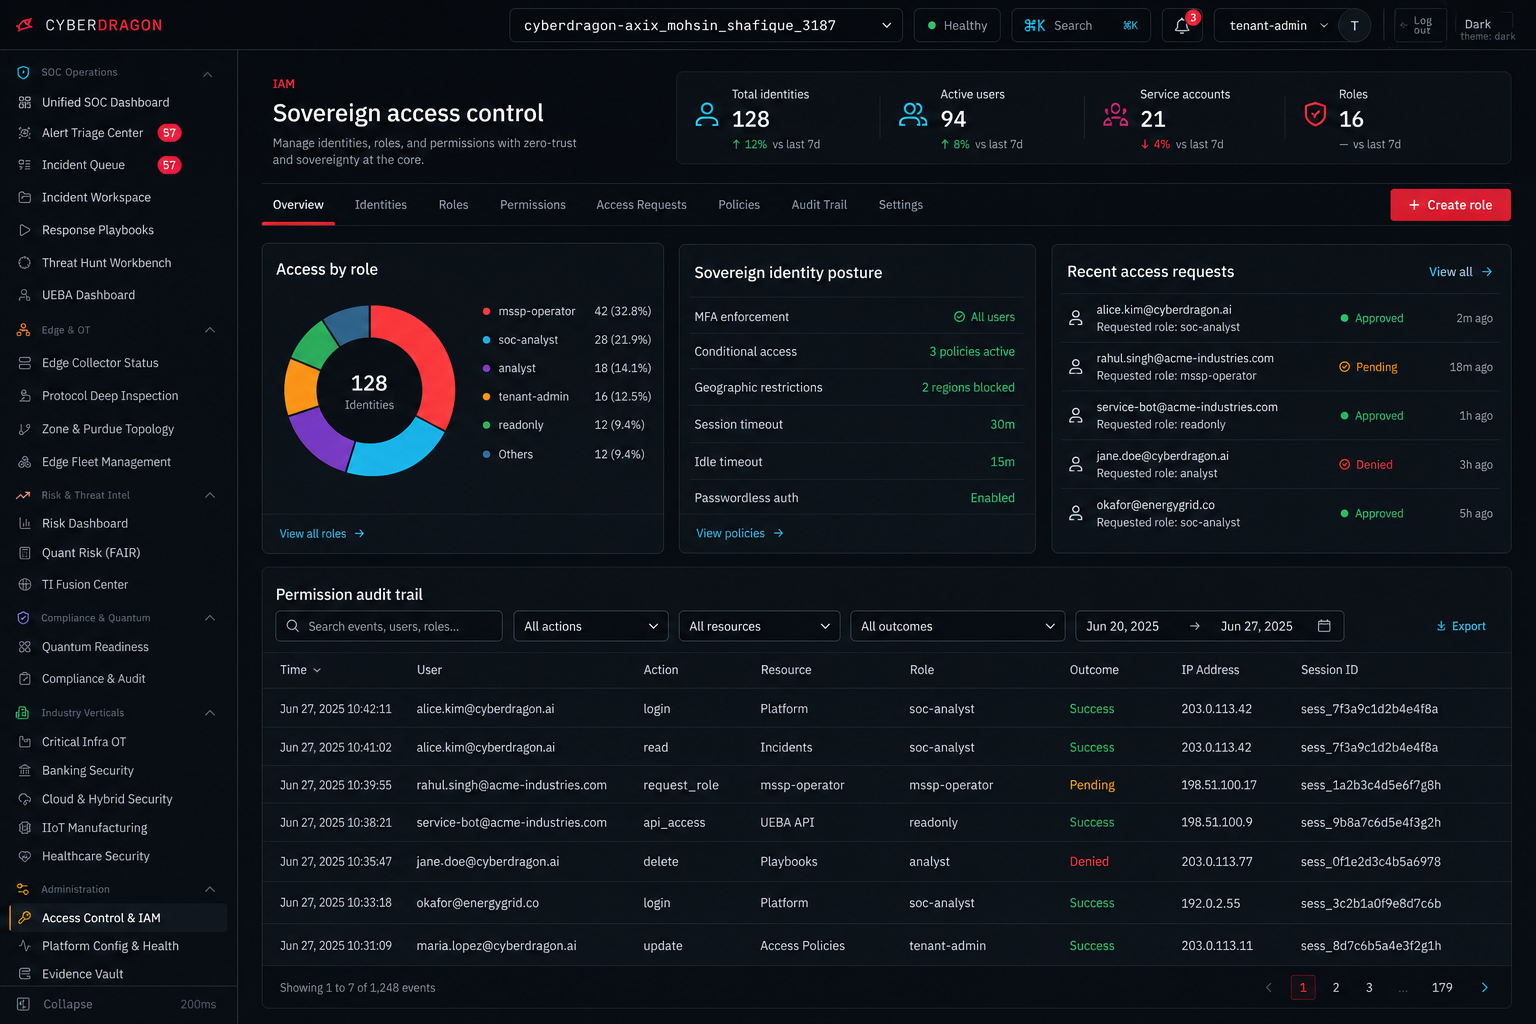
Hybrid PQC JWTs, Vault-backed keys, 7-tier RBAC, OPA OT guardrails, PostgreSQL RLS, and a tamper-evident evidence vault.

PQC identity

ML-DSA-65 + Ed25519 — live today, not 2030.

Every session JWT is hybrid-signed. Say quantum-resilient with hybrid signing today — not "fully quantum-safe end-to-end."

Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
OT safety

We automate up to the plant floor — not against it.

Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Evidence vault

Hash-chained. Ed25519-signed. Tamper-evident ZIP export.

Every finding is sealed into a hash-chained vault. Chain verify is lab-validated (66 entries, OK). Built for the auditor, the regulator, and the incident review board.

01Event
02Hash
03Ed25519 seal
04Vault
05ZIP export
Network segmentation

Four Docker networks. No flat trust.

Core splits frontend / backend / ingest / data networks. Telemetry from Edge is HMAC + optional mTLS. There is no command plane into Purdue L0–L2.

frontend

UIs, nginx ingress, TLS 1.3

backend

SOC services, Temporal, OPA

ingest

Edge / connector intake

data

PostgreSQL, Neo4j, Kafka, Vault

Frameworks

IEC 62443 · NERC CIP · NIST · ISO · SOC 2

IEC 62443-3-3

OT / ICS system security

NERC CIP

Bulk electric / utilities

NIST CSF 2.0

Enterprise cyber maturity

ISO 27001:2022

ISMS audit cycles

SOC 2 (TSC)

Service organization assurance

EU CRA

Bridge mapping (roadmap)

Engineering practices

How the platform itself is kept trustworthy.

Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Explore Now →
Identity federation

Bring your IdP without giving up sovereign sessions.

Explore Now →
Explore Now →
Explore Now →
Shared responsibility

Who owns what, written down before go-live.

AreaAxix Technologies LLC USACustomer
Edge placement and SPAN configurationGuidance, validation, and parser tuningPhysical port, host, and change approval
Platform patching (Mode A)Full ownershipMaintenance-window acknowledgement
Platform patching (Mode B)Signed releases and upgrade runbooksExecution inside your change process
Detection tuningBaseline content and hypercare tuningSite context and suppression sign-off
Response actions on OT assetsPolicy engine and audit trailHuman approval, always
Evidence retentionChain integrity and export toolingRetention policy and archive custody
FAQ

Frequently asked questions.

Is post-quantum cryptography live or roadmap?
Live. Every session JWT is hybrid-signed with ML-DSA-65 (NIST FIPS 204) and Ed25519. We say quantum-resilient with hybrid signing today, not fully quantum-safe end to end.
How is tenant isolation enforced?
Structurally, with PostgreSQL row-level security, plus OPA authorization and a 7-tier RBAC model.
Can the platform deny an action a human approved?
Yes. OPA policy evaluates OT-affecting classes independently and can deny after analyst approval, with the reason code sealed into the evidence vault.

Download the security brief after trial.

Start a 7-day free trial, then request the security whitepaper from the team.