Fusion
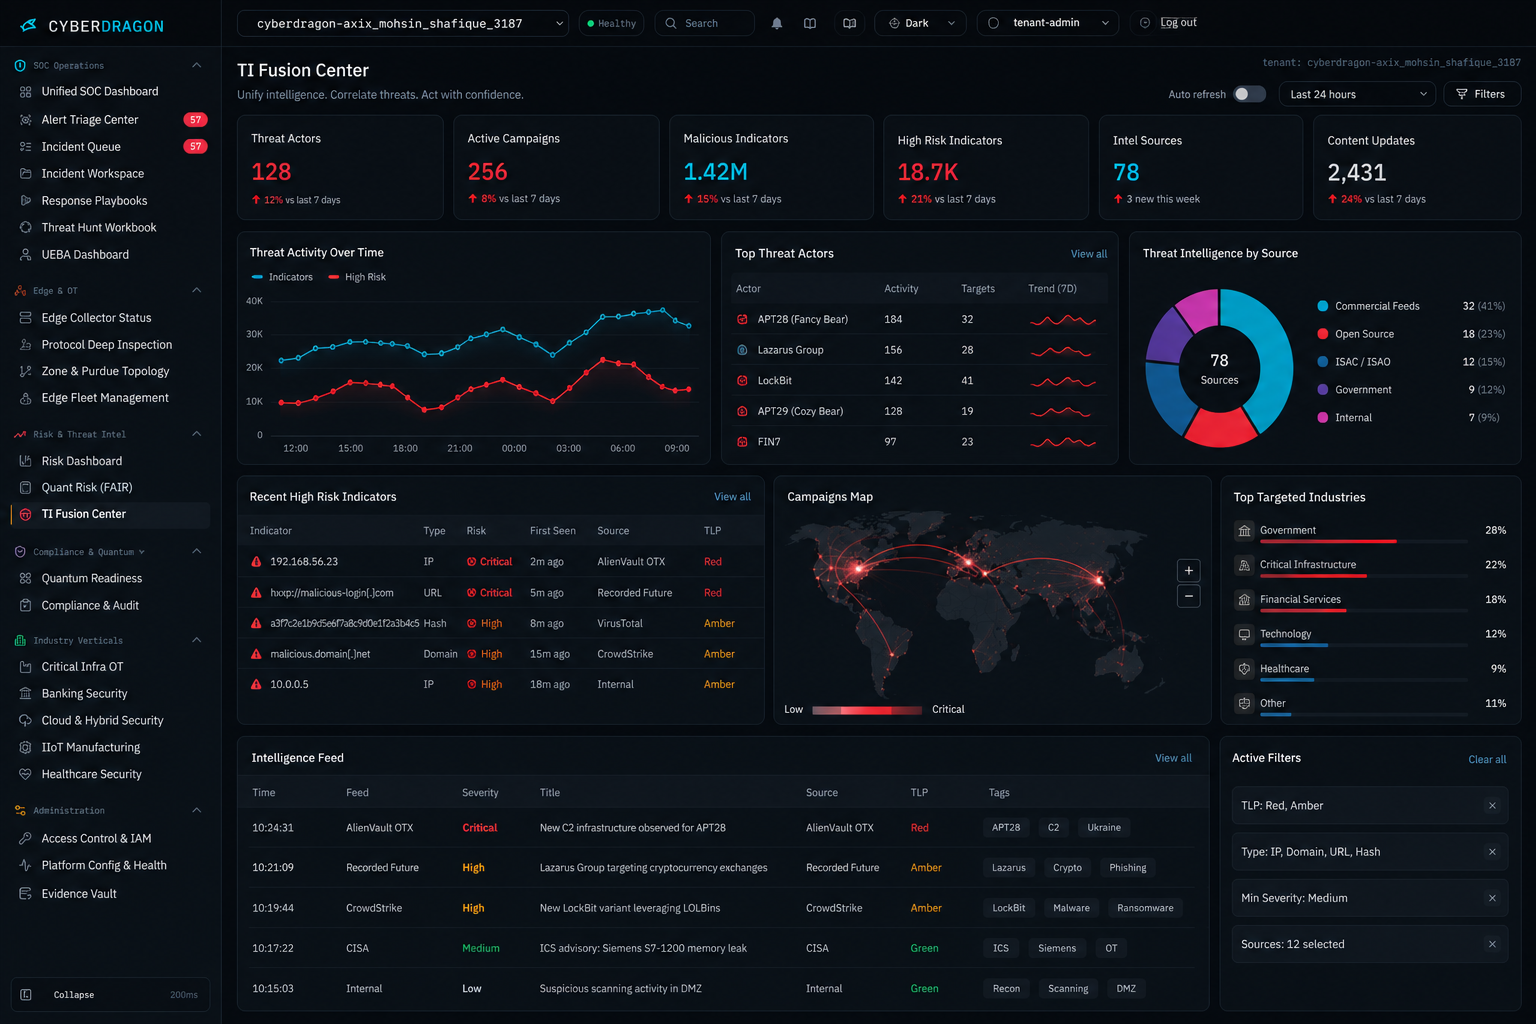
TI Fusion Center
- Public intel in-flight with Edge events.
- Threat Atlas is the public board; Fusion is the tenant board.
- No separate silo.
Quarterly threat reports, YAML detection packs with MITRE mapping, CVE coordination, and ICS-ISAC / E-ISAC / FS-ISAC alignment.
KEV, ransomware disclosures, and ICS advisories and the briefing video sits next to the live board, not a separate marketing silo.
Fusion
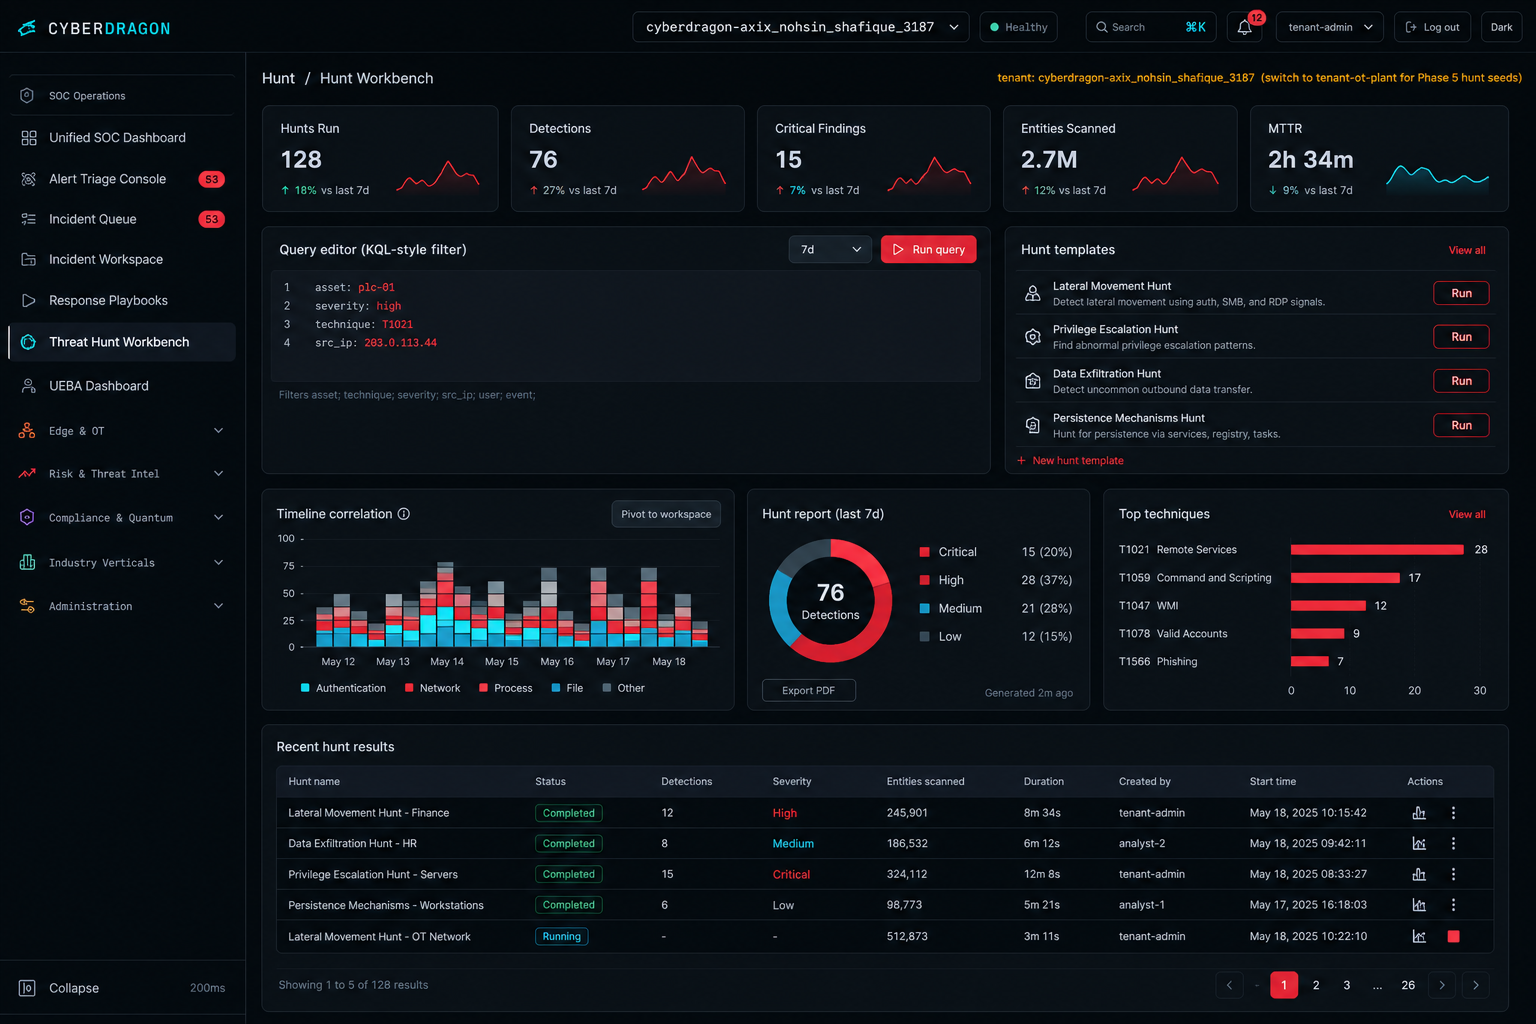
Hunt
UEBA

Burst correlation and brute force, scanning, and rapid recon across enterprise and OT sensors.
Lateral movement and engineering-workstation pivots that stitch enterprise identity abuse to OT sessions.
Slow APT dwell and staged persistence, C2 beaconing, and pre-positioning before an OT action.
| Tactic | enterprise expression | OT expression |
|---|---|---|
| Reconnaissance | Network and identity enumeration | Modbus function-code sweeps, device fingerprinting |
| Initial Access | Phishing, exposed remote services | Vendor VPN and engineering workstation entry |
| Lateral Movement | Credential reuse, remote services | Enterprise→OT pivot across the industrial DMZ |
| Collection | Data staging | OPC-UA tag harvesting, historian scraping |
| Impair Process Control | and | Unauthorized Modbus writes, DNP3 control commands |
| Impact | Ransomware deployment | Loss of view, loss of control, production downtime |
Exploited-in-the-wild vulnerabilities from the CISA Known Exploited Vulnerabilities catalog, tagged for OT and ICS relevance.
Ransomware leak-site disclosures with sector and country attribution, flagged when the victim profile implies industrial exposure.
CISA industrial control system advisories, cross-referenced against the protocols Edge parses natively.
A live corpus of 15,093 indicators fused from OTX, Abuse.ch, ThreatFox, MITRE TAXII, and GreyNoise, applied to events in flight.
Open the live board: Threat Atlas.
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.