CyberDragon Core is live — indigenous SIEM/SOAR with Edge protocol capture. Start a 7-day free trial on your own traffic →
Manufacturing & IIoT · Global cyber defense

Stop production tampering before downtime

Industry 4.0 and smart-factory cyber defense that treats Modbus writes and OPC-UA session changes as first-class SOC signals — not afterthoughts bolted onto an endpoint stack.

The challenge

What Manufacturing & IIoT operators face on the Enterprise→OT corridor.

Attackers do not respect the DMZ. Manufacturing & IIoT estates need quantum-resilient cyber defense that treats OT protocols, Industry 4.0 cells, and corporate identity as one kill chain — with evidence auditors can trust.

Unauthorized Modbus / DNP3 writes that alter setpoints or recipes before anyone notices

Smart-factory and IIoT device sprawl across L1–L3 with no agent path to PLCs

Unplanned downtime from production tampering that endpoint-only tools never correlate

ISO 27001 / NIST CSF audits that cannot prove OT control coverage

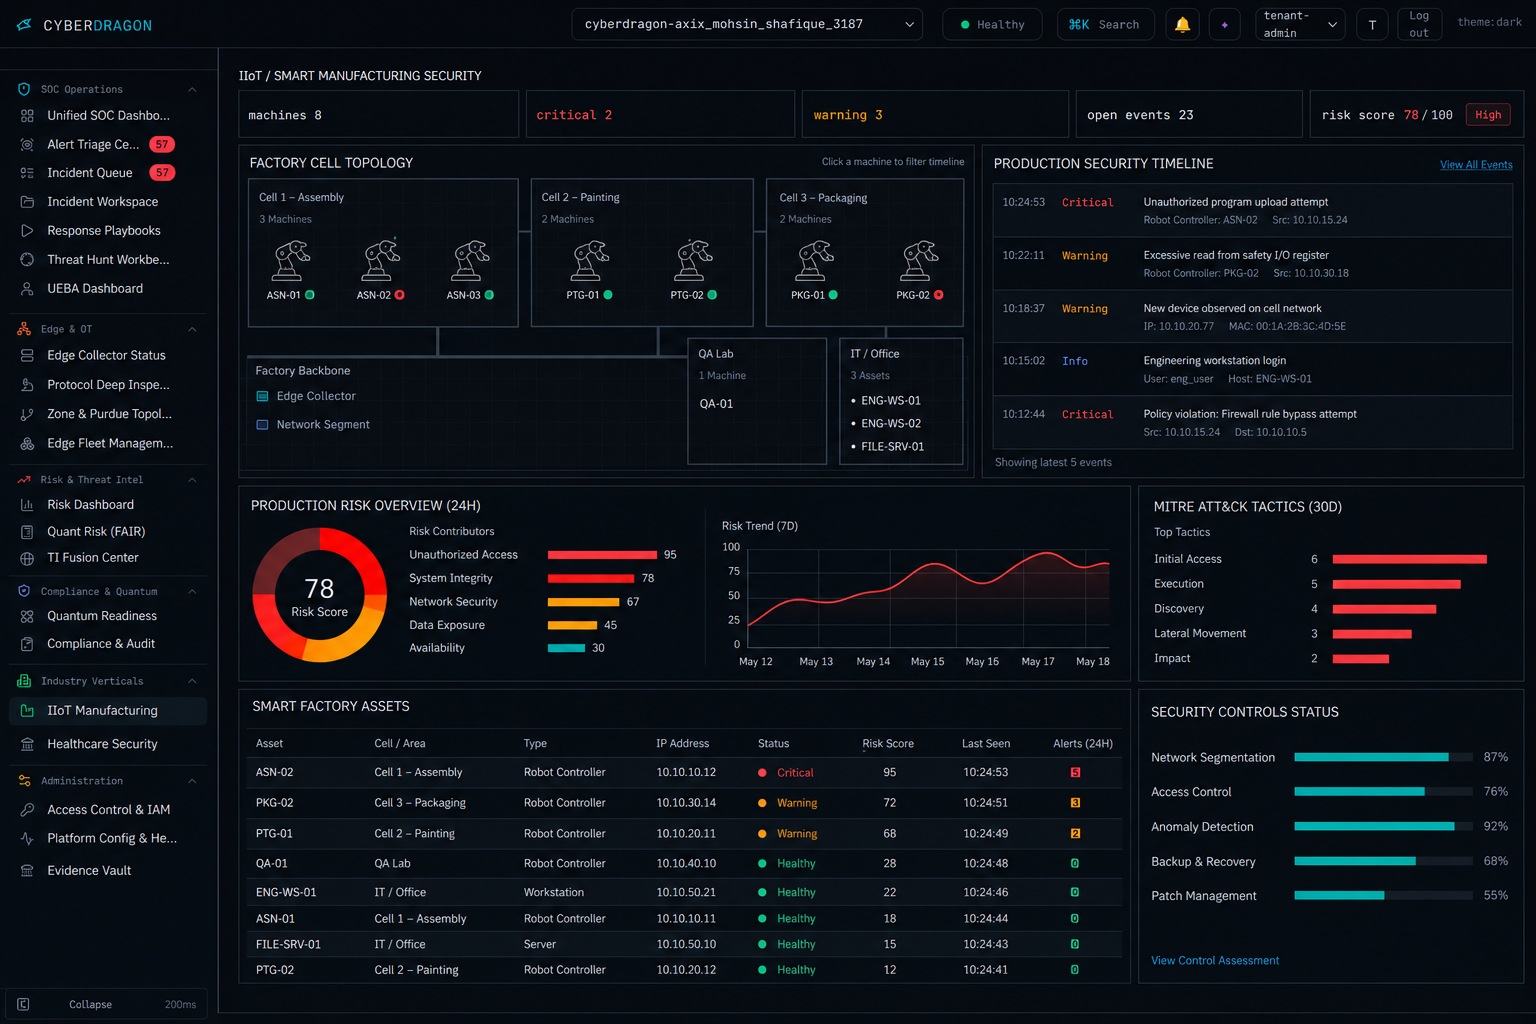
Smart factory

IIoT manufacturing security

  • Cells and conveyor zones on one OT board.
  • Security events scored against production risk.
  • No agents on robot controllers.
IIoT dashboard
How CyberDragon helps

Unified SIEM/SOAR, Edge capture, and zone-aware policy for Manufacturing & IIoT.

Native Modbus, DNP3, OPC-UA, MQTT parsing at the Edge — no agents on PLCs or robots

IIoT vertical + incident queue with Enterprise→OT kill-chain timelines

ISO 27001 / NIST CSF evidence packets from live events

OT Safety Gate: OPA can deny automation even after human approval

Unified cyber threat intelligence fusion into the same SIEM/SOAR plane as enterprise alerts

Regulatory alignment: ISO 27001, NIST CSF. Controls auto-map from live events into the tamper-evident evidence vault.

Protocols
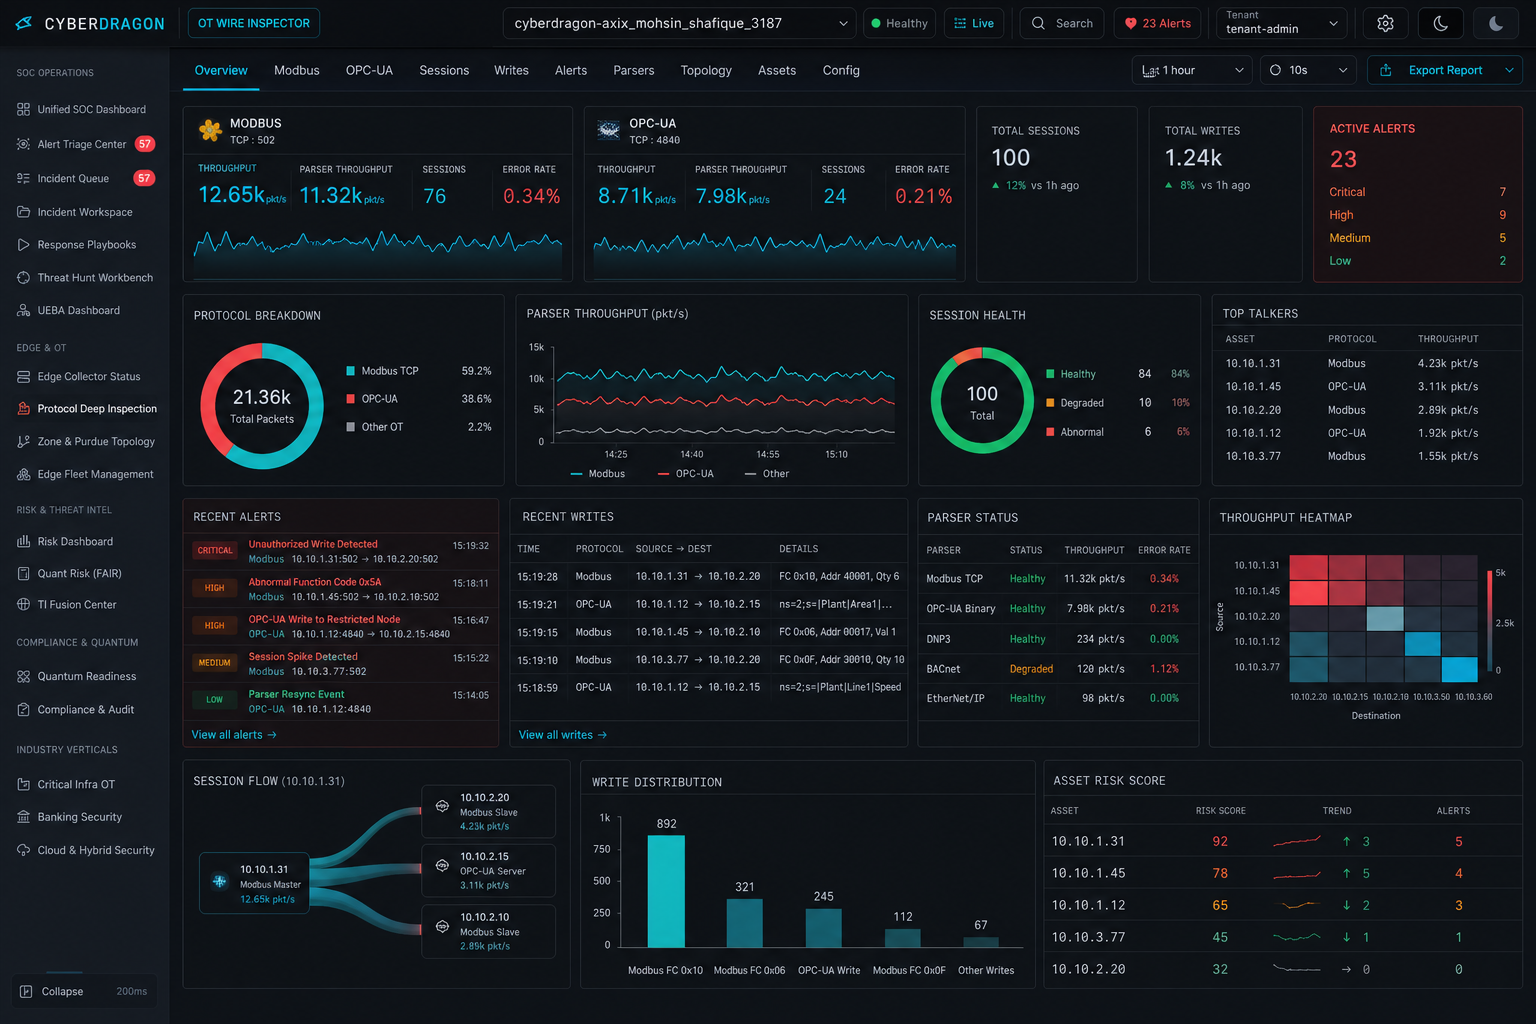
Modbus and OPC-UA on the wire

  • Writes and session changes as first-class SOC signals.
  • Industry 4.0 cells without endpoint coverage.
  • SPAN at the DMZ.
CyberDragon Protocol deep inspector
Outcomes

What a PoV is designed to prove.

01

Tampering visible on the wire

02

Downtime risk scored

03

Plant engineers can sign off on safety

Purdue L0–L5

Industry 4.0 and classic ICS on one zone model.

Edge deploys at L3 / industrial DMZ. Telemetry flows up. Command plane into L0–L2: none.

Explore Now
Explore Now
Explore Now
Explore Now
Explore Now
Explore Now
FAQ

Frequently asked questions.

How does a Manufacturing & IIoT deployment start?
With a 7-day free trial on the cloud tenant, then a single Edge collector at the industrial DMZ for passive capture during the Proof of Value.
Which regulations are mapped?
ISO 27001, NIST CSF. Controls are auto-mapped from live events and sealed into the evidence vault for auditors.
Do we need agents on operational devices?
No. Collection is passive from a SPAN tap or hardware TAP, so no agents are installed on PLCs, RTUs, or medical and field devices.
Is CyberDragon a SIEM replacement?
CyberDragon includes an indigenous SIEM/SOAR plane and also forwards to existing SIEMs via syslog, Splunk HEC, STIX/TAXII, and webhooks.

Request a Manufacturing & IIoT trial.

A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.