
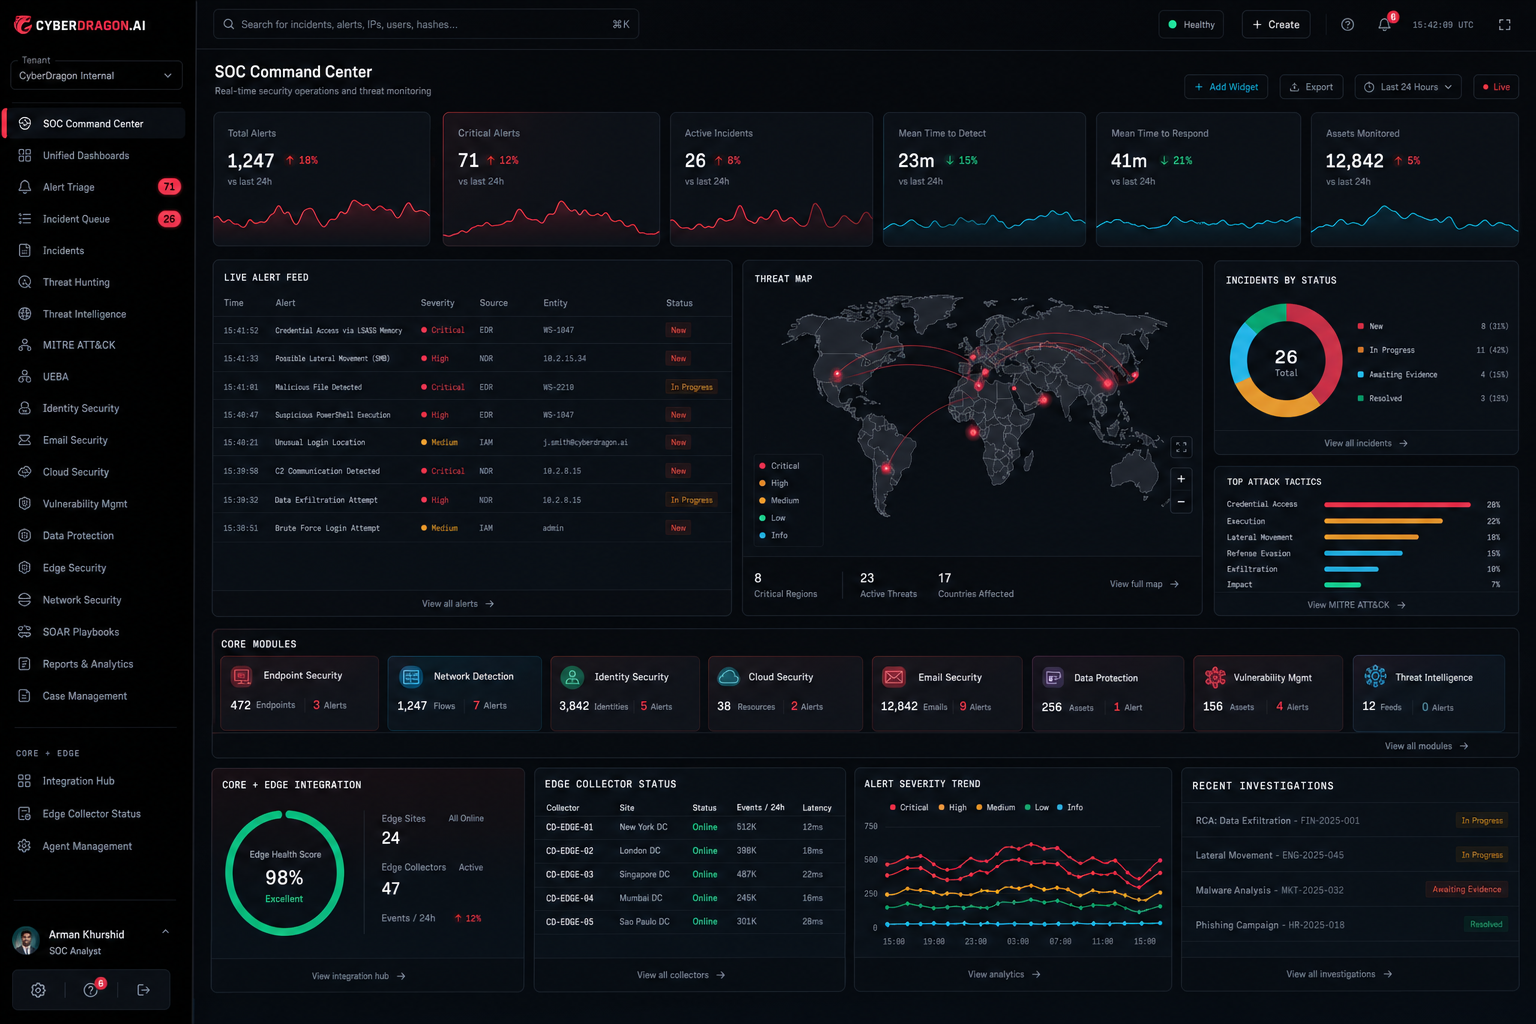
SOC
Where every Core module lands
- Live, partial, and roadmap labeled honestly on the platform page.
- Detection, risk, compliance, and identity share the same incident.
- Click a module, then come back to the operator board.
Network and OT events auto-map to roughly seven controls each. Framework packs for IEC 62443-3-3, NERC CIP, NIST CSF 2.0, ISO 27001:2022, and SOC 2 feed auditor packets from the evidence vault. FAIR-style scenario scores help CISOs prioritize without fake precision.
Automatic event→control mapping (~7 controls per network event)
IEC 62443-3-3, NERC CIP, NIST CSF 2.0, ISO 27001:2022, SOC 2 packs
Per-asset risk scoring on a 0–100 scale
FAIR-style scenario models for board narrative
Evidence vault export with control mappings
Honest PARTIAL maturity labels while dashboards harden
SOC
Edge and connector events enter the normalized stream with zone and asset context.
Compliance auto-mapper attaches relevant controls to each qualifying event.
Risk engine computes asset and scenario scores for prioritization.
Framework packs filter views and exports for the auditor's chosen standard.
Executive reporting generates CISO and board summaries from live evidence.
Signed ZIP packets include mappings, scores, and chain verification.
Playbooks
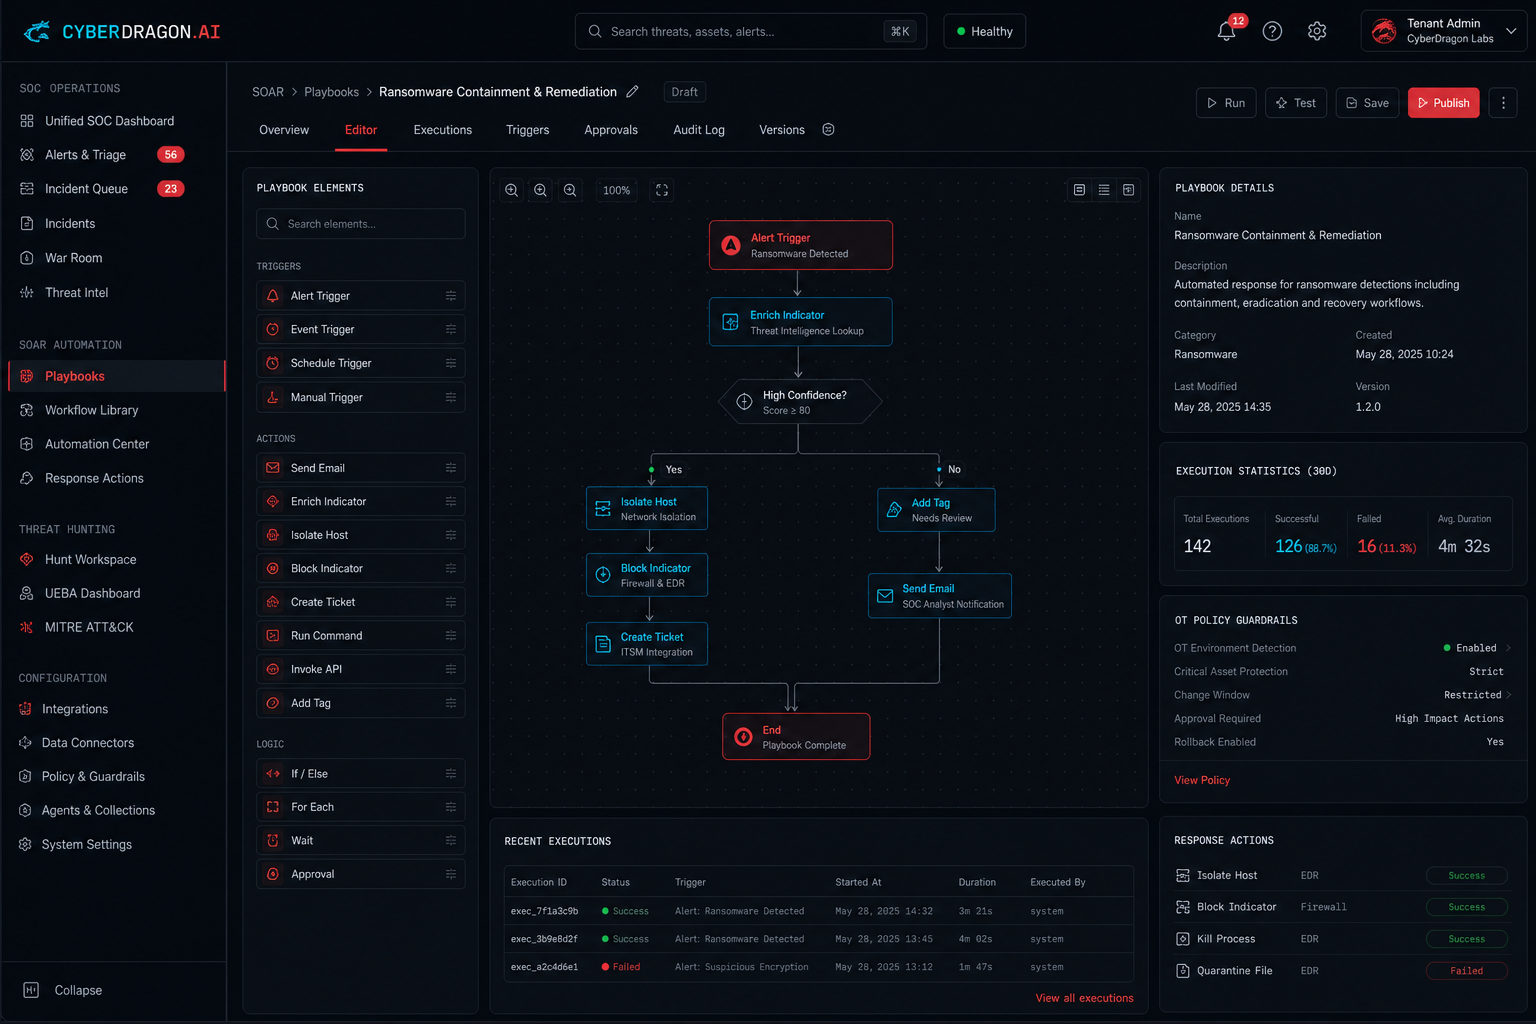
Modbus writes and DNP3 commands carry zone and asset identifiers.
MFA, RBAC, and session issuance map to access controls.
Approvals and OPA denials prove operational control effectiveness.
Tamper-evident records back every mapped control claim.
UEBA
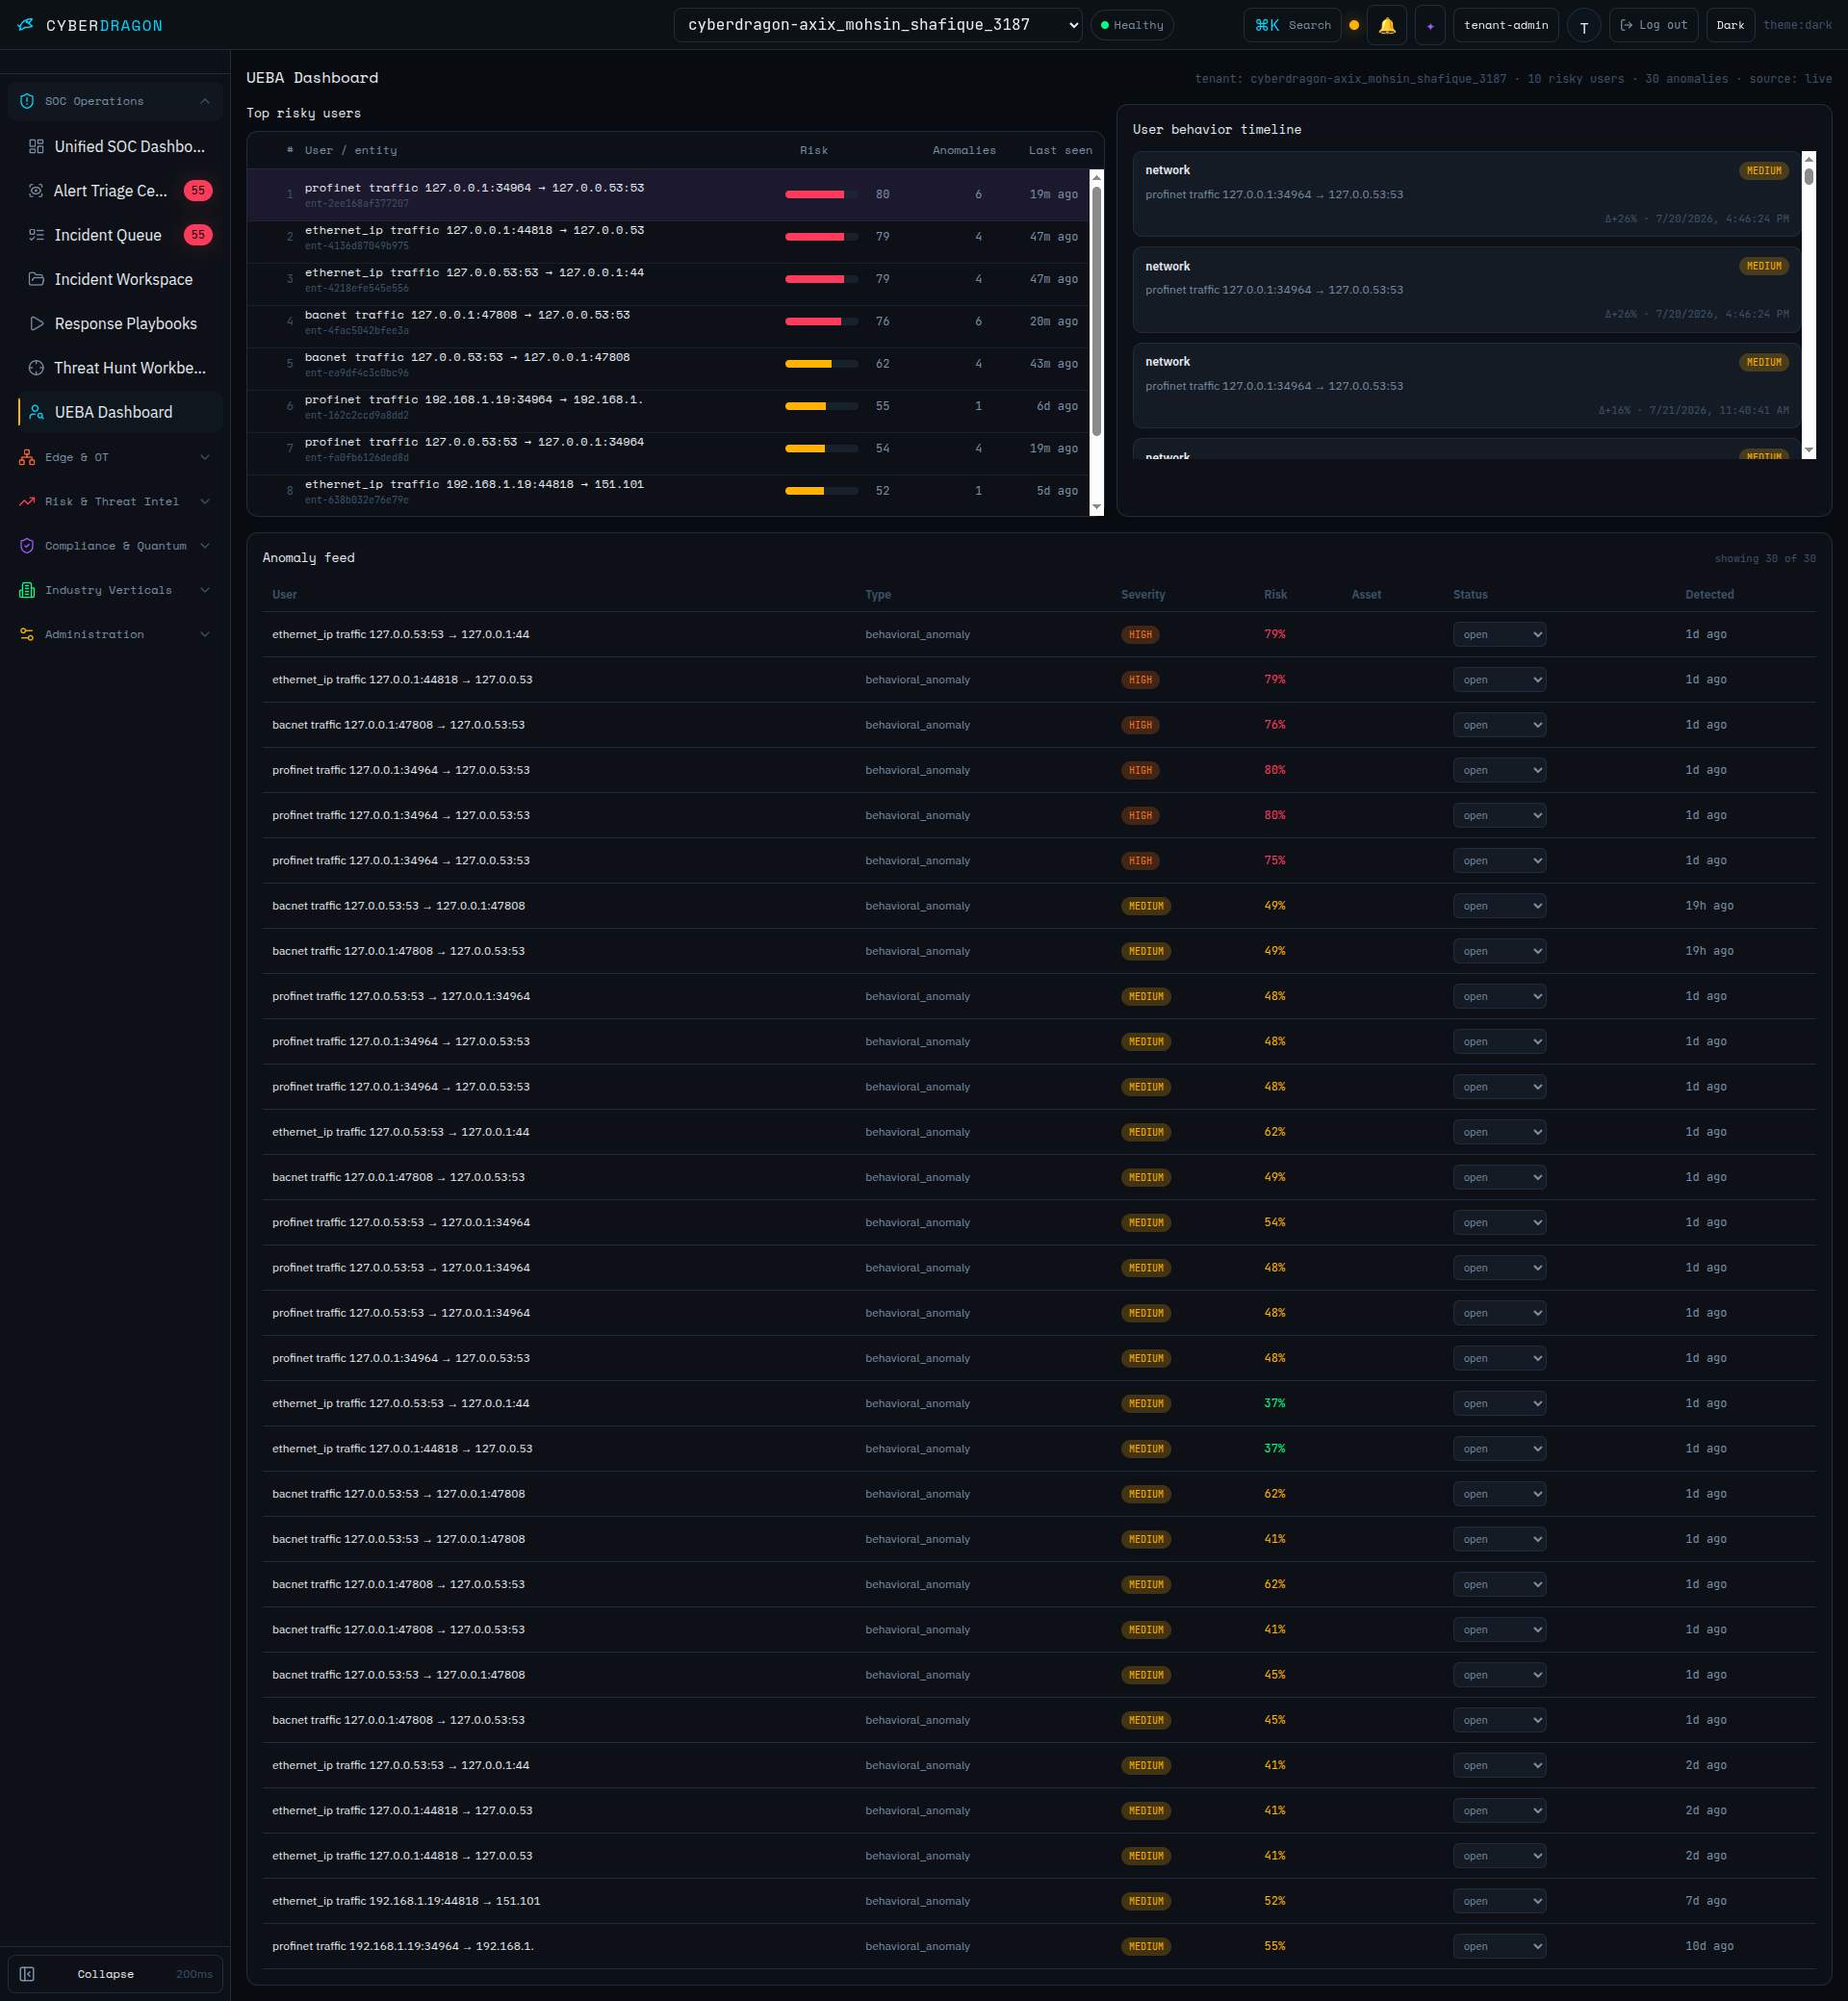
One platform, two planes — Core control plane and Edge collector for converged IT/OT.
Kafka-backed indigenous SIEM/SOAR — ingest, detection, risk, compliance, and response.
Passive SPAN capture at the industrial DMZ — telemetry up only, no PLC agents.
Modbus, DNP3, OPC-UA, and MQTT parsed natively at Purdue L3.
Indigenous global SIEM and Temporal-orchestrated SOAR with human approval gates.
W15 / W60 / W24 cascading windows across MITRE ATT&CK and ICS tactics.
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.