SOC
What endpoint-first consoles cannot see
- Unified SOC includes OT protocol events, not just endpoint detections.
- Kill-chain confidence across enterprise→OT pivots.
- Run both: endpoints for corporate, CyberDragon for the plant corridor.
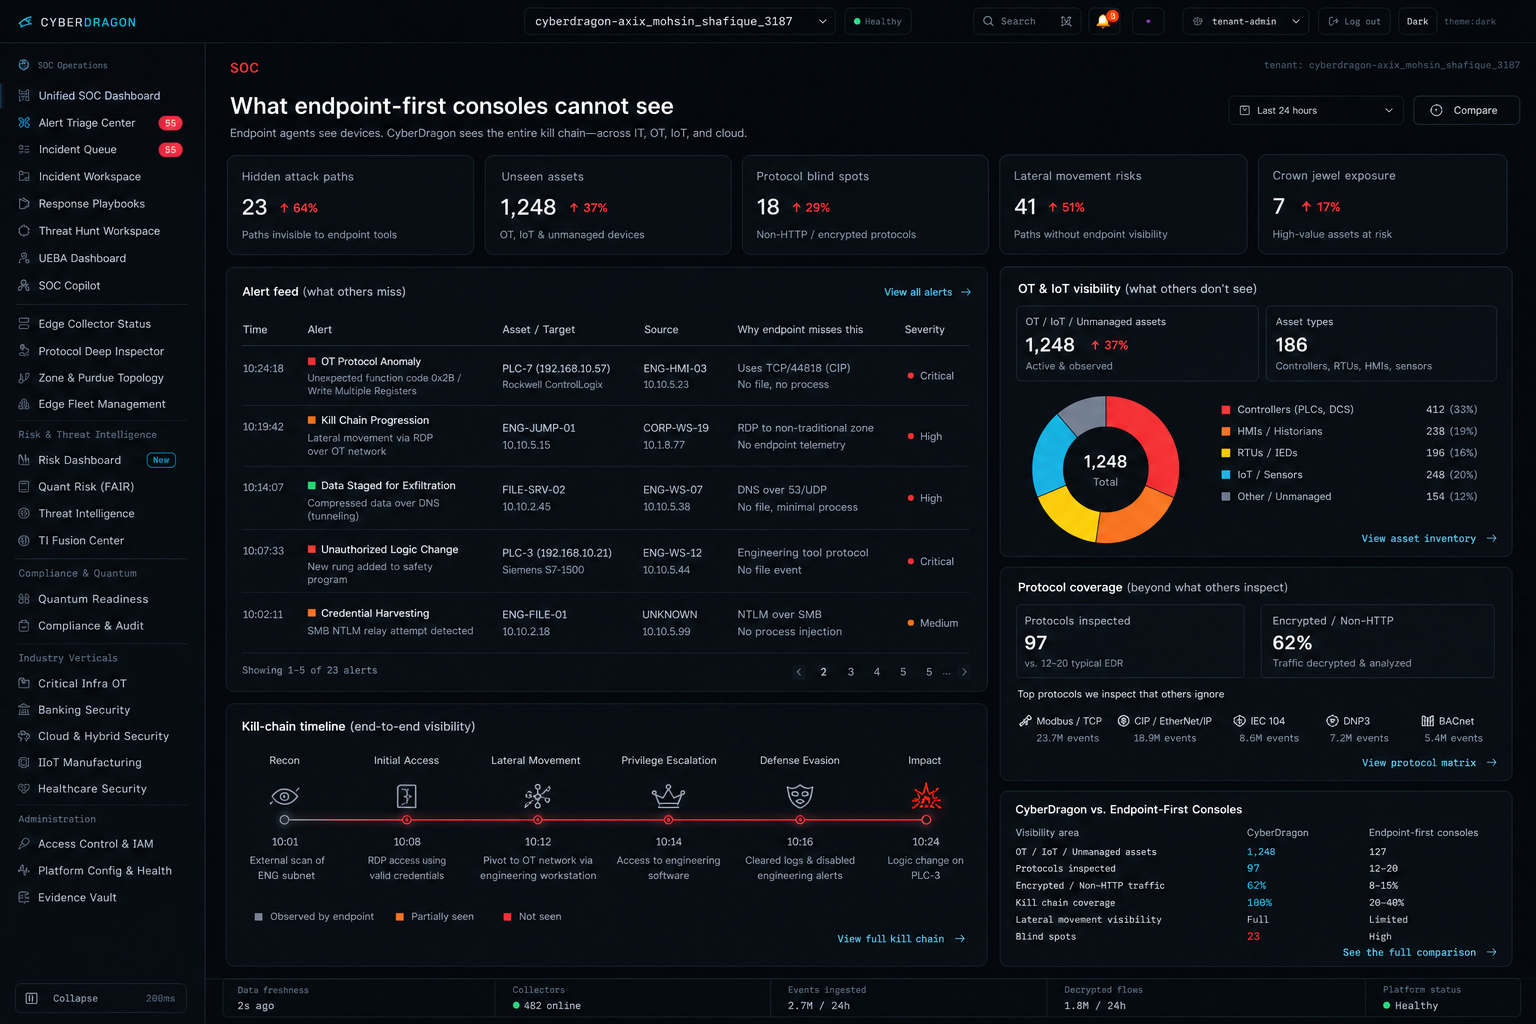
CrowdStrike excels at endpoint/XDR. Tanium excels at endpoint inventory and patch. TXOne excels at inline OT endpoint and network prevention. None of the three run a passive, no-footprint indigenous SIEM/SOAR with kill-chain correlation and evidence-grade audit and that gap is where CyberDragon runs.
Already running an endpoint, inventory, or prevention-first OT platform? CyberDragon adds the OT protocol layer and kill-chain correlation those stacks cannot see and and correlates enterprise compromise to industrial protocol abuse in one timeline. Fair comparison on this page; trademarks belong to their owners.
SOC
| Capability | CyberDragon | CrowdStrike Falcon | Tanium | TXOne Networks |
|---|---|---|---|---|
| Primary focus | Unified Enterprise/OT/IoT/IIoT kill-chain cyber defense | Endpoint detection & response (EDR/XDR) | Endpoint visibility, inventory, patch/config | Prevention-first OT endpoint & network protection |
| OT protocol depth | Native Modbus, DNP3, OPC-UA, MQTT parsing | Limited OT offerings; agent-centric | Not OT-protocol-native | Strong OT asset/protocol visibility; enforcement-centric |
| Collection model | Passive SPAN tap at plant DMZ and no agents on PLCs | Endpoint agents + cloud telemetry | Endpoint agents required | Inline network appliances + endpoint agents on engineering workstations/HMIs and active prevention, not passive-only |
| Plant safety | No command plane into L0–L2; dual-gate OT response | Automated remediation on endpoints | Config/patch orchestration | Inline inspection and endpoint lockdown and not a zero-footprint, passive-only model |
| Kill-chain correlation | W15 / W60 / W24 cascading windows; MITRE ATT&CK + ICS | Strong EDR correlation; OT is add-on | Limited SOC / kill-chain | OT asset and threat detection; not a SIEM/SOAR kill-chain plane |
| Post-quantum identity | Hybrid ML-DSA-65 + Ed25519 JWTs and live today | Standard enterprise crypto | Standard enterprise crypto | Standard enterprise crypto |
| Evidence for auditors | Hash-chained vault, Ed25519-signed, ZIP export | Falcon logging / reporting | Compliance data; less forensic chain | Asset and security posture reporting; not a hash-chained evidence vault |
| MSSP multi-tenancy | PostgreSQL RLS and structural isolation | Falcon Complete MSSP program | Partner programs | Partner/channel program; not structural RLS multi-tenancy |
| Air-gap / sovereign | Full on-prem Core + Edge; Helm air-gap mode | Cloud-first SaaS | On-prem / hybrid | On-prem appliances supported |
| Compliance mapping | Auto-mapper: IEC 62443, NERC CIP, NIST, ISO, SOC 2 | Framework mappings | Asset / compliance posture | OT/ICS framework alignment via asset inventory |
| Deployment at OT boundary | Edge at IEC 62443 L3 / industrial DMZ | Endpoint on L3+ workstations | Endpoint agents | Inline appliances plus agents on engineering workstations/HMIs |
| Offline resilience | SQLite WAL buffer, store-and-forward | Agent buffering | Agent-dependent | Appliance-dependent local enforcement |
| Pricing model | Platform + per Edge node | Per endpoint / module | Per endpoint | Per appliance / per protected asset |
Edge

Already running CrowdStrike, Tanium, or TXOne? CyberDragon adds the indigenous SIEM/SOAR and kill-chain layer those stacks don't run and and correlates enterprise compromise to industrial protocol abuse in one timeline. Integrates via syslog, Splunk HEC, STIX/TAXII, and webhooks.
Risk
Ask them of us too. If a vendor cannot answer these against your own traffic in a two-week evaluation, the answer is probably no.
A dedicated CyberDragon tenant on your own traffic and not a slide deck. See kill-chain cyber defense on your network.