CyberDragon Core is live — indigenous SIEM/SOAR with Edge protocol capture. Start a 7-day free trial on your own traffic →
MSSP · Global cyber defense

Multi-tenant OT/enterprise cyber defense at scale

Structural multi-tenancy for managed providers who need OT protocol depth, kill-chain SIEM/SOAR, and client SLAs — without stacking five tools per industrial account.

The challenge

What MSSP operators face on the Enterprise→OT corridor.

Attackers do not respect the DMZ. MSSP estates need quantum-resilient cyber defense that treats OT protocols, Industry 4.0 cells, and corporate identity as one kill chain — with evidence auditors can trust.

Margin pressure from tool sprawl across endpoint, SIEM, and OT vendors

Client SLA enforcement without a shared evidence and portfolio view

Multi-tenant onboarding that still needs weeks of custom glue

Industrial clients who refuse agents on PLCs

Portfolio

Unified SOC per client tenant

  • PostgreSQL RLS isolation — Client A evidence never lands in Client B.
  • Analysts work inside the tenant; operators see the portfolio.
  • Indigenous SIEM/SOAR so you are not stacking five tools per account.
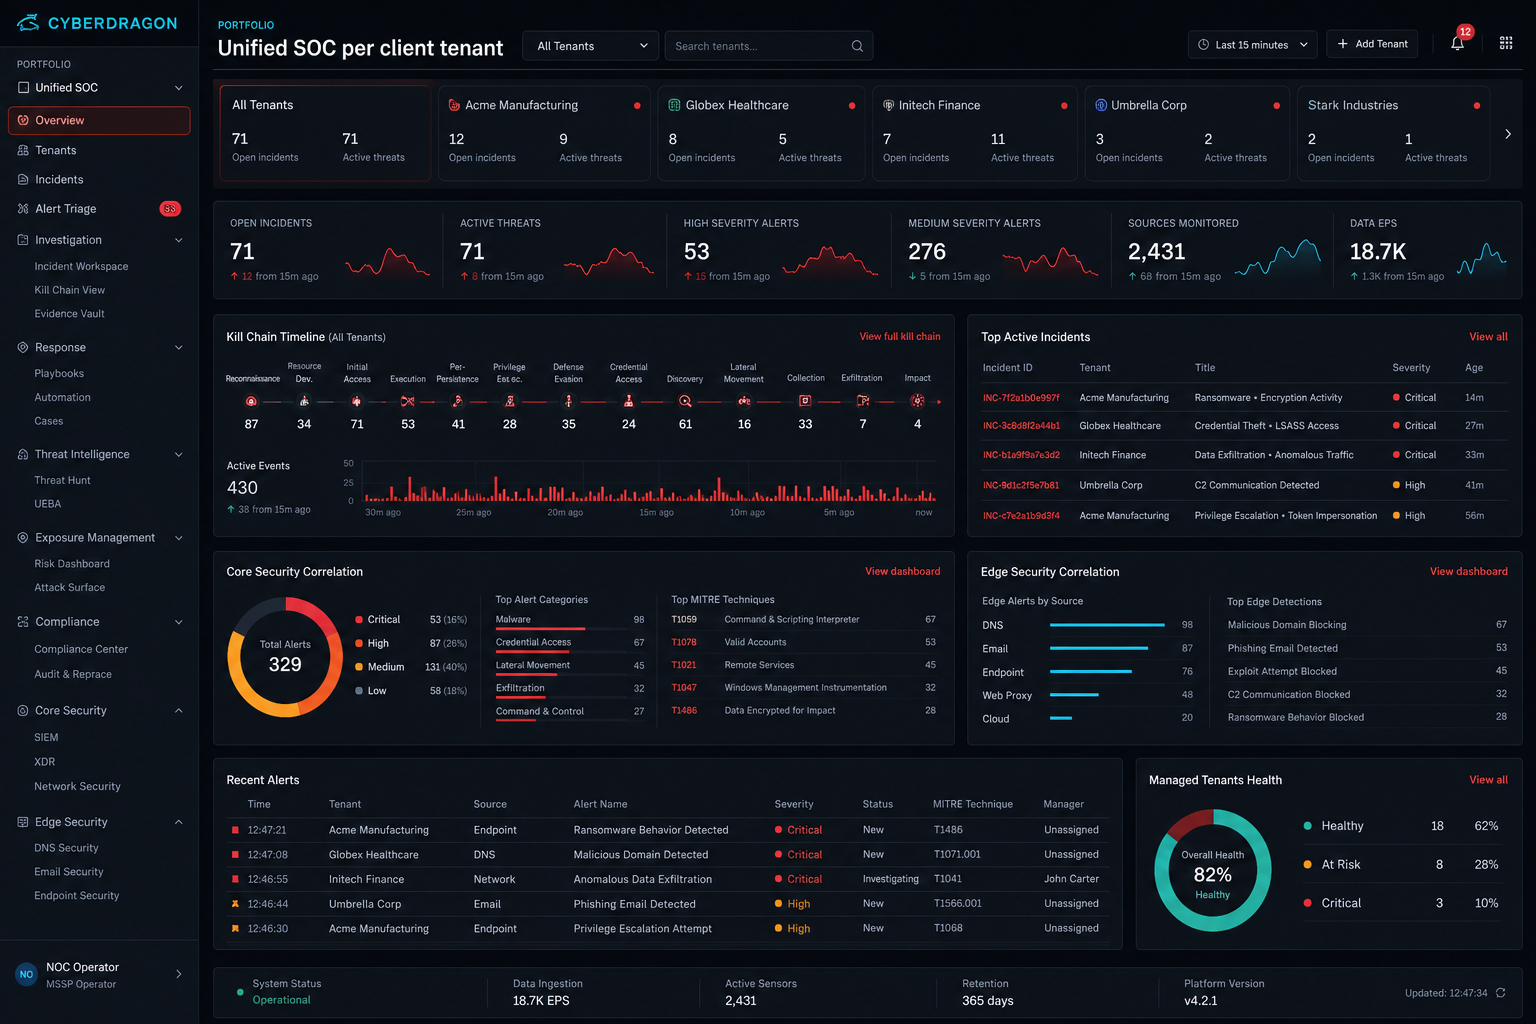
CyberDragon Unified SOC dashboard
How CyberDragon helps

Unified SIEM/SOAR, Edge capture, and zone-aware policy for MSSP.

PostgreSQL RLS structural isolation across managed tenants

Cross-tenant portfolio, bulk reports, and MSSP portal workflows

White-label / BYOC options under Axix licensing

One Edge kit per site + shared Core for indigenous SIEM/SOAR operations

Proof of Value packs that prove OT visibility before the contract expands

Regulatory alignment: Client contract SLAs. Controls auto-map from live events into the tamper-evident evidence vault.

IAM
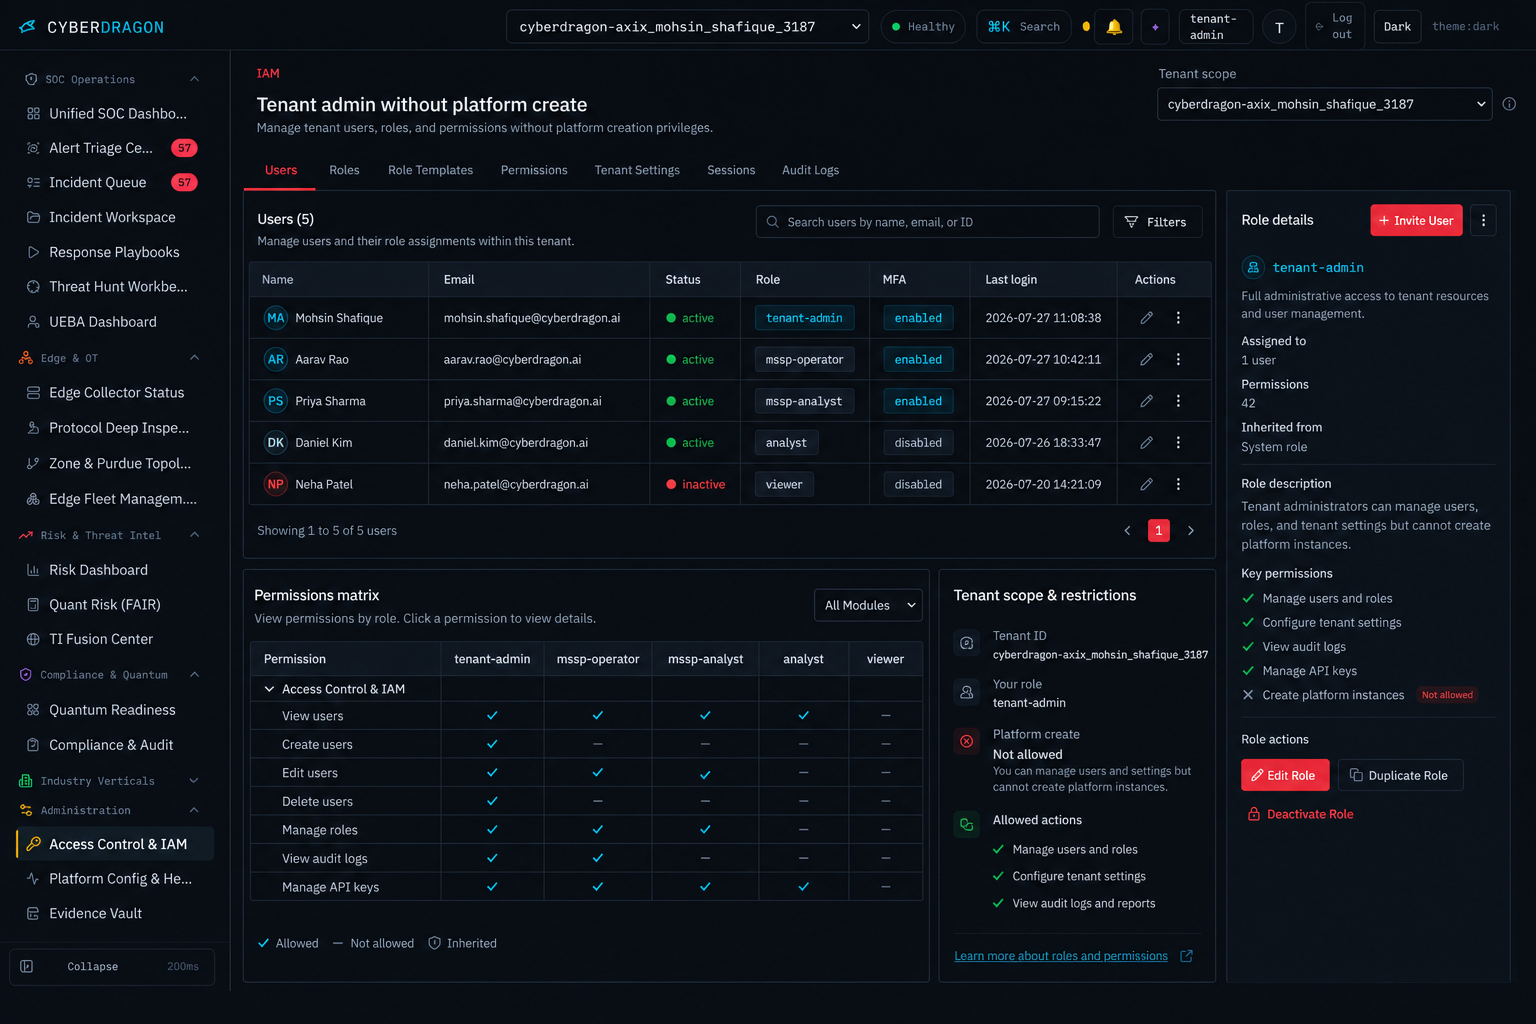
Tenant admin without platform create

  • Create analysts and read-only auditors per client.
  • MFA enrollment is in-product.
  • Super Admin still owns tenant create/suspend.
CyberDragon Access Control and IAM dashboard
Outcomes

What a PoV is designed to prove.

01

Faster onboarding

02

OT without PLC agents

03

Portfolio-level SLAs

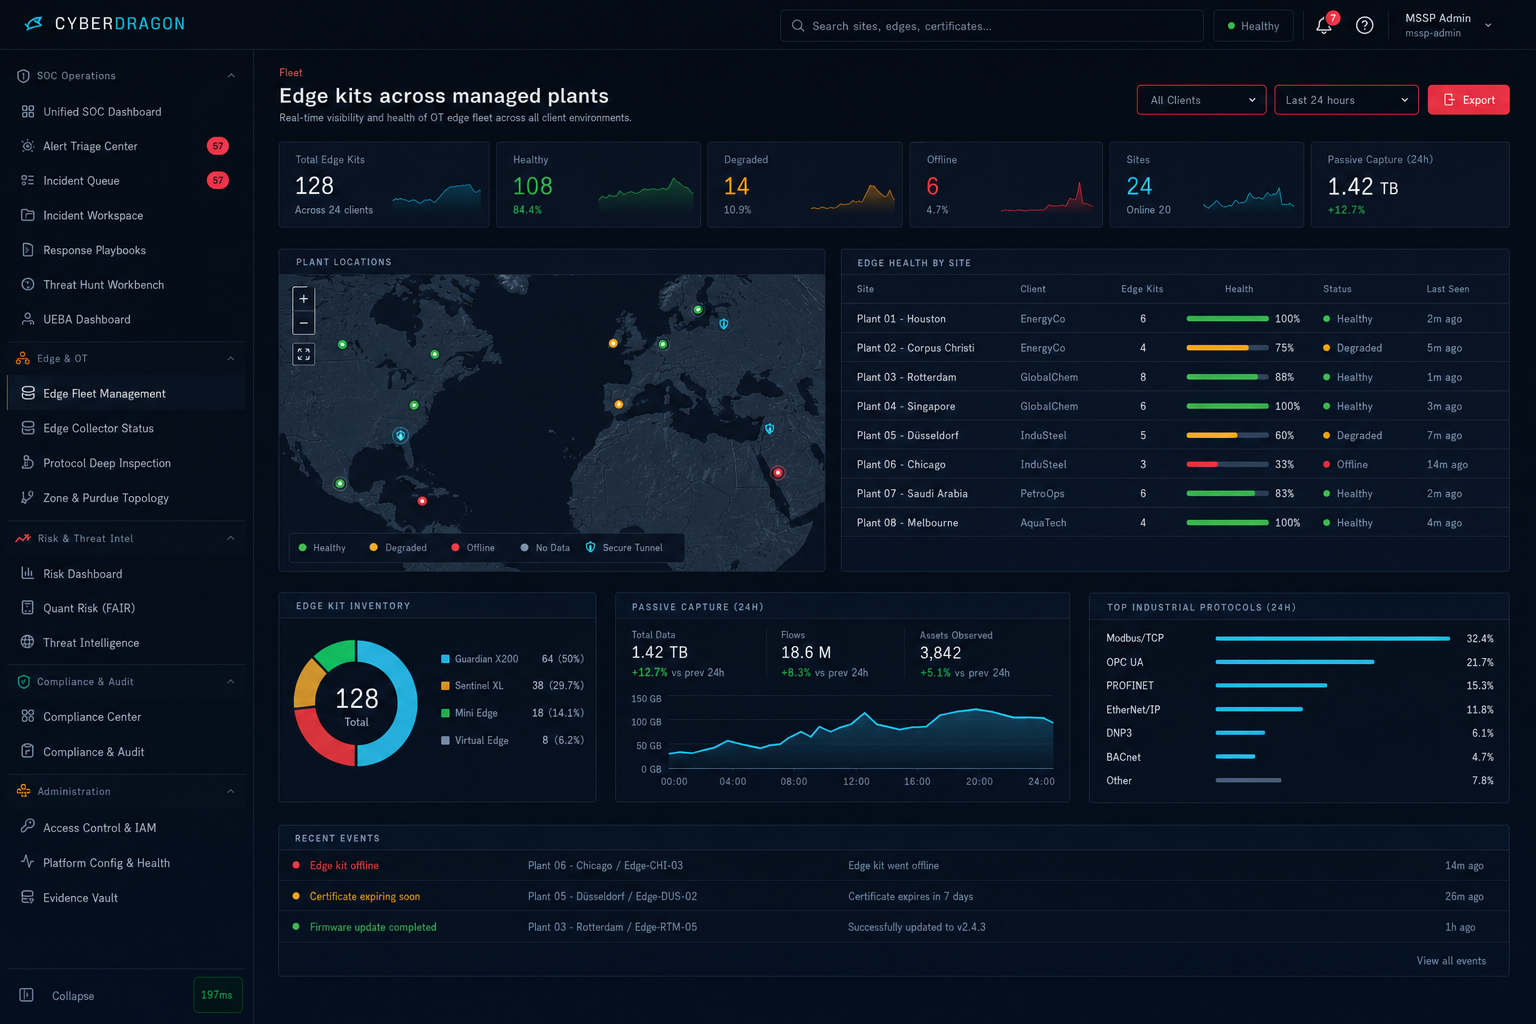
Fleet

Edge kits across managed plants

  • Roll Edge without a unique stack per industrial client.
  • Passive capture only — plant engineers will sign off.
  • SLA-friendly health and degraded states.
CyberDragon Edge fleet management dashboard
Purdue L0–L5

Industry 4.0 and classic ICS on one zone model.

Edge deploys at L3 / industrial DMZ. Telemetry flows up. Command plane into L0–L2: none.

Explore Now
Explore Now
Explore Now
Explore Now
Explore Now
Explore Now
FAQ

Frequently asked questions.

How does a MSSP deployment start?
With a 7-day free trial on the cloud tenant, then a single Edge collector at the industrial DMZ for passive capture during the Proof of Value.
Which regulations are mapped?
Client contract SLAs. Controls are auto-mapped from live events and sealed into the evidence vault for auditors.
Do we need agents on operational devices?
No. Collection is passive from a SPAN tap or hardware TAP, so no agents are installed on PLCs, RTUs, or medical and field devices.
Is CyberDragon a SIEM replacement?
CyberDragon includes an indigenous SIEM/SOAR plane and also forwards to existing SIEMs via syslog, Splunk HEC, STIX/TAXII, and webhooks.

Request a MSSP trial.

A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.