
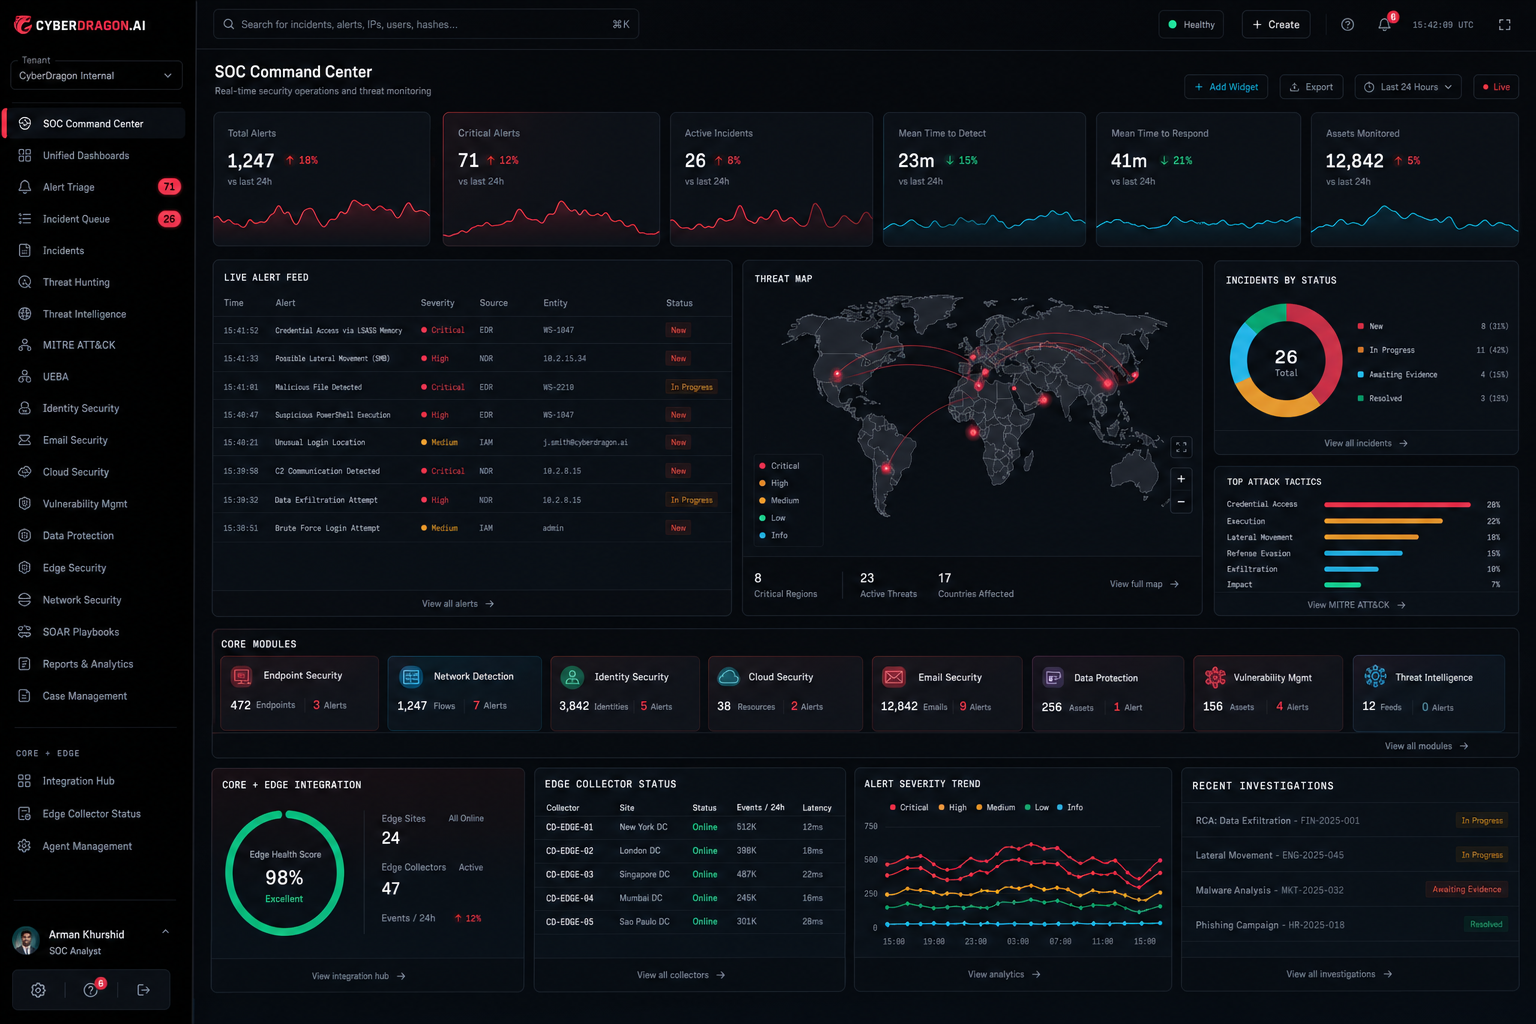
SOC
Where every Core module lands
- Live, partial, and roadmap labeled honestly on the platform page.
- Detection, risk, compliance, and identity share the same incident.
- Click a module, then come back to the operator board.
PARTIAL: a knowledge graph that connects enterprise identity, engineering hosts, and OT assets for blast-radius questions.
Neo4j-backed graph store
Cyber-physical relationships
Blast-radius queries
Hardening in progress (PARTIAL)
SOC
Neo4j-backed graph store
Cyber-physical relationships
Blast-radius queries
Hardening in progress (PARTIAL)
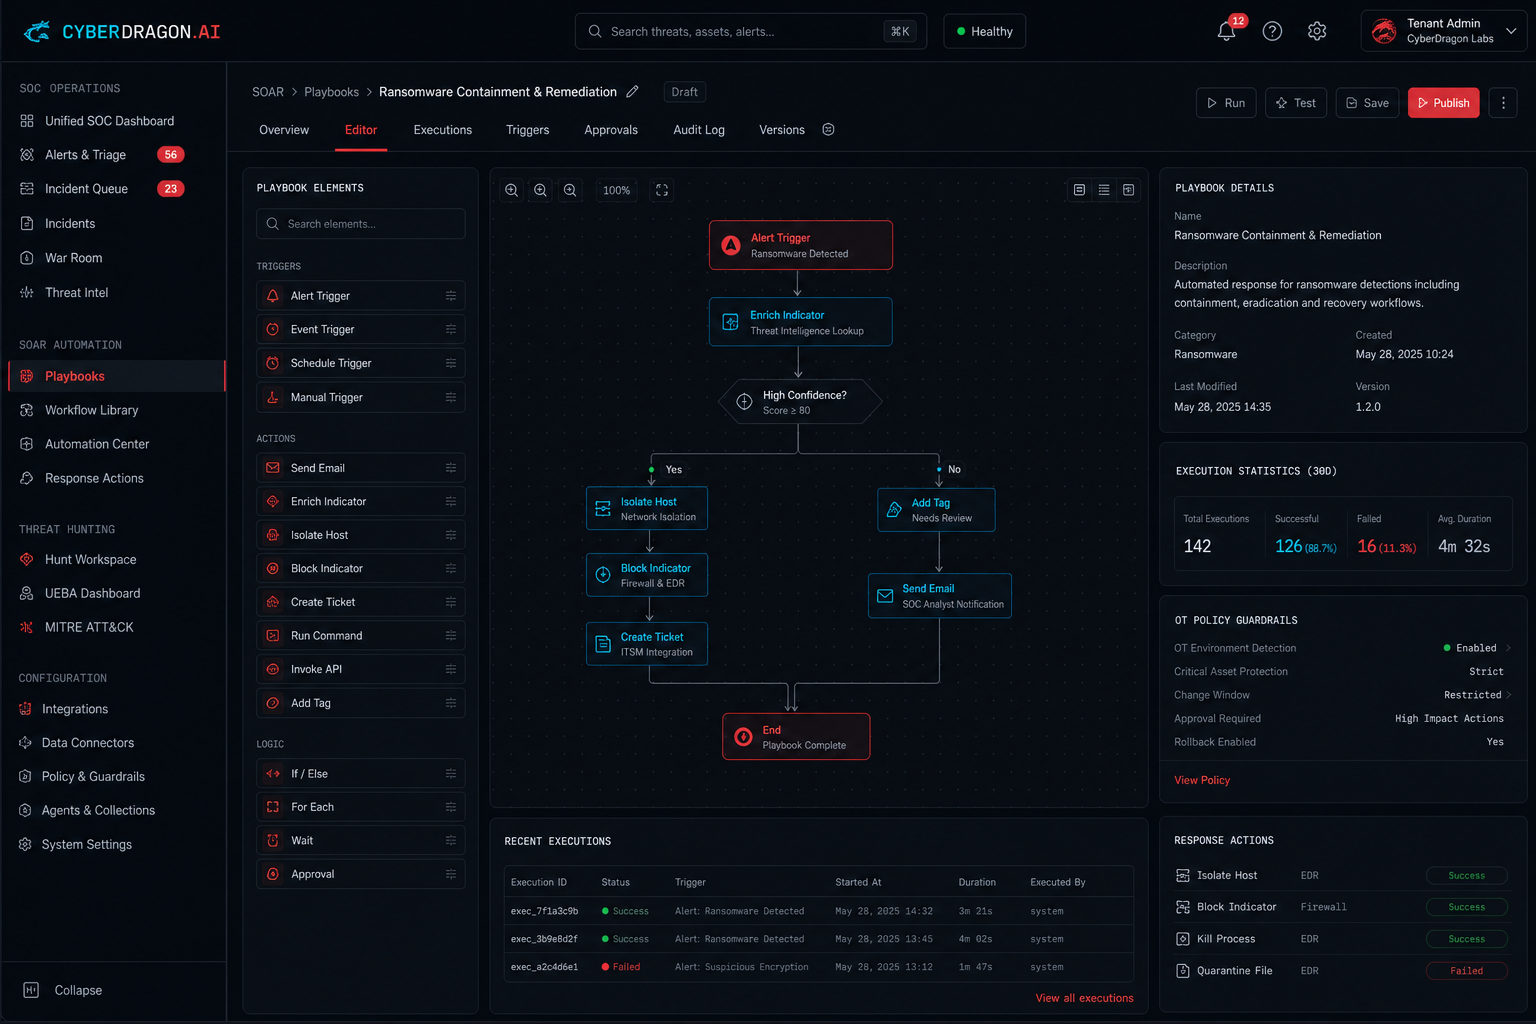
Playbooks
Neo4j-backed cyber-physical knowledge graph.
Ingest, normalize, enrich, detect, and respond on shared topics.
Passive OT capture plus syslog, HEC, and cloud telemetry.
Detections and decisions hash-chained for auditors.
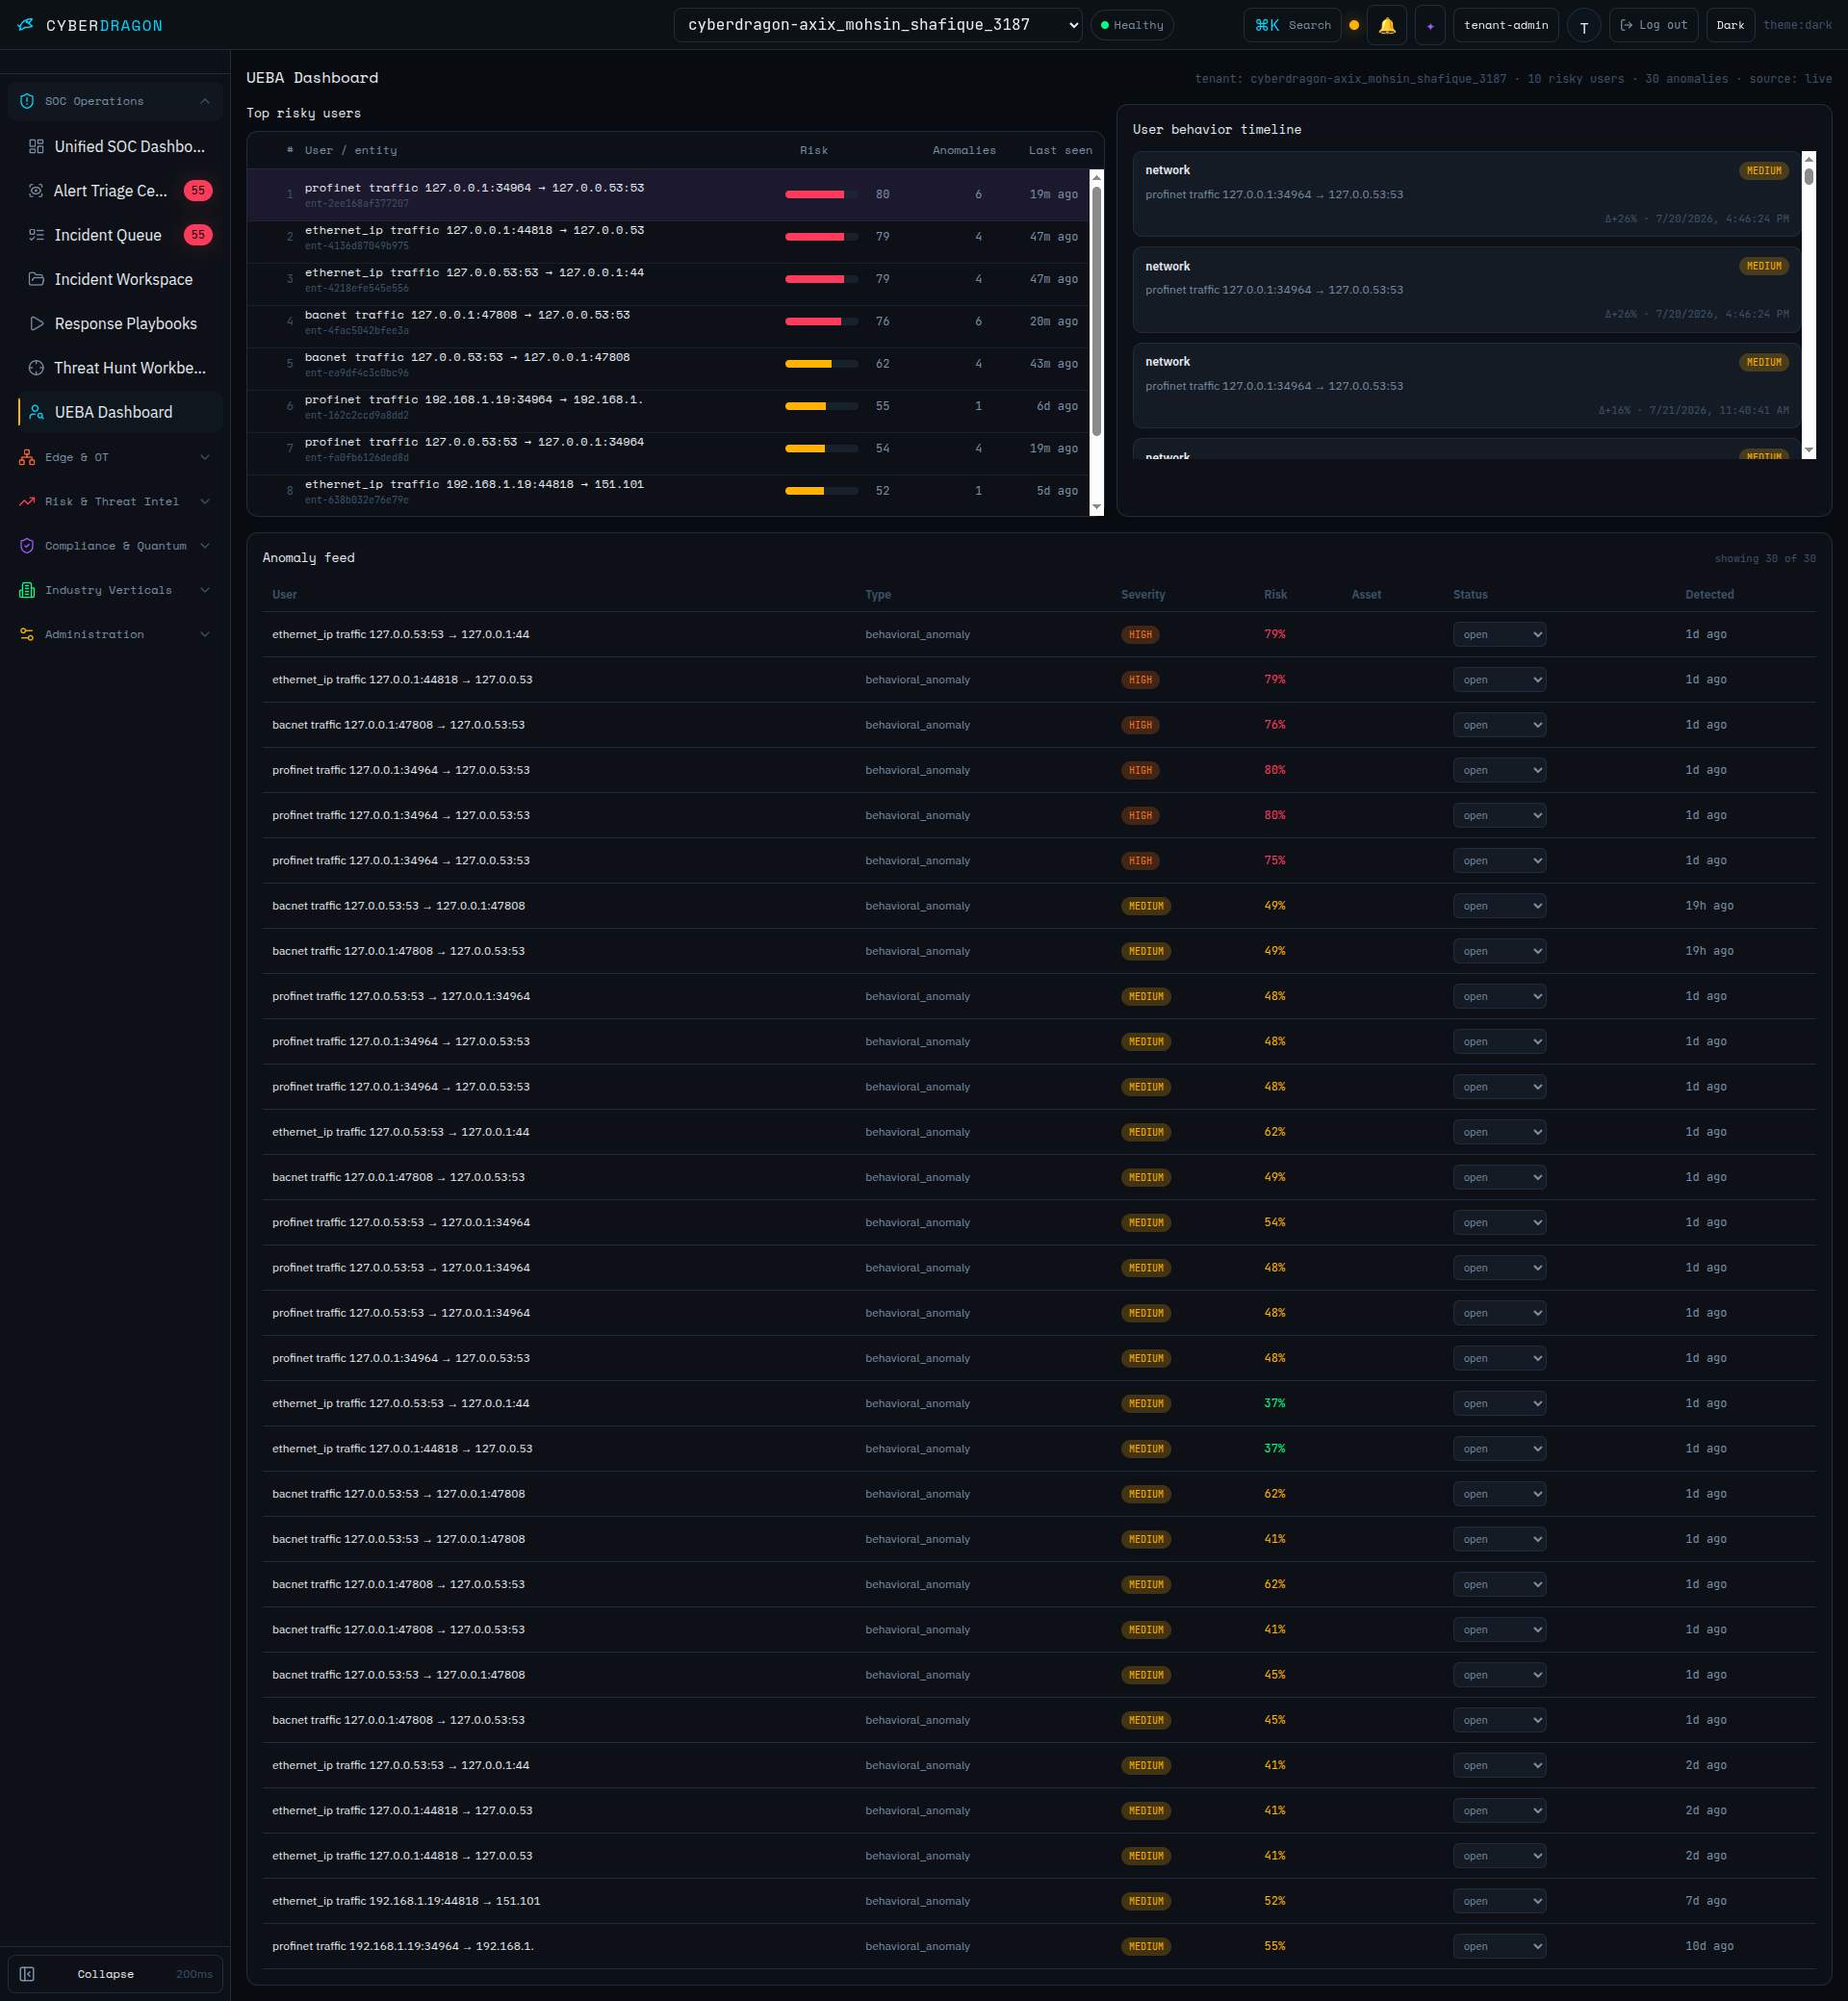
UEBA
One platform, two planes — Core control plane and Edge collector for converged IT/OT.
Kafka-backed indigenous SIEM/SOAR — ingest, detection, risk, compliance, and response.
Passive SPAN capture at the industrial DMZ — telemetry up only, no PLC agents.
Modbus, DNP3, OPC-UA, and MQTT parsed natively at Purdue L3.
Indigenous global SIEM and Temporal-orchestrated SOAR with human approval gates.
W15 / W60 / W24 cascading windows across MITRE ATT&CK and ICS tactics.
A dedicated CyberDragon tenant on your own traffic — not a slide deck. See kill-chain cyber defense on your network.